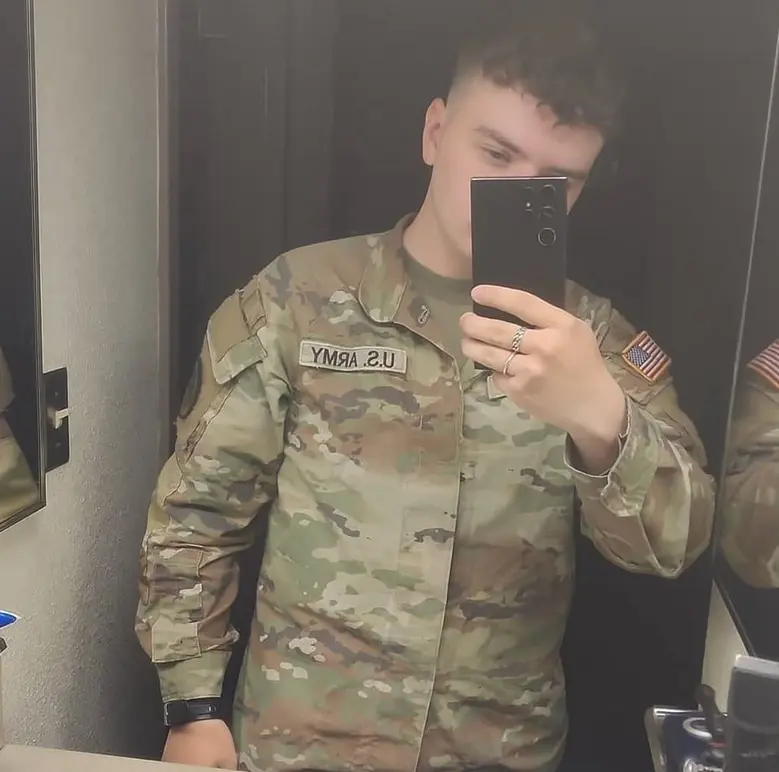
A U.S. Army soldier who pleaded guilty to hacking into multiple telecommunications companies and stealing mobile call and text metadata belonging to more than 100 million AT&T customers was sentenced to 70 months in federal prison today. In addition to the prison term, the federal court ordered him to pay nearly $300,000 in restitution to his victims, bringing a significant chapter to a high-profile international cybercrime investigation that exposed profound vulnerabilities in modern cloud data storage and telecommunications security.
Cameron John Wagenius, a 22-year-old soldier who was stationed at a U.S. Army base in South Korea at the time of his offenses, operated under the cybercriminal moniker “Kiberphant0m.” Working alongside a network of alleged co-conspirators, Wagenius exploited exposed credentials and accounts that failed to enforce multi-factor authentication (MFA) within Snowflake, a cloud data storage service utilized by several major corporate clients. Snowflake has since mandated multi-factor authentication across all accounts following the widespread security incidents.
The scope of the breaches became public in October 2024 when Wagenius brazenly bragged on various cybercrime forums about stealing the call and text metadata—including source and destination phone numbers, timestamps, and call durations—for tens of millions of AT&T customers. Operating under his Kiberphant0m persona, he claimed to have successfully infiltrated more than a dozen telecommunications companies worldwide, such as Verizon’s Push-to-Talk business, and publicly extorted these entities with threats to publish the proprietary data unless monetary demands were met.
The trail leading to his identification began to form in late November 2024, when KrebsOnSecurity published an investigative warning that the hacker operating as Kiberphant0m was likely a U.S. soldier stationed in South Korea. Less than a month after that report, Wagenius was arrested and faced two separate federal indictments. He swiftly pleaded guilty to all counts in both cases, leading up to his sentencing hearing in Seattle, where a federal judge handed down the nearly six-year prison sentence and a restitution order of $294,978.
Federal prosecutors outlined a complex web of collaboration, stating that Wagenius was assisted in his extortion efforts by Kenneth Schuchman, a 28-year-old resident of Vancouver, Washington, with an extensive and documented cybercriminal background. In 2019, Schuchman pleaded guilty to operating the Satori botnet, a vast and dangerous collection of compromised Internet-of-Things (IoT) devices that had been deployed to orchestrate large-scale distributed denial-of-service (DDoS) attacks against various internet infrastructure targets.
Other alleged co-conspirators connected to the Snowflake data thefts have also faced legal consequences. Conor Riley Moucka, operating under the alias “Judische” in Kitchener, Ontario, was arrested in 2024 and entered a guilty plea in August 2026. Meanwhile, John Erin Binns, an American citizen currently residing in Turkey, remains wanted by law enforcement for his alleged involvement in a massive 2021 data breach at T-Mobile that exposed the personal identifying information of at least 76 million customers.
As the extortion scheme evolved, Kiberphant0m’s tactics escalated to re-extorting victims and making sweeping threats to disclose classified national security secrets. Following the arrest of Moucka—and despite the fact that AT&T had already paid the extortion ring a Bitcoin ransom equivalent to $370,000—Kiberphant0m published files on hacker forums. He claimed these files contained the AT&T call logs of prominent political figures, specifically then-President-elect Donald Trump and then-Vice President Kamala Harris, alongside technical schematics allegedly stolen from the U.S. National Security Agency (NSA).
The involvement of an active-duty soldier with a security clearance immediately triggered a high-level, multi-agency federal response. Paul Russell, a resident agent in charge at the Defense Criminal Investigative Service (DCIS)—the criminal investigative arm of the U.S. Department of Defense Office of Inspector General—noted that once DCIS received intelligence regarding a soldier with secret clearance engaging in cybercrime, the agency joined forces with the FBI, the Army Criminal Investigative Division (CID), and the U.S. Secret Service.
Russell emphasized the unusual and alarming nature of the case, pointing out that discovering an active-duty service member with secret clearance actively building hacking tools and trafficking stolen data is an exceedingly rare occurrence. The revelation immediately mobilized partner organizations, creating an atmosphere of urgency because the insider threat presented unique security unknowns from the very beginning of the investigation.
Despite his cooperation with authorities following his arrest, Wagenius continued to draw scrutiny from law enforcement while incarcerated and awaiting sentencing. According to a sentencing memo filed on September 19 by federal prosecutors in Seattle, Wagenius violated the computer use policies of the Bureau of Prisons (BOP) in an attempt to probe the vulnerabilities of BOP computer systems.
The government’s memo revealed that in or around September 2025, Wagenius utilized another inmate’s email system to instruct an external recipient to prompt a commercial artificial intelligence tool. Specifically, he sought information regarding Windows 10 Enterprise privilege escalation, bypass methods, and specific Common Vulnerabilities and Exposures (CVEs) accompanied by real-world working scripts without omitted code.
Less than a week later, Wagenius reportedly used a different inmate’s email account to request step-by-step instructions and potential code for CVE-2023-45208, a three-year-old command injection vulnerability affecting D-Link networking devices. During the same month, he allegedly asked the email recipient to research how to construct a makeshift antenna using prison commissary items or readily available tools to extend radio reception. Federal prosecutors also noted that Wagenius requested research regarding methods for escaping a correctional facility.
To bypass safety controls built into commercial AI models designed to prevent the generation of malicious exploit code, Wagenius framed his queries as research for a book he claimed to be writing. Prosecutors identified this technique as a textbook example of "prompt injection," wherein attackers feed deceptive inputs into AI tools to circumvent restrictions against outputting dangerous code. Although the government stated it found no evidence that Wagenius successfully deployed these researched vulnerabilities within BOP systems—and Wagenius claimed he was merely looking for potential flaws to report to the prison—the incidents underscored his persistent fixation on cybersecurity exploits.
In a striking contrast to the massive volume of data he managed to access, the financial return from Wagenius’s cybercriminal enterprise was remarkably low. Court documents revealed that despite compromising the data of over 100 million individuals and targeting prominent telecommunications giants, Wagenius earned a total of only about $1,500 from selling stolen data.
Concluding their assessment in the sentencing memo, federal prosecutors underscored the dichotomy between his financial gains and the far-reaching consequences of his actions, noting that while Wagenius was not particularly successful as a profit-driven cybercriminal, he clearly intended to cause—and ultimately did cause—substantial harm to numerous individual victims, major U.S. corporations, and the national security apparatus of the United States.