A teenager from Amman, Jordan, suspected of acting as a leading force behind the prolific data theft and extortion syndicate known as ShinyHunters, has been detained by local authorities and is reportedly cooperating with the Federal Bureau of Investigation (FBI) to identify other members of the hacking collective.
According to reports from KrebsOnSecurity, the suspect—who operates online under the hacker handle “Rey”—was taken into custody just as the hacking group was in the active process of extorting a business unit recently divested by global aerospace giant Boeing. Notably, Boeing manufactures the aircraft fleet utilized by the primary employer of Rey’s father, Royal Jordanian Airlines.
The detention follows a series of escalating international law enforcement actions targeting the loose-knit cybercrime network. On October 3, Reuters cited three unnamed sources confirming that a suspected ShinyHunters member in Amman named Saif Al-din Khader had been detained by Jordanian authorities and was actively assisting the FBI. KrebsOnSecurity had previously identified Rey as Khader in a November 2025 profile, during which the young man admitted to collaborating with multiple ransomware operations.
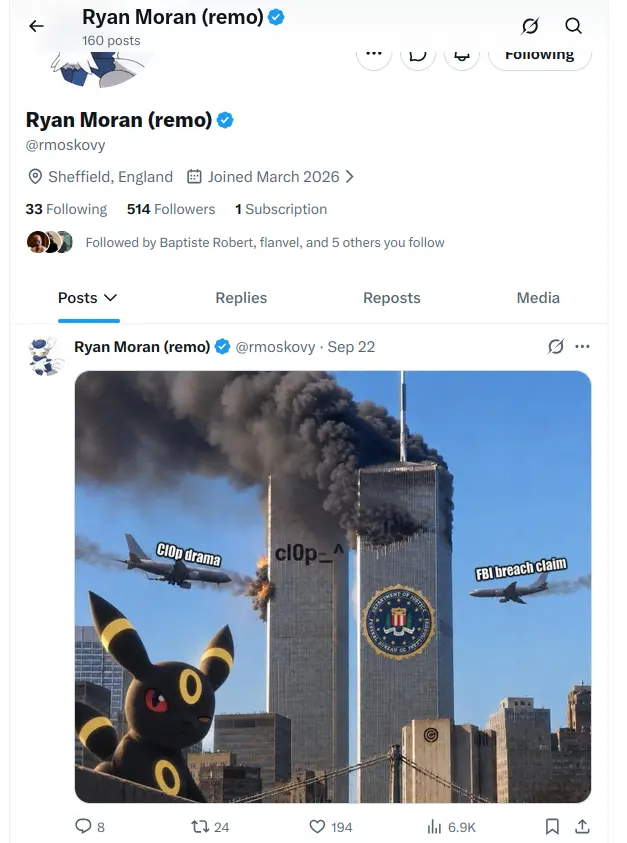
Rey’s activities drew renewed scrutiny following an exclusive September 28 report detailing the arrest of 24-year-old convicted Dutch cybercriminal Pepijn van der Stap by police in the Netherlands. Van der Stap is suspected of aiding ShinyHunters in their data theft and extortion schemes. Immediately following the dramatic Dutch police raid on the evening of September 15, Rey seized control of the ShinyHunters brand, publicly boasting about breaching the FBI and extorting the notorious Cl0p ransomware syndicate.
Using his long-standing account on Twitter/X, Rey taunted both federal law enforcement and the Cl0p group with memes. In a calculated move to frame the newly arrested Dutchman, Rey included images of the avatar used by Van der Stap’s former hacker alias, “Umbreon,” alongside his taunting posts.
The security failures exploited by the group trace back to a critical vulnerability, tracked as CVE-2026-35273, within PeopleSoft—a software-as-a-service platform developed by Oracle that is widely deployed across enterprises for human resources, payroll, and benefits management. Although Oracle rapidly issued a security patch after ShinyHunters began weaponizing the vulnerability as a zero-day exploit in June, and Mandiant subsequently released web application firewall (WAF) rules for organizations unable to immediately patch, the actors persisted.

According to statements made by the hackers to BleepingComputer in June, the initial objective behind targeting PeopleSoft was to breach the FBI’s internal databases, though those early attempts were reportedly unsuccessful. In the weeks leading up to the recent arrests, however, ShinyHunters managed to bypass Mandiant’s recommended WAF rules by employing a well-known URL-encoding trick.
A joint threat intelligence report released on September 25 by Mandiant and the Google Threat Intelligence Group confirmed that the group had mass-exploited the PeopleSoft vulnerability. The campaign compromised dozens of systems across a diverse array of sectors, including higher education, technology, healthcare, agriculture, transportation, and government agencies.
Further compounding the fallout, Reuters reported on October 5 that the FBI dismissed an Accenture contractor due to their failure to patch the compromised FBI recruitment portal. The breach exposed sensitive personal and professional data belonging to more than 5,000 bureau personnel, including specific unit assignments, specializations, and confidential medical and psychiatric records.
‘Rey’ Means King, as in Royal
According to two sources close to the international investigation into ShinyHunters, a digital aviation and navigation unit recently divested by Boeing was among the primary targets undergoing active extortion when Jordanian law enforcement apprehended Rey.
Investigators confirmed that the FBI’s pursuit of the hacking group gained significant urgency following the attempted extortion of the former Boeing division. Officials feared that the sensitive proprietary information stolen during the breach could introduce substantial operational safety and security risks.
In a brief statement provided to KrebsOnSecurity, Boeing acknowledged the ongoing extortion threats, confirming that the incident involved data stolen from Jeppesen ForeFlight. Boeing sold this subsidiary in November 2025 to private equity firm Thoma Bravo for $10.55 billion.

"We are aware of claims by a threat actor regarding data allegedly associated with Boeing and our former subsidiary Jeppesen ForeFlight," a Boeing spokesperson stated. "Estamos actively reviewing the matter with the Jeppesen ForeFlight team."
A representative for Jeppesen ForeFlight maintained that their internal systems remained insulated from the breach. "Based on our investigation to date into this claim and proactive security posture, there was no impact to our operations or products," the company said in a written statement.
Rey’s suspected role in targeting the former Boeing subsidiary carries additional weight due to compelling evidence linking his father to Royal Jordanian Airlines. The airline, primarily controlled by the Jordanian government, operates long-haul flights exclusively utilizing Boeing passenger aircraft. While Rey claimed on Telegram in early 2025 that his father worked as an airline pilot, that specific detail could not be independently verified.
However, forensic analysis from a November 2025 profile of Rey revealed that a shared family computer had been compromised by password-stealing malware. Data extracted from the malware logs demonstrated that Rey’s father utilized identical login credentials across multiple administrative portals designated for Royal Jordanian Airlines employees.
Royal Jordanian Airlines did not respond to requests for comment regarding the security compromise. Prior to the publication of the September 28 report, investigators reached out directly to Rey’s father to apprise him of his son’s alleged criminal activities. Neither of the Khaders responded to the inquiry. Within hours of the message being sent, however, Rey began systematically purging his social media footprint, deleting the Twitter/X profiles he had previously used to mock law enforcement and corporate victims.
Despite the social media scrub, Rey’s technical blog hosted on GitHub remained online. The repository features a detailed investigation published in March 2026 that attempts to unmask two Russian men as the core developers and masterminds behind the Cl0p ransomware operation.

Murder-for-Hire Allegations
While investigators focus on the digital extortion ring, Dutch media outlets have surfaced explosive new allegations concerning Pepijn van der Stap. Despite widespread public narratives celebrating his purported transformation from a convicted cybercriminal to a reformed security professional, Dutch daily RTL reported on September 29 that authorities suspect Van der Stap attempted to orchestrate at least two murders abroad.
Van der Stap had recently completed the majority of a four-year prison sentence for extensive data theft and extortion crimes that prosecutors estimated netted between 1.5 million and 2.7 million euros. During a September 9 interview, Van der Stap presented himself as the "offensive security lead" at Neo Security, a Dutch cybersecurity firm where he purportedly tested client network defenses.
Neo Security owner Benjamin Korper informed Reuters that an independent auditing firm was retained to investigate whether Van der Stap had compromised the company or its clients, though no evidence of internal malicious activity has emerged. Korper noted that Dutch forensic teams descended on his offices on September 15 during the dramatic police raid that resulted in Van der Stap’s arrest, which reportedly utilized flash-bang grenades.
Before his initial 2023 arrest, Van der Stap worked as a software engineer for Hadrian, an Amsterdam-based security startup, while volunteering for the Dutch Institute for Vulnerability Disclosure. This dual life allowed him to maintain access to corporate networks even as he orchestrated extortion campaigns against major organizations.
When questioned about how the public could trust a self-described reformed hacker with a history of deception, Van der Stap expressed resignation. "You can throw a bunch of nice words at someone, but you can’t convince them if they don’t want to be convinced," he said. "I’m doing what I can to repay victims, and that’s all I can do."
Franchising and Burning a Brand
Cybercriminals associated with the ShinyHunters banner have been linked to dozens of major data breaches resulting in the exposure of billions of records since 2019. Security researchers emphasize, however, that the individuals currently operating under the moniker bear little relation to the group’s original core members, most of whom are French citizens who have previously faced arrest and prosecution.

Instead, ShinyHunters has evolved into a fractured franchise model. Analysts compare the succession mechanism to the Dread Pirate Roberts persona from popular culture, where arrests continuously prompt new operators to step into the vacancy. Law enforcement is increasingly turning its attention toward freelance affiliates who trade stolen SaaS credentials in exchange for a percentage of ransoms paid by corporate targets.
Following the news of Van der Stap’s arrest, a Telegram chat server reportedly managed by Rey erupted in criticism. Peers ridiculed the teenager after he backed down from threats directed at the FBI and Cl0p, particularly as the ShinyHunters darknet portal abruptly went offline following an FBI deadline. Observers accused Rey of purchasing historical forum PGP keys to impersonate the defunct collective for personal financial gain.
"He bought the old forum PGP key and used it to make new Breachforum websites and Telegram channels larping as ShinyHunters to ransom companies and then sell the used data or resell his forum when he goes broke," one community member observed.
A competing Telegram channel named "The Battle" has systematically targeted Rey and other alleged affiliates, characterizing Rey as an inexperienced novice seeking to exploit an infamous cybercrime brand. "Rey (Saif Al-Din Khader) made a serious mistake when he started pretending to be a member of ShinyHunters," the channel’s administrators posted. "That group had already been dismantled… yet Rey still chose to use its name while carrying out his crimes."
In a prior interview with industry publication The Register, representatives for the active iteration of ShinyHunters claimed their decision to target the FBI was designed to challenge a public safety advisory issued by the agency in May. That advisory explicitly warned organizations against paying ransoms to the group and detailed aggressive tactics, including threatening phone calls, text messages, swatting incidents, and false claims regarding the publication of sensitive personal media.
While the hackers asserted that breaching federal infrastructure served to demonstrate their technical capabilities and counter agency narratives, they ultimately conceded that the intense law enforcement focus severely hampered their commercial prospects. For an enterprise reliant on victim compliance, the publicity surrounding the raids and subsequent cooperation agreements has effectively burned the brand.