Authorities in the Netherlands have arrested a 24-year-old convicted cybercriminal on suspicion of aiding data thefts and extortion campaigns orchestrated by the prolific and aggressive hacker group ShinyHunters. The high-profile arrest has sent shockwaves through the underground cybercrime community, triggering a dramatic and volatile escalation from the remaining members of the collective. In the immediate wake of the suspect’s detention, ShinyHunters launched high-profile retaliatory attacks, including a devastating breach of the FBI’s recruitment portal and aggressive digital extortions targeting the notorious Russian ransomware syndicate Cl0p.
According to three sources familiar with the matter, the individual taken into custody by Dutch law enforcement this month is Pepijn van der Stap, a previously convicted cybercriminal residing in Almere and Lelystad in the Netherlands. Van der Stap’s legal troubles are well-documented; he was convicted in late 2023 for a widespread campaign of data thefts and cyber extortions. Prosecutors at the time estimated that his illicit operations generated between €1.5 million and €2.7 million in illicit proceeds.
During his 2023 trial, van der Stap offered a candid admission of his dual existence, describing a life akin to Dr. Jekyll and Mr. Hyde. By night, he operated under the hacker handle "Umbreon," using English-language cybercrime forums—including the now-defunct RaidForums and Breached—to extort victims and publish sensitive databases. By day, however, van der Stap maintained a legitimate professional profile as a software engineer at Hadrian, an Amsterdam-based cybersecurity startup. He also dedicated his time to volunteering with the Dutch Institute for Vulnerability Disclosure (DIVD), a well-known nonprofit security research organization dedicated to finding and responsibly reporting software flaws.
Van der Stap confessed openly to his role in the data thefts and extortion rings during legal proceedings. Ultimately, he was sentenced to four years in prison, with one year suspended. In a peculiar twist during his trial, van der Stap requested to remain in custody rather than return home, arguing that he could not find adequate medical and psychological support outside prison walls for his ongoing struggles, which he attributed to post-traumatic stress disorder stemming from childhood trauma. He was subsequently released from prison in December 2025.
In an interview with KrebsOnSecurity on September 9, 2026, van der Stap portrayed himself as a completely reformed individual striving to turn his life around and make positive contributions to society. At the time of the interview, he was employed as an offensive security lead at Neo Security, a Dutch cybersecurity firm that has since declined to comment on the arrest. Van der Stap noted during the conversation that he was still actively dealing with civil lawsuits, restitution demands, and the legal fallout from his past cybercrimes, insisting he was doing everything in his power to make amends. However, shortly after that interview, van der Stap abruptly ceased all communication, failing to reply to messages from reporters and associates alike over a two-week period.
Sources with direct knowledge of the investigation confirmed that van der Stap was arrested by Dutch authorities on or around September 16 and has since been held in custody for questioning. A local source reported that a colleague personally witnessed law enforcement officers removing boxes and hardware from van der Stap’s residential property during the raid.
The arrest marks a major escalation in a sweeping Dutch investigation into ShinyHunters. Earlier in September, law enforcement in the Netherlands made a public appeal for assistance in identifying a native Dutch speaker whose voice was recorded during a February 2026 phone call. In that call, a ShinyHunters operative used sophisticated social engineering techniques to trick an employee of Odido—the country’s largest mobile telecommunications provider—into logging into a spoofed website. The attackers leveraged that unauthorized access to siphon sensitive data concerning more than 6.2 million Dutch citizens.

Reacting to local news coverage, representatives of ShinyHunters publicly confirmed that the individual heard in the leaked audio recording is indeed a member of their collective. In a statement provided to the NL Times, the group vowed unwavering support for their detained associate. "Our team member has our full support—emotionally, mentally, and financially," the hackers declared. "Everything has been arranged, including a criminal defense lawyer. We do not look down on our staff and members; we take excellent care of them."
The collective also hurled insults at Dutch law enforcement. "The Dutch police will need all the luck in the world—and everyone’s prayers—if they want to catch him before we carry out another large-scale data theft in the Netherlands," the statement read. "Frankly, the Dutch police are a big joke; they are incapable of doing anything. Incompetent. Irrelevant. Unimportant. Useless."
Following the arrest, the Dutch police officially confirmed they were holding a 24-year-old man in connection with the ongoing ShinyHunters investigation. Authorities announced that the suspect would appear before the chambers of the Rotterdam District Court. Meanwhile, investigative reports in Dutch media outlet RTL revealed that investigators are also examining whether van der Stap attempted to orchestrate at least two murders abroad, allegedly issuing direct orders for the killings.
FBI, CL0P HACKS
Just days after van der Stap was detained, ShinyHunters claimed responsibility for an extraordinarily brazen cyberattack targeting the FBI’s job application portal at apply.fbijobs.gov. According to reporting from 404 Media and Reuters, the compromised data included Social Security numbers and detailed personal information belonging to more than 5,000 current and prospective FBI officials.
The stolen files contained sensitive professional details, including job titles and team assignments across high-stakes departments such as special agents, threat intake examiners, the major cybercrimes units, and personnel tasked with investigating state-sponsored foreign cyber threats. Furthermore, Reuters reviewed documents shared by the hackers that revealed deeply personal psychiatric and medical files belonging to FBI personnel. The bureau subsequently issued a brief public statement acknowledging the unauthorized compromise of the job portal.
Security analysts uncovered that ShinyHunters gained access to the FBI site—alongside numerous other corporate and government networks—by exploiting a critical zero-day vulnerability tracked as CVE-2026-35273 within Oracle PeopleSoft. PeopleSoft is a widely utilized software-as-a-service platform relied upon by major institutions globally for human resources, recruitment, payroll, and benefits administration. Although Oracle quickly patched the vulnerability after ShinyHunters began mass-exploiting it in June, and Mandiant issued web application firewall (WAF) mitigation rules for organizations unable to immediately patch, the cybercriminals successfully bypassed these defenses. Security reporting from BleepingComputer revealed that ShinyHunters utilized a clever URL-encoding technique to circumvent Mandiant’s WAF mitigation rules.
A joint threat intelligence report released on September 25 by Mandiant and the Google Threat Intelligence Group confirmed that ShinyHunters weaponized the PeopleSoft flaw to steal data from dozens of organizations across diverse sectors, including higher education, technology, healthcare, agriculture, transportation, and government.

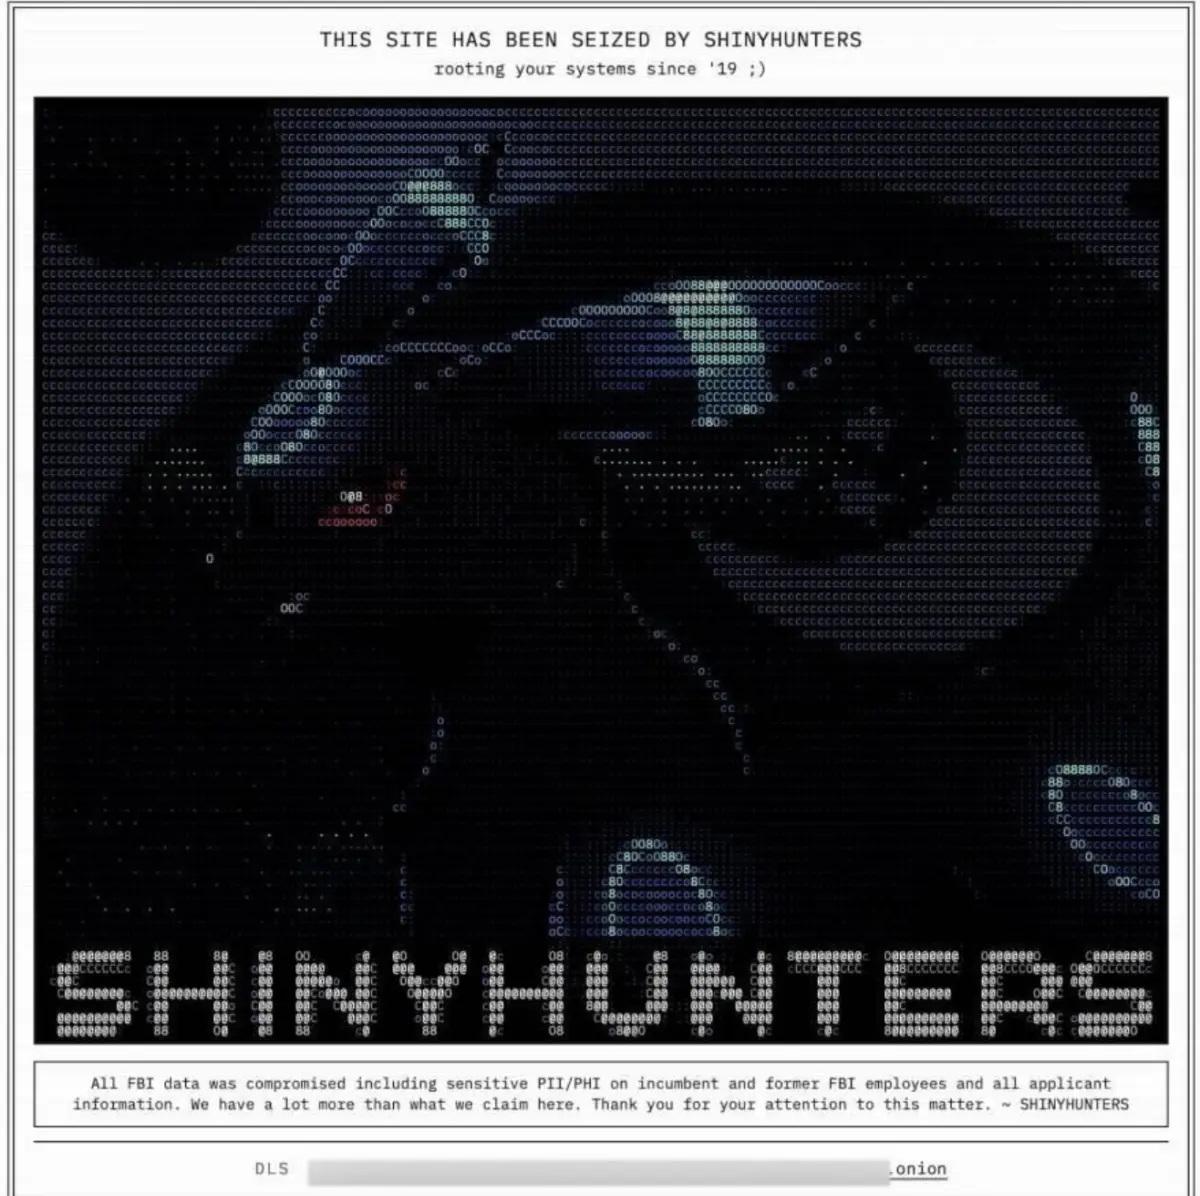
Intriguingly, van der Stap’s former hacker alias, "Umbreon," appeared hidden in plain sight across the digital footprints left by ShinyHunters during the FBI breach. The defacement image posted on the compromised FBI recruitment site featured an ASCII art rendering of the Pokémon character Umbreon, accompanied by the taunting header: "This site has been seized by ShinyHunters. rooting your systems since ’19 ;)." The visual layout bore a striking resemblance to a defacement banner deployed by ShinyHunters during their 2020 hack of the English-language cybercrime forum Hackforums.
Sources close to the ongoing investigation indicate that the group’s sudden pivot toward high-risk targets like the FBI and a major Russian ransomware faction represents a dramatic shift in operational philosophy. This volatile change in behavior reportedly followed an internal power struggle within ShinyHunters, which was taken over by a teenage cybercriminal from Amman, Jordan. Operating under the online handle "Rey," the young hacker belongs to a syndicate known as ScatteredLapsussHunters (SLSH)—an amalgamation of three notorious cybercrime brands: Scattered Spider, LAPSUS$, and ShinyHunters.
According to insider accounts, Rey held a personal grudge against the Dutch hacker regarding control over the ShinyHunters brand and its vast repositories of stolen data. Investigators believe that prominently featuring the Umbreon Pokémon imagery in the FBI site defacement was a deliberate attempt by Rey to frame van der Stap for the attack.
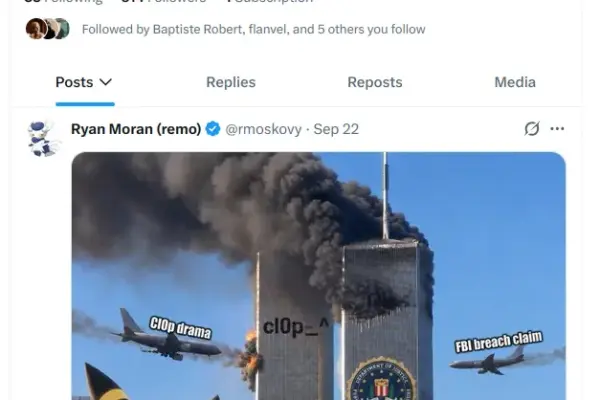
Rey was first publicly unmasked by cybersecurity firm KELA in March 2025. During subsequent inquiries by KrebsOnSecurity, Rey’s father—an employee of Royal Jordanian Airlines—forwarded media interview requests directly to his son. The teenager acknowledged participating in ransomware operations while simultaneously claiming he was attempting to extricate himself from the SLSH collective. Following news of the FBI breach, Rey’s primary account on X (formerly Twitter) engaged in extensive taunting, posting inflammatory memes targeting both the FBI and the Cl0p ransomware group before the account was ultimately deleted.
Underpinning the animosity between SLSH and ShinyHunters is a disputed partnership forged earlier in the year. According to an investigative report by Wired, ShinyHunters and SLSH members briefly collaborated to monetize credentials gathered by TeamPCP, an upstart supply-chain hacking group that successfully compromised software code repositories but struggled to convert stolen access into financial profit.
In reality, Mandiant analysts had secretly infiltrated TeamPCP and were quietly feeding compromised credentials to major cloud infrastructure providers like Amazon and Microsoft, allowing them to rapidly invalidate the stolen keys. As the stolen access burned out, the allied cybercrime factions turned on one another in mutual suspicion. Wired reported that ShinyHunters ultimately went rogue, executing independent extortion schemes using TeamPCP credentials without sharing profits with the supply-chain hackers.
Despite the mounting legal pressures and internal infighting, security researchers estimate that ShinyHunters has generated massive profits through extortion throughout the year, remaining on track to pull in nearly $100 million in ransom payments by the end of 2026.

For his part, van der Stap consistently maintained that financial gain was never his primary driver. In interviews following his initial arrest, he insisted his cybercriminal endeavors stemmed from an obsessive compulsive drive to assemble the world’s most comprehensive collection of stolen databases. "The hacking was very easy for me, and it wasn’t a compulsion," van der Stap told Bloomberg in 2024. "My habit was collecting. Collecting data, organizing data, downloading data, creating folders."
Meanwhile, the nonprofit DIVD addressed an internal cybersecurity incident involving the potential malicious use of artificial intelligence. While the organization disclosed few details regarding the breach, a DIVD spokesperson confirmed that the incident bore no connection to ShinyHunters and showed no ties to any former volunteers.
Law enforcement agencies internationally have signaled that the net is tightening around the remaining members of the collective. Brett Leatherman, assistant director of the FBI’s cyber division, released a direct video message thanking Dutch authorities for their pivotal assistance and warning the remaining members of ShinyHunters that time is running out.
"Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who’s left," Leatherman stated. "The longer you stay in this, the more we learn about you. You know how to find us, and we know how to find you. I suggest you reach out to us while the choice is still yours."