Federal Bureau of Investigation agents have arrested a high-ranking executive at a Canadian cybersecurity firm in connection with an escalating international investigation into the notorious ShinyHunters hacking collective—a group that recently breached federal systems and relieved the bureau of sensitive data pertaining to thousands of law enforcement agents.
According to multiple sources speaking with KrebsOnSecurity, the arrest took place in Pennsylvania and targeted a Canadian professional whose work intersects with corporate cyber extortion, ransomware negotiations, and incident response.
The New York Times first reported the apprehension of the Canadian man on suspicion of providing assistance to the ShinyHunters operation. While neither the initial Times report nor a public statement published on social media by FBI Director Kash Patel identified the suspect by name, court records and industry sources have since linked the detention to Edward Dubrovsky, a prominent figure in the Canadian cybersecurity landscape and the author of a book on cyber extortion response strategies.
Sources close to the ongoing federal investigation revealed that the suspect had traveled to Pennsylvania to attend a prominent cyber insurance conference. The event in question, the annual Cyber Risk Summit, was hosted at the Loews Philadelphia Hotel. According to publicly available event records and sponsor listings, the conference drew numerous industry leaders, with a Canadian security firm known as Cypfer listed as its primary corporate sponsor.

Further corporate mapping via professional networking platforms indicates that Dubrovsky was historically tied to Cypfer. While his online profiles previously described him as an ex-founder of the organization, a Cypfer spokesperson subsequently clarified that Dubrovsky actually served as a managing director before ultimately resigning from his post in December 2025. Following his departure, Dubrovsky became affiliated with another Canadian security enterprise and conference sponsor, CyberSteward. Approximately a month prior to his arrest, Dubrovsky had shared posts on professional channels indicating his intention to travel to the Philadelphia summit alongside his new colleagues to discuss global strategies for handling coercive cyber threats, extortion advisories, and ransom negotiations.
Federal court documentation filed in Pennsylvania shows that an individual matching the suspect’s identity—under the slightly misspelled name Edward Dobrovsky—was formally charged with cyber extortion and conspiracy offenses. Although several core case files, including the primary criminal complaint, remain sealed from public view, a series of documents indexed on legal research platforms outline the severity of the allegations. The available summaries charge the defendant with conspiracy to threaten the impairment of information confidentiality with the explicit intent to extort money, alongside charges related to interference with commerce through threats.
U.S. Bureau of Prisons inmate locator data initially placed a 54-year-old Edward Dubrovsky inside a federal detention facility in Philadelphia. However, legal filings indicate that the case was swiftly transferred to the Eastern District of Texas. According to individuals familiar with the multi-jurisdictional inquiry, the Texan federal field office has recently been designated as the centralized hub and epicenter for the expansive government investigation into the ShinyHunters syndicate. The FBI has declined to provide formal comment on the ongoing proceedings.
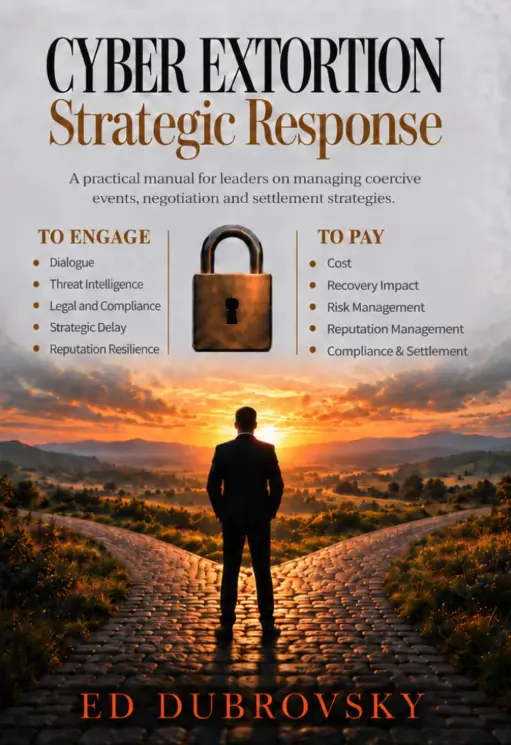
Dubrovsky is widely known within cybersecurity circles for his expertise in navigating the complex landscape of digital extortion. He penned a 252-page professional volume titled Cyber Extortion Strategic Response, which is marketed as a guide designed to help organizational leaders make critical decisions during ransomware incidents. A recurring theme in Dubrovsky’s published writings centers on the vital distinction between open communication with cybercriminals and the actual disbursement of extortion payments. His work argues that opening a dialogue with threat actors does not equate to a commitment to pay ransoms, suggesting instead that engagement can be utilized to vet attacker claims, buy time, gather actionable intelligence, and preserve strategic options.
At the time of reporting, Dubrovsky could not be reached for immediate comment, and representatives from CyberSteward had not yet issued public statements regarding the arrest. Court documentation indicates that the defendant has not yet secured private legal representation or been assigned a public defender by the court system.

The ShinyHunters organization has long operated as one of the cybercrime ecosystem’s most persistent and disruptive threats. The group typically relies on sophisticated phishing campaigns and stolen credential sets to infiltrate corporate networks and software-as-a-service platforms, siphoning massive volumes of proprietary and confidential data. They routinely leverage the threat of publicly releasing this stolen material to pressure victims into meeting exorbitant financial demands. According to federal estimates, the syndicate has successfully extorted upward of $70 million from corporate and institutional victims over the course of the year.
The apprehension in Pennsylvania represents the latest milestone in a rapidly intensifying international sweep targeting the cybercrime ring. Federal investigators have reportedly spent weeks combing through digital devices seized during a late-September operation by Dutch law enforcement. That operation resulted in the arrest of Pepijn van der Stap, a reformed hacker and convicted cybercriminal whose activities drew the attention of investigators probing the ShinyHunters network. Law enforcement sources suggest that these ongoing forensic examinations could lead to additional criminal charges against principals at other firms that specialize in intermediary ransomware negotiation services.
The pressure on the hacking collective has mounted sharply following a series of high-profile confrontations with law enforcement. Immediately following the arrest of Van der Stap, an operative within ShinyHunters operating under the alias "Rey" assumed de facto leadership of the group. In an audacious display of defiance, Rey began taunting federal authorities online after the group successfully breached and exfiltrated sensitive information from an online recruitment portal maintained by the FBI itself. The compromised files reportedly contained personal data detailing individual agents’ specific units, specialized areas of training, and confidential medical and psychiatric records.
International reporting subsequently revealed that the operative known as Rey was actually a teenager named Saif Al-din Khader. Authorities successfully detained Khader, who has reportedly begun cooperating with federal investigators. The operational breakthrough came to light as the group attempted an extortion scheme targeting a digital aviation and navigation unit that had recently been spun off by Boeing.
As federal authorities continue to untangle the web of facilitators, negotiators, and hackers connected to the ShinyHunters enterprise, the investigation remains active and fluid, with further developments expected as the case progresses through the federal court system in Texas.