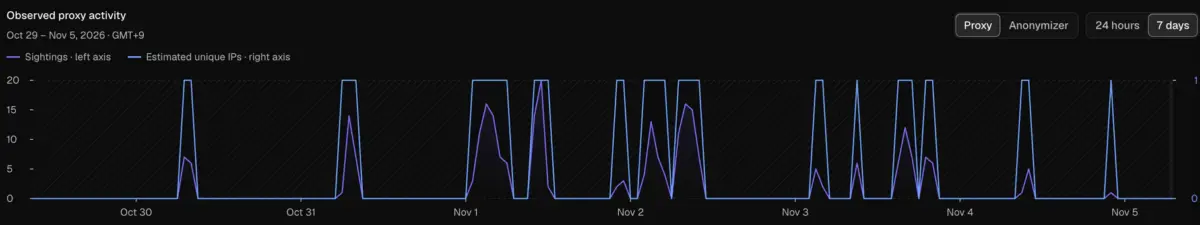
Security experts have issued a troubling warning after discovering that several staffers at the White House are actively utilizing computers or mobile devices equipped with residential proxy services. These background applications render their internet addresses available for external parties to rent, inadvertently opening a potential backdoor into some of the most sensitive and secure government networks in the world.
According to findings released by security firm Layer3 Intel, multiple residential proxy nodes were detected beaconing out from the dedicated internet address network reserved exclusively for the Executive Office of the President, designated as AS2650. The firm reported that the proxy activity was relatively persistent over a month-long monitoring window, occurring between October 5 and November 3. A comprehensive review of the proxies available from this specific Autonomous System Number showed that they successfully exited from the White House network 236 times during that designated period.
Adding a layer of geopolitical and historical concern to the discovery, proxy tracking company Synthient revealed on social media that the activity observed coming from AS2650 was directly related to multiple Windows 11 installations of a service known as Infatica. Infatica is a commercial proxy program frequently integrated into seemingly benign free mobile and desktop applications. The founder of Infatica is Vladimir Fomenko, a Russian national whose previous web hosting business, King Servers, served as the digital infrastructure ground zero for cyberattacks against state election systems in Arizona and Illinois back in 2016. At that time, King Servers housed six of the eight internet addresses utilized by Russian state security services to compromise sensitive databases belonging to those American election systems.
The existence of residential proxy services highlights a pervasive and often misunderstood corner of the modern internet. There are dozens of commercial residential proxy providers operating globally with varying degrees of legitimacy, a significant portion of which are based in countries like China and Russia. While these networks market themselves for legitimate data-gathering tasks, they all fundamentally function by making it remarkably simple for paying customers to rent someone else’s residential or corporate internet address.
This mechanism allows users to completely anonymize their web traffic or spoof their true geographic location. From the perspective of any website or online service, the traffic originating from a proxy network user appears to stem entirely from the rented IP address—such as one belonging to the White House—rather than from the actual individual operating the proxy service.
Layer3 Intel’s telemetry revealed that the proxy exit nodes operating out of the White House originated from six distinct internet addresses, appearing on 26 out of the 30 days monitored by the firm. Furthermore, the analysis showed that the majority of this unauthorized proxy activity took place during evening hours, specifically between 5 p.m. and midnight, a timeframe when typical government operational tempo might shift or when personal device usage patterns change.
Perhaps most alarming to cybersecurity professionals is that Infatica was not the only service capable of channeling traffic through the heart of the American executive branch. Layer3 Intel reported an even broader exposure, stating that it found 28 separate residential proxy services were able to successfully route and exit traffic through this dedicated government network.
Describing the ease with which outside entities could leverage these connections, the Layer3 Intel research team emphasized the public and unprotected nature of the flaw in a published analysis. They noted that anyone can obtain access simply by signing up for a public residential proxy service, paying a few dollars, and sending routing requests through it. The researchers clarified that they did not selectively target this specific network or attempt to force their probes to exit from it, noting instead that they caught the exposure entirely by chance simply by requesting global rotating access through these commercial services.
The White House did not immediately respond to requests for comment regarding the security findings.
The presence of residential proxy traffic on corporate and government networks is not merely an administrative oversight; it represents a major source of unwanted and frequently malicious cyber activity. Over the past year, security researchers have repeatedly documented how these networks are leveraged for account takeovers, cybercrime operations, large-scale advertising fraud, and aggressive mass content scraping to fuel artificial intelligence training projects.
Beyond data harvesting, these applications introduce severe security vulnerabilities into any environment where they are installed. In late 2025, security analysts discovered that cybercriminals were aggressively exploiting a widespread structural flaw inherent in many residential proxy services. This vulnerability allowed bad actors to systematically probe each proxy endpoint’s local network, searching for vulnerable systems and internal devices to infect with malware.
The danger was further underscored in January 2026, when dozens of residential proxy services were forced to scramble and patch their infrastructure after Synthient Founder Ben Brundage demonstrated how cybercriminals were actively abusing these vulnerabilities. Threat actors were using residential proxy routes to seize administrative control over devices residing deep inside the local networks of unsuspecting users, transforming residential setups into launchpads for broader network compromises.
Ben Brundage highlighted the low cost and minimal friction that make these ecosystems attractive to malicious actors, noting that some resellers sell bandwidth for as little as sixty cents a gigabyte. For less than a dollar, an individual can gain an operational foothold inside some of the most confidential and trusted networks in existence. According to Brundage, the broader reseller ecosystem exacerbates the issue by allowing cybercriminals to routinely bypass standard Know Your Customer, or KYC, verification processes.
In many cases, these dangerous proxy connections find their way onto protected corporate and government environments because employees inadvertently bring infected personal devices into the workplace, or install seemingly harmless consumer software on work-issued machines. Software developers frequently monetize their free applications by embedding software development kits provided by residential proxy networks, compensating the app creators with small financial kickbacks for every installation achieved.
Despite the obvious security implications, the infiltration of government and corporate networks by residential proxies is remarkably widespread. Data compiled by proxy tracking service Spur during a webinar in January 2026 revealed that residential proxies were detected residing inside nearly 300 government-owned and operated networks. The tracking data also identified active proxy nodes within 318 utility companies, 166 healthcare organizations and hospitals, and 141 institutions operating within the banking and finance sector. Similarly, a security advisory published earlier this year by Infoblox indicated that an astonishing 65 percent of its enterprise customer base had internal systems querying one or more residential proxy-related domains.