Authorities in the Netherlands have arrested a 24-year-old convicted cybercriminal on suspicion of aiding in sophisticated data thefts and widespread extortions orchestrated by the prolific and aggressive hacker group ShinyHunters. The high-profile arrest has sent immediate shockwaves through the cybercrime underworld, triggering a dramatic and brazen escalation in retaliatory attacks from the remaining members of the collective. In the days immediately following the suspect’s detention, the group launched high-profile campaigns, stealing highly sensitive personal and medical data from the Federal Bureau of Investigation (FBI) and turning their sights on extorting the notorious Russian ransomware syndicate known as Cl0p.
According to three sources familiar with the matter, the Dutch man taken into custody by law enforcement this month is Pepijn van der Stap, a convicted cybercriminal from Almere and Lelystad in the Netherlands. Van der Stap previously stood trial and was convicted in 2023 for his involvement in a sweeping string of international data thefts and corporate extortions. Dutch prosecutors estimated at the time that those illicit activities generated between €1.5 million and €2.7 million in criminal proceeds.
During his late 2023 trial, van der Stap admitted to living a complex, double life reminiscent of Dr. Jekyll and Mr. Hyde. He confessed to secretly utilizing the hacker handle “Umbreon” to extort victims and publish stolen corporate and personal databases on prominent English-language hacking forums, including the now-defunct RaidForums and Breached. By day, however, van der Stap maintained a completely respectable professional facade, working as a software engineer at Hadrian, an Amsterdam-based cybersecurity startup, while simultaneously volunteering his technical expertise at the Dutch Institute for Vulnerability Disclosure (DIVD), a well-known nonprofit security research organization.
Van der Stap fully confessed to his extensive data theft and extortion operations during court proceedings and was sentenced to four years in prison, with one year suspended. In a somewhat unusual twist during his trial, van der Stap opted to remain in custody temporarily rather than return home, explaining to the court that he felt he could not find adequate treatment on the outside for his ongoing psychological struggles. He maintained that these issues stemmed from severe post-traumatic stress disorder related to childhood trauma. He was ultimately released from prison in December 2025.
In an interview with KrebsOnSecurity on September 9, 2026, van der Stap actively cast himself as a thoroughly reformed individual striving to turn his life around and make a positive, constructive contribution to society. At the time of the interview, van der Stap was employed as an offensive security lead at Neo Security, a Dutch cybersecurity firm that ultimately did not respond to multiple requests for comment from journalists.

During that same conversation, van der Stap noted that he was still navigating complex civil lawsuits and restitution demands stemming from his past cybercrime activities, emphasizing that he was doing his absolute best to make amends to those affected. However, shortly after that interview concluded, the Dutch hacker abruptly stopped replying to messages. Efforts by close acquaintances and colleagues to reach him repeatedly failed over the subsequent two weeks.
According to two sources with direct knowledge of the ongoing investigation, van der Stap was arrested by Dutch law enforcement on or around September 16 and has remained in custody for intensive questioning ever since. One source reported that a colleague personally witnessed Dutch authorities removing boxes and equipment from van der Stap’s residence during the operation.
Law enforcement agencies across the Netherlands have spent months pursuing leads related to the ShinyHunters network. Earlier in September, Dutch police publicly appealed for help from the citizens to identify a native Dutch-speaking voice recorded in a phone call from February 2026. During that call, a ShinyHunters operative successfully used social engineering techniques to compromise Odido, the nation’s largest mobile telecommunications provider. The intruder tricked an Odido employee into authenticating their credentials on a spoofed website, leveraging that unauthorized access to steal personal data belonging to more than 6.2 million Dutch citizens.
Responding directly to local news media reports, ShinyHunters confirmed that the individual heard in the released audio clip is indeed an active member of their decentralized collective. In a public statement shared with the NL Times, the group vowed unwavering solidarity with their detained associate. "Our team member has our full support — emotionally, mentally, and financially," the hackers declared, adding that everything from legal representation to daily needs had been arranged. The group also directed harsh, derisive language toward Dutch law enforcement, predicting that investigators would struggle to prevent further large-scale operations within the country.
FBI AND CL0P HACKS
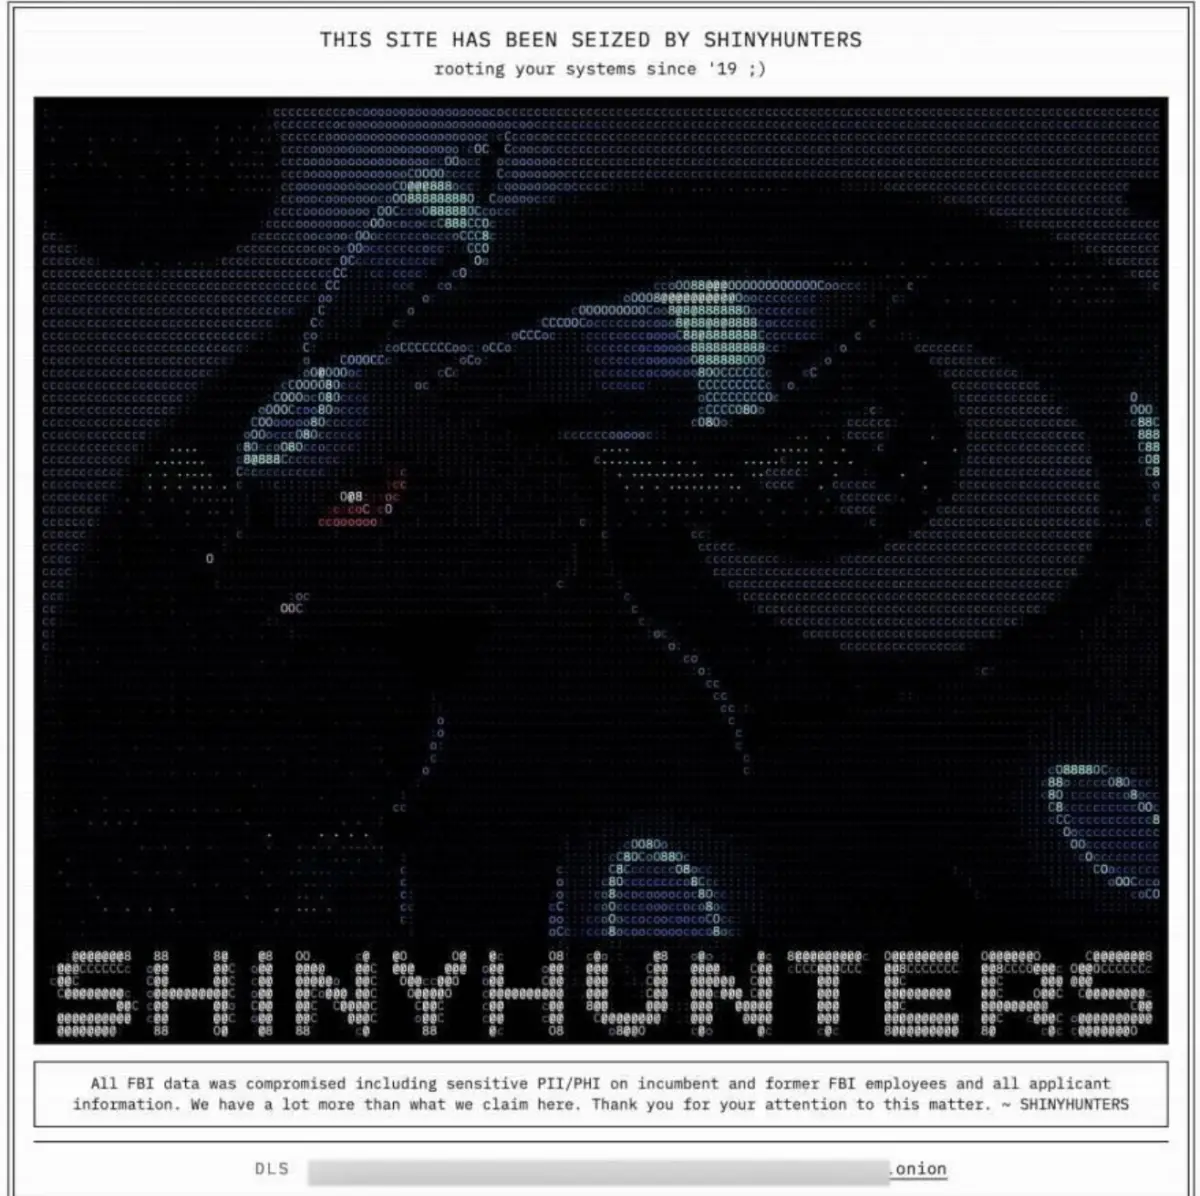
The situation escalated sharply just days after sources indicated van der Stap was detained. ShinyHunters publicly claimed credit for an extraordinarily brazen breach targeting the FBI’s official job application portal, apply.fbijobs.gov. Reporting from outlets including 404 Media and Reuters revealed that the stolen data included Social Security numbers and deeply sensitive personal information concerning more than 5,000 current officials and job applicants.
The compromised records detailed specific job titles and sensitive assignments within the bureau, including special agents, threat intake examiners, members of major cybercrimes units, and personnel dedicated to investigating foreign state-backed cyber threats. Furthermore, Reuters examined documents shared by the group which revealed that the cache included confidential psychiatric and medical files belonging to FBI employees. The bureau subsequently issued a brief statement confirming the unauthorized compromise of the portal.

According to ShinyHunters, access to the FBI portal and other victim networks was achieved by exploiting a recently patched vulnerability—cataloged as CVE-2026-35273—affecting PeopleSoft, a widely used enterprise software-as-a-service platform owned by software giant Oracle. Organizations heavily rely on PeopleSoft for human resources, hiring, payroll, and benefits management. Oracle moved quickly to issue a software fix after discovering that ShinyHunters had been actively exploiting the vulnerability as a zero-day since June. Concurrently, Mandiant released web application firewall rules designed to assist organizations that could not immediately apply the security patches.
Security reports published later in September by Mandiant and the Google Threat Intelligence Group revealed that ShinyHunters bypassed mitigation rules by employing a clever URL-encoding trick. This mass-exploitation campaign affected dozens of systems across diverse sectors globally, including higher education, technology, healthcare, agriculture, transportation, and government agencies.
Intriguingly, van der Stap’s former hacker moniker, "Umbreon," appeared prominently in the imagery left behind by ShinyHunters following the FBI portal breach. The defacement message posted on the seized FBI jobs site featured an ASCII art rendering of the Pokémon character Umbreon alongside a taunting banner declaring the site seized. Security analysts noted that the visual aesthetic was virtually identical to defacements the group used during past attacks, establishing a thematic thread tying the collective’s history directly to the unfolding drama.
Multiple sources close to the investigation suggested that these high-risk attacks against both the FBI and Cl0p—one of Russia’s most prominent ransomware syndicates—represented a sharp departure from the group’s previous operational style. Analysts attributed this sudden strategic pivot to a leadership shift within ShinyHunters, following a takeover by a teenage cybercriminal from Amman, Jordan. Known by the alias "Rey," this individual operates as a key figure within ScatteredLapsussHunters (SLSH), a hybrid cybercrime amalgamation uniting elements of Scattered Spider, LAPSUS$, and ShinyHunters.
Sources familiar with underground dynamics indicated that Rey harbored a lingering feud with the Dutch hacker regarding control over the ShinyHunters brand and amassed data assets. Consequently, analysts believe the inclusion of the oversized Umbreon imagery in the FBI site defacement was a deliberate attempt by Rey to cast suspicion and pin the blame squarely on the imprisoned Dutchman.
Rey was first publicly unmasked by cybersecurity firm KELA in March 2025. Subsequent investigative outreach to Rey’s family members revealed a complex underworld involvement, with the teenager admitting to participating in various ransomware operations while simultaneously attempting to distance himself from the broader SLSH collective. Following intense media scrutiny and further inquiries from researchers regarding his rising prominence within ShinyHunters, Rey abruptly deleted his primary social media accounts.

The underlying friction between SLSH and ShinyHunters stems from a short-lived operational partnership formed earlier in the year. According to reporting by Wired, the groups briefly collaborated to better monetize stolen credentials gathered by TeamPCP, an upstart supply-chain hacking collective. Although TeamPCP successfully compromised global code supply chains, they struggled to generate substantial financial returns before two of their alleged leaders were arrested in Australia.
Investigations revealed that Mandiant had secretly infiltrated TeamPCP’s infrastructure, continuously feeding compromised credentials to major cloud providers like Amazon and Microsoft so that stolen keys could be rapidly invalidated. As the operational profits dried up, the allied hacker factions began pointing fingers and blaming one another for burning the stolen access. Reports indicated that ShinyHunters eventually went rogue, utilizing the shared credentials to execute independent extortions without cutting in their partners.
Despite the internal strife, security researchers estimate that ShinyHunters has maintained a lucrative extortion spree throughout the year, remaining on track to pull in nearly $100 million in illicit payments. Van der Stap, by contrast, consistently maintained that his own historical hacking activities were never primarily driven by financial enrichment. In previous interviews, he described his motivation as an obsessive compulsion to acquire, organize, and archive the world’s most comprehensive collection of stolen databases.
Meanwhile, the Dutch Institute for Vulnerability Disclosure (DIVD) reported an internal cybersecurity incident involving the potential malicious use of artificial intelligence. However, a spokesperson for the nonprofit clarified that the event bore no relation to ShinyHunters and showed no ties to any former volunteers.
Dutch police formally confirmed the arrest of the 24-year-old suspect in connection with the ongoing ShinyHunters investigation, announcing that he would appear before the Rotterdam District Court. Concurrently, investigative reports emerged in local media suggesting that Dutch authorities are reviewing whether the suspect attempted to orchestrate murders abroad.
As the international investigation deepens, FBI leadership has expressed gratitude to Dutch law enforcement for their decisive partnership. Brett Leatherman, assistant director of the FBI’s cyber division, issued a direct warning to the remaining members of the ShinyHunters collective, emphasizing that ongoing arrests and disrupted infrastructure continue to narrow the net around cybercriminals operating globally.