Google announced today that it has successfully worked alongside a coalition of industry partners to dismantle a sprawling botnet consisting of more than 1.3 million Android TV set-top boxes. These devices were shipped directly to consumers pre-installed with malicious software designed to covertly monetize the hardware. The malware secretly rented out unsuspecting users’ internet connections to external strangers while simultaneously orchestrating widespread advertising fraud. Experts closely involved in the coordinated takedown warn that this decisive action is likely to severe the botnet’s harmful access to more than 10 million additional compromised systems globally. These supplementary systems include a wide variety of Internet of Things (IoT) products, ranging from Android-based healthcare and telehealth devices to commercial karaoke machines and digital signage setups.
A comprehensive report published by the Google Threat Intelligence Group (GTIG) revealed that Google has officially severed all ties with Videostrong Technology Co., a prominent TV box manufacturer based in China. According to conclusions reached by GTIG and other independent cybersecurity experts, Videostrong was directly responsible for embedding the malicious code that enrolled more than 1.3 million set-top boxes into a sophisticated botnet dubbed "XCPE," a designation derived from one of the malware’s core underlying code components.
The GTIG report detailed how the XCPE botnet operated by loading infected user devices with specialized background software. This software dynamically exposed the user’s home internet protocol address, making it available for resale by multiple commercial "residential proxy" services. These proxy services allow paying customers to rent residential IP addresses as a method to anonymize web traffic, scrape digital content, or spoof their true geographic location. As highlighted in numerous security investigations over the past several years, residential proxy networks have emerged as a primary vector for unwanted and illicit traffic, fueling malicious activities such as account takeover attacks, digital advertising fraud, and aggressive mass data scraping operations executed for artificial intelligence development projects.
According to the GTIG public advisory, Videostrong actively monetized the built-in system backdoor by selling illicit access to various criminal affiliates, subsequently loading those third-party affiliates’ malicious modules straight onto the vulnerable devices. To neutralize the threat, Google undertook decisive legal action to seize and disable the specific domains and command-and-control servers that Videostrong relied upon to operate the botnet and push secondary malware payloads. GTIG emphasized in its report that a hardware manufacturer intentionally embedding malware into consumer devices represents an egregious and unacceptable breach of trust, posing severe operational and privacy risks to everyday users. Without the explicit knowledge or consent of the owners, these compromised devices were effectively transformed into an automated distribution network for a diverse array of malicious actors.

While standard TV streaming boxes accounted for the vast majority of the infections, the GTIG investigation uncovered the exact same XCPE malware variant embedded within a variety of other Android-based IoT products. These included specialized telehealth hardware, automated karaoke systems, and commercial digital signage platforms deployed in public venues. Google mandates that all Android device manufacturers must successfully pass rigorous compatibility and security evaluations to ensure their hardware does not introduce risks to consumers. However, investigators found that Videostrong managed to circumvent these safeguards by engineering its malicious software to execute immediately following the initial boot sequence when a user powers on the device for the very first time. Google confirmed that it has since implemented measures to address and close this specific structural weakness.
The GTIG report also explicitly called out several residential proxy providers whose software development kits were routinely downloaded and utilized by devices ensnared in the XCPE botnet. Among those named is AppSalt, also widely known as Honeygain, which is owned by Oxylabs, a company headquartered in Vilnius, Lithuania. Oxylabs was recently relaunched under a new corporate brand called Source following a substantial $130 million funding injection from private equity firm Warburg Pincus, a transaction that reportedly valued the enterprise at approximately $3.6 billion. Oxylabs did not respond to requests for comment regarding its inclusion in the security reports.
Another prominent proxy provider linked directly to the botnet infrastructure was NetNut, a sprawling residential proxy enterprise formerly operated by Alarum Technologies, a publicly traded company based in Israel. The disruption follows previous enforcement actions in July, when the Federal Bureau of Investigation collaborated with industry partners to seize hundreds of domains associated with NetNut. At the time, federal authorities stated that the company was responsible for operating a completely separate botnet named Popa, which similarly enslaved standard TV set-top boxes to function as residential proxies. Additional proxy services explicitly named in the GTIG report include EarnFM, Traffmonetizer, Jaguar, LINKFOG, BMW/IPWeb, and GaGaNode.
Google’s formal announcement credited a broad coalition of industry collaborators, including Synthient, a specialized security startup that continuously tracks residential proxy providers. In January, Synthient published influential research detailing the rapid, aggressive spread of the Kimwolf botnet. At the time, Kimwolf was actively inundating global networks with record-breaking distributed denial-of-service attacks. Synthient’s documentation illustrated how Kimwolf managed to infect millions of Android set-top boxes virtually overnight by exploiting widespread vulnerabilities inherent in these residential proxy services, subsequently compromising other connected Android devices residing within the local home networks of unsuspecting consumers.
The publication of Synthient’s research prompted dozens of residential proxy providers to patch critical vulnerabilities in their respective networks. This remediation effort fragmented the Kimwolf botnet into much smaller, isolated segments, rendering its continuous and disruptive DDoS attacks significantly easier for network operators to mitigate and manage. The situation also captured the attention of the Motion Picture Association, a prominent trade organization representing major Hollywood film studios. The MPA partnered directly with Synthient to purchase, reverse-engineer, and dismantle a variety of popular Android TV set-top boxes that had been compromised by Kimwolf and other competing IoT botnets.

In a comprehensive report published alongside Google’s announcement, Synthient examined a popular, pre-infected streaming device marketed under the brand MECOOL by Skyworth Technology, a publicly traded corporation based in China. Synthient concluded that MECOOL boxes similarly bundled malware originating from Videostrong Technology Co. and actively installed AppSalt, Honeygain, and other related proxy components without user awareness. Synthient founder Ben Brundage revealed in interviews that Videostrong’s malicious distribution network also pushed software associated with the Grass proxy service. Previous industry investigations into popular streaming hardware like Superbox similarly identified embedded residential proxy software linked to Grass, though representatives for Grass have consistently denied any formal corporate affiliation with the hardware manufacturers.
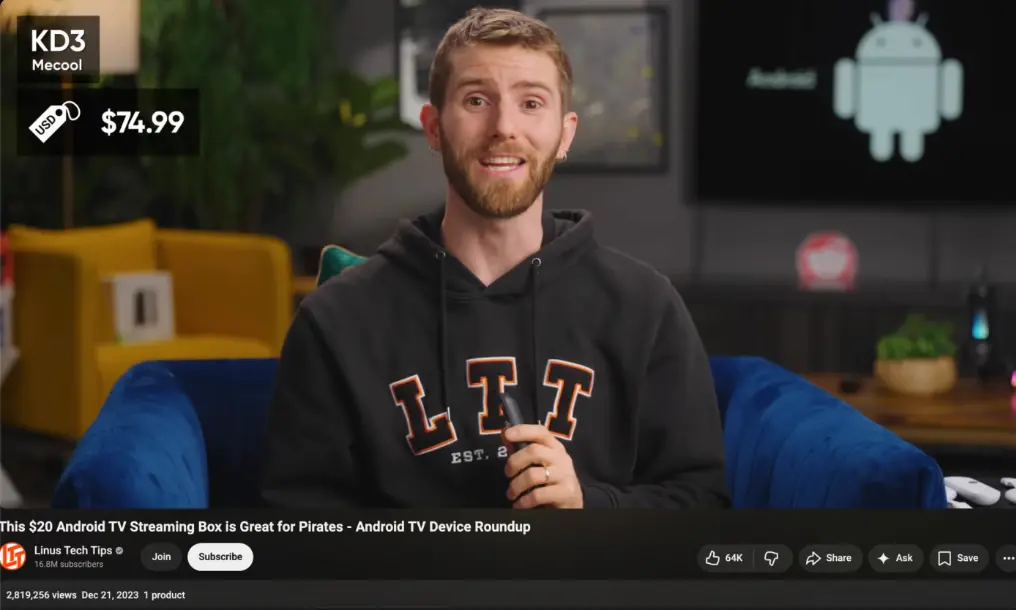
Investigations into how these pre-infected devices achieve widespread market adoption point heavily to modern digital marketing channels. Superbox and comparable Android TV set-top boxes have historically acquired new customers by engaging online influencers across platforms like TikTok and YouTube. These creators frequently endorse the hardware by highlighting its ability to provide access to hundreds of unauthorized, pirated pay-per-view and cable television streaming channels for a single, low, up-front fee. Similarly, Synthient’s research noted that MECOOL set-top boxes experienced an explosive surge in market popularity after the hardware was featured in a 2023 video by the prominent YouTube channel Linus Tech Tips, which boasts an audience of nearly 17 million subscribers. Representatives for Linus Tech Tips shared a statement indicating that the channel has since updated the archived video to explicitly frame the product as a consumer scam and has removed all associated monetization and affiliate links.
The latest estimates from the GTIG report suggest that the complete takedown of the XCPE botnet will successfully sever access to at least 10 million additional compromised systems. Analysts noted that the diverse network of proxy and ad-fraud affiliates tied to Videostrong maintained independent distribution channels for their respective software modules that extended far beyond the core XCPE framework. Synthient founder Ben Brundage reinforced this perspective, characterizing the baseline figure of 1.3 million infected devices as highly conservative. The actual scale of affected consumer hardware is likely substantially higher, making this intervention one of the largest coordinated operations targeting backdoored streaming and TV set-top boxes to date.