The international hacking collective known as ShinyHunters has claimed responsibility for dozens of massive data breaches dating back to 2019. Originally operated primarily by cybercriminals based in France, control over the brand shifted over time as law enforcement dismantled the group’s early core membership. Leadership eventually fell to "Rey," whom authorities identified last year as a teenage hacker residing in Amman, Jordan. According to estimates from the FBI, ShinyHunters has successfully extorted more than $70 million from corporate and governmental victims so far this year alone.
The group’s brazen activities drew unprecedented scrutiny in late September, when ShinyHunters compromised the FBI’s recruitment portal, fbijobs.gov. The hackers openly taunted federal authorities by threatening to publish a cache of stolen internal files. Reports indicate the compromised data included deeply personal records—such as home addresses, Social Security numbers, medical and psychological documentation, and specific details regarding employee units and specializations.
The breach of the FBI jobs portal prompted an immediate and aggressive response from federal law enforcement, leading to the rapid detention and questioning of individuals suspected of maintaining communications with Rey and other key suspects. On October 3, Reuters reported that Rey had been detained by authorities in Jordan and was actively cooperating with the FBI.
Rey’s ascent to leadership within ShinyHunters followed the sudden incapacitation of a senior member. On the evening of September 15, law enforcement officers in the Netherlands executed a high-stakes raid, arresting convicted hacker and ShinyHunters suspect Pepijn van der Stap. Dutch police reportedly deployed flash-bang grenades to stun Van der Stap and secure him before he could wipe his active online sessions.

According to a source close to the investigation, authorities apprehended Van der Stap while he remained logged into his Signal instant messaging account. This tactical advantage allowed investigators to immediately review recent communications with frequent contacts, including ransomware negotiators operating out of Canada and the United States.
Multiple sources with direct knowledge of the investigation revealed that Van der Stap’s decrypted Signal messages became the critical breakthrough in unraveling a separate murder-for-hire plot that surfaced in the wake of his arrest. Dutch news outlet RTL reported last month that the planned attacks were intended to be carried out abroad, with investigative indications pointing to Van der Stap as the individual who issued the orders, though authorities emphasize there is no evidence the plot was ever executed.
The fallout from Van der Stap’s arrest widened significantly on October 9, when the FBI arrested Edward Dubrovsky, a 54-year-old Canadian cybersecurity executive, in connection with the sprawling ShinyHunters probe. Dubrovsky, who recently authored a book on cyber extortion management that advocated for maintaining open communication with hackers, faces federal charges including threatening to disclose compromised data and interfering with interstate commerce through extortion, according to court documents. Politico reported that federal prosecutors requested Dubrovsky remain in custody pending trial, and case records have been placed under seal.
Investigators analyzing Van der Stap’s Signal chats discovered that the Dutch suspect maintained frequent communications with Dubrovsky and at least one executive at a major U.S.-based consulting firm. According to a source close to the probe, these executives frequently possessed intimate knowledge of fresh ShinyHunters cyberattacks even before the victim organizations themselves realized they had been breached.
Perhaps most explosively, investigators found that Dubrovsky was fully aware that ShinyHunters had successfully plundered sensitive data from FBI servers. Despite this knowledge, federal records indicate Dubrovsky never alerted the bureau to the security failure prior to the extortion group’s public threats on social media to publish the agency’s classified personnel files.

SHINYWIRE
As the probe deepened, sources close to the investigation told investigators that at least one executive at a prominent U.S. consulting firm played an active administrative role in operating "shinywire[.]com," a now-defunct extortion portal utilized by ShinyHunters. While the firm—which boasts more than 1,000 associates—and the specific executive have not yet been formally charged, their identities are a focal point of the ongoing federal inquiry.
The Shinywire platform operated from approximately May 3 until October 16, listing nearly 100 corporate and institutional victims targeted by the cybercrime syndicate. Each profile on the site served as a pressure point, urging victim entities to open negotiations, displaying samples of stolen documentation, and threatening total public exposure of proprietary records if demands were ignored.
Cached internet records highlight the platform’s tactics, including an extortion listing targeting Intuitive Surgical, a prominent American medical technology corporation. Intuitive Surgical suffered a network breach in March after an employee fell victim to a targeted phishing campaign that compromised corporate credentials.
Victims who refused to engage or negotiate within a strict seven-day window found their stolen archives dumped onto the primary ShinyHunters shaming blog, a dark web site accessible exclusively via the Tor anonymity network.
The legal and professional fallout has begun to fracture the corporate cybersecurity landscape. In mid-October, The Globe and Mail reported that months prior to his federal arrest, Dubrovsky had filed a civil lawsuit in Ontario against Daniel Tobok, the former chief executive of Cypfer, a Toronto-founded cybersecurity firm with international operations. The two men had partnered in 2017 to build Cypfer, where Dubrovsky served as managing partner and chief operating officer before a bitter falling-out in 2024. Dubrovsky alleged in court filings that Tobok gradually pushed him out of business decisions and launched a campaign to destroy his professional reputation, while Tobok filed a counterclaim accusing Dubrovsky of competing unfairly and misrepresenting his ownership stake.

GHOSTBYTE
Interviews with former colleagues of Daniel Tobok reveal that years prior to the current controversies, he was known within cybercrime circles by a specific moniker: Ghostbyte. In 2018, a Canadian enterprise was compromised by Dharma, a prolific Russian-language ransomware affiliate program. Facing the permanent loss of unrecoverable encrypted files, the victim company sought assurances from the extortionists that their data would indeed be restored and kept confidential upon payment.
In a redacted email response recovered from the incident, the Dharma representative directed the victim to seek guarantees through a third-party IT specialist in Canada, explicitly recommending they reach out to the email address "[email protected]."
"If you want guarantees, you can write to the IT company," the Dharma operative advised. "Take the phone and negotiate with them. This IT company often solves such problems in Canada. You can contact them and sign a contract for services."
While it remains unproven whether Tobok actively utilized the Ghostbyte alias during those negotiations, threat intelligence firm Constella Intelligence identified that an email address frequently used by Tobok—"[email protected]"—was tied to online accounts operating under the username "ghostbyte," including a Snapchat profile. Constella’s tracking also linked the Dharma representative’s wallet address to substantial cryptocurrency transactions totaling dozens of bitcoin.
Cypfer issued a formal statement distancing the company from the ongoing criminal proceedings, asserting that its business model does not involve facilitating ransom payments. The firm maintained that it learned of Dubrovsky’s arrest through media reports and had received no outreach from law enforcement regarding an investigation into the company itself. Cypfer noted that it operates entirely independently of CyberSteward—another firm tied to the principals—and pointed to its recent acquisition by the Apros Group, a holding company led by former FBI special agent Jason Hogg.

CONFLICTING INTERESTS
Under U.S. law, paying a ransom to recover encrypted files or secure promises of data deletion is not inherently illegal, provided the extortion group is not formally sanctioned by the U.S. Treasury Department. ShinyHunters currently lacks formal designation on government sanctions lists. Nonetheless, corporate victims frequently find themselves caught in a web of conflicting guidance from cyber insurance providers, incident response firms, and federal law enforcement.
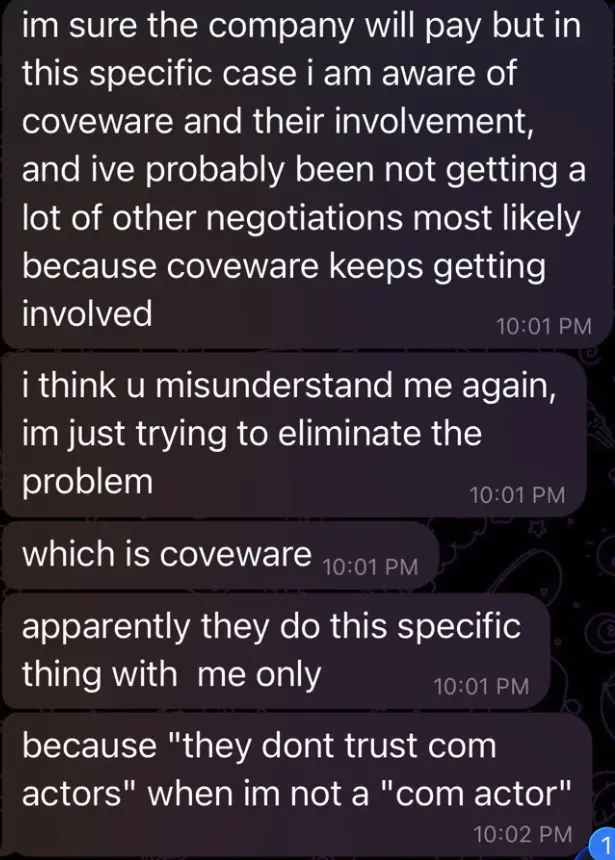
While reputable incident response organizations—such as Coveware and Unit 221B—consistently advise corporate victims against paying ShinyHunters, pointing out that extortionists routinely resell or re-extort stolen data regardless of payouts, other firms readily step in to facilitate transactions. The FBI issued a formal public service announcement advising against paying the syndicate, a stance that drew the ire of ShinyHunters leadership. Internal chat logs reviewed by investigators revealed group administrators expressing deep frustration over Coveware’s public warnings, complaining that the firm’s anti-payment advocacy severely hampered their incoming revenue streams.
Industry veterans point out an inherent structural conflict within the cybersecurity remediation market. Mark Camillo, chief executive of the cyber insurance industry group CyberAcuView, noted that negotiation firms charging a percentage of the final ransom payout maintain a financial incentive to keep ransom figures high rather than aggressively driving down costs.
"It has come to the industry’s attention that many of the ransomware payers charge a percentage of the final payment which may or may not be disclosed," Camillo observed. "This makes no sense if they are also the negotiator. There needs to be more transparency in the process as no one in the ecosystem should be profiting purely on the size of the ransomware transaction."
Federal prosecutors have increasingly targeted intermediaries who cross legal boundaries. In October, the Department of Justice charged MonsterCloud CEO Zohar Pinhasi with wire fraud and conspiracy for allegedly billing clients millions for remediation while secretly paying hackers behind the scenes. Similarly, in July, Florida-based ransomware negotiator Angelo Martino was sentenced to 70 months in prison after being convicted of conspiring with the Blackcat/ALPHV ransomware group to maximize victim payouts by leaking confidential negotiation strategies.