The GeoServer open-source project has released a comprehensive security recap detailing a turbulent summer of 2026. The period was marked by newly discovered Common Vulnerabilities and Exposures (CVEs), a high-profile zero-day exploit, a supply chain advisory, and a notable rise in AI-assisted vulnerability submissions. Project maintainers are urging all administrators and organizations relying on the widely used geospatial software to apply the latest security updates immediately to protect their systems.
For administrators responsible for managing GeoServer instances, the primary and most urgent takeaway is clear: systems must be updated without delay. The project team has rolled out targeted releases to address these vulnerabilities, specifically pointing users toward GeoServer 3.0.1, GeoServer 2.28.5, and GeoServer 2.27.6. These updates contain critical fixes intended to secure instances against active threats discovered over the preceding months.
The GeoServer project has long adhered to a strict coordinated vulnerability disclosure policy. Under this framework, security flaws are identified, privately evaluated, and fixed across both stable and maintenance release branches before any technical details or CVE identifiers are made public. The fundamental objective of this policy is to ensure that all users and organizations have a fair and adequate opportunity to patch their systems before malicious actors can weaponize the underlying vulnerabilities.
However, maintaining this security equilibrium proved challenging during the summer months due to unexpected external disclosures. In August, GeoServer found itself managing a critical zero-day vulnerability—an active exploit functioning in the wild without an immediate, publicly available native patch at the time of the leak. Prior to the public breach, the underlying problem had already been privately reported to the project by several independent security researchers, and a formal fix had been scheduled for inclusion in the upcoming GeoServer 3.0.1 release.
The zero-day crisis escalated rapidly when an unrelated third party, operating entirely independently of both the core development team and the initial reporting researchers, disclosed the vulnerability publicly on social media channels. The consequences were immediate and severe. Automated scans searching for vulnerable instances were detected across the internet within mere hours of the social media post going live.
The velocity of the subsequent threat activity prompted swift media attention and generated an urgent call to action disseminated through the official user forums managed by the Open Source Geospatial Foundation. Project leadership publicly expressed their gratitude to security researcher Ravie Lakshmanan for initially notifying them through the Open Source Geospatial Foundation. The swift deployment of GeoServer 3.0.1, alongside maintenance updates 2.28.5 and 2.27.6, helped mitigate the worst of the fallout. According to project representatives, this intense episode vividly reaffirmed the critical importance of adhering to coordinated vulnerability disclosure protocols and emphasized why users must apply updates the moment they become available.
This recent incident builds upon a series of security challenges managed earlier in the season. On June 11, 2026, alongside the major release of GeoServer 3.0.0, the project published several other CVEs affecting earlier versions, including updates for GeoServer 2.27.3, 2.26.4, and the 2.27.0 branch. These continuous release cycles highlight the ongoing effort required to maintain software integrity in complex enterprise environments.
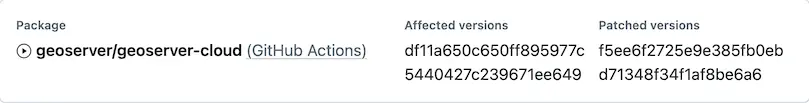
In addition to direct software vulnerabilities, the project encountered a different kind of security test over the summer via a supply chain advisory. Supply chain advisories carry the inherent potential to undermine the baseline trust and integrity of the software files downloaded by end users. This marked the first time the GeoServer project had to navigate an infrastructure-related advisory of this nature. Because the issue was tied to the GitHub Actions workflow for the geoserver/geoserver-cloud repository rather than an official core release of GeoServer itself, it did not qualify for a traditional CVE number.
Project leadership moved quickly to reassure the community that no official GeoServer releases were compromised or affected by the infrastructure incident. Standard GeoServer releases continue to be compiled securely using a dedicated Jenkins build server that publishes official artifacts simultaneously to SourceForge and the official OSGeo infrastructure, maintaining a strict firewall between development cloud pipelines and production distribution channels.
Beyond traditional bugs and supply chain checks, the GeoServer security team has faced an unprecedented surge in automated administrative burdens brought on by the technology industry’s broader shift toward generative artificial intelligence. Like many other prominent open-source software projects, GeoServer is experiencing a massive wave of vulnerability reports generated with AI assistance.
To manage this influx, the project has established a dedicated general AI policy and updated its core security policy on GitHub. These documents explicitly acknowledge the reality of AI-generated tooling and provide clear guidelines for individuals submitting reports. Maintainers note that AI-generated reports are frequently very verbose, making human participation and clarity immensely valuable during the review process.
Evaluating these automated submissions often requires significant time investment just to review the claims, determine if the reports are duplicate submissions, or verify whether a real underlying flaw exists. Project contributors emphasize that community members who can assist by testing, verifying, and helping validate proposed fixes provide invaluable relief to the overburdened geoserver-security team.
Sustaining the security and longevity of GeoServer requires an active partnership between the core maintainers and the broader user community. Organizations that depend on geospatial infrastructure for their daily operations are strongly encouraged to consider financial sponsorship through the official project channels or to allow their internal technical staff to participate directly in the geoserver-security work groups. Furthermore, the project is actively working to establish formal project membership structures for public institutions and government agencies that frequently face administrative or legal restrictions regarding corporate sponsorship and direct participation.
To stay ahead of potential security threats, the GeoServer project operates on a predictable, time-boxed release cycle that maintains both stable and maintenance lines throughout the course of each year. Security maintainers strongly advise all administrators to upgrade their deployments to a supported release at least once every twelve months to ensure continuous coverage and access to vital security patches. Detailed guidance on navigating these transitions can be found within the official user guide documentation under upgrading existing versions.
For developers and security researchers seeking to report new issues privately and securely, the project maintains a strict protocol utilizing GitHub security advisories, ensuring that disclosures follow proper channels before any public awareness campaigns or software patches are finalized.