As the open-source community reflects on the security landscape over the summer of 2026, the GeoServer project has issued a comprehensive review of recent vulnerability disclosures, a noteworthy supply chain advisory, and an update to its operational security policies. Most critically, the project is urging all administrators managing GeoServer instances to immediately apply recent patches following an aggressive zero-day exploit cycle that unfolded in August.
For organizations running the widely used open-source geospatial software, the immediate directive from the core development team is clear: administrators must update their systems to GeoServer version 3.0.1, version 2.28.5, or version 2.27.6 depending on their specific deployment branch. These releases contain crucial fixes designed to secure instances against active threats that materialized during the summer months.
The GeoServer project maintains a strict coordinated vulnerability disclosure policy. Under normal operating conditions, vulnerabilities are discovered, analyzed, and patched across both stable and maintenance release branches before any Common Vulnerabilities and Exposures (CVE) details are made publicly available. The foundational goal of this protocol is to ensure that every organization utilizing the software has a fair and adequate window of opportunity to apply security updates prior to malicious actors obtaining actionable exploit intelligence.
However, the summer of 2026 tested these mechanisms in unprecedented ways, most notably during an incident in August involving a zero-day vulnerability. Prior to public awareness, the underlying problem had already been identified privately by several independent security researchers who responsibly reported it to the project. A fix had been scheduled for inclusion in the forthcoming GeoServer 3.0.1 release.
The security equilibrium was disrupted, however, when an unconnected third party publicly disclosed the vulnerability on social media before the official patch could be widely deployed. The consequences were immediate and severe. Automated vulnerability scanners and malicious actors began actively probing for the flaw within hours of the public social media post.
The rapid escalation generated significant industry attention, including coverage by prominent cybersecurity news outlets and urgent warnings distributed across the official OSGeo user forums. Project leadership formally acknowledged the swift reporting efforts of security researcher Ravie Lakshmanan, who first notified project leadership via the Open Source Geospatial Foundation. This tense episode starkly reaffirmed the critical importance of adhering to coordinated vulnerability disclosure timelines and underscored why system administrators must prioritize applying new releases the moment they become available.
Beyond the August zero-day incident, the summer review also cataloged previously published CVEs that emerged earlier in the season. These included security advisories published on June 11, 2026, which coincided with the major release of GeoServer 3.0.0. Those updates addressed specific security boundaries across the 2.27 and 2.26 maintenance lines, ensuring that long-term deployments remained resilient against newly discovered attack vectors.
In addition to direct software vulnerabilities, the project encountered a different kind of security challenge over the summer months: a supply chain advisory. Supply chain advisories inherently carry the potential to undermine trust in the integrity of downloaded software packages, making them a sensitive topic for any open-source project.
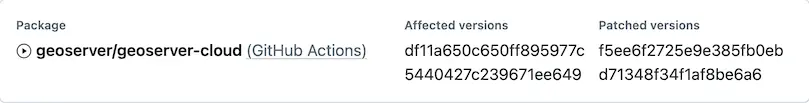
This particular event marked the first time the GeoServer project had to navigate an infrastructure-level advisory of this nature. Because the advisory did not correspond to an actual release of the core GeoServer software, it did not qualify for a traditional CVE number. Instead, the project categorized the advisory under the identifier for the GitHub Actions environment associated with the geoserver-cloud repository.
Crucially, project maintainers emphasized that no official GeoServer releases were compromised or affected by this infrastructure event. Standard GeoServer releases continue to be produced through a controlled Jenkins build server that securely publishes verified artifacts directly to SourceForge and official OSGeo infrastructure, maintaining a strict firewall between cloud automation environments and distribution channels.
Another prominent theme in the project’s summer review is the modern challenge of AI-assisted vulnerability reporting. Like many other prominent open-source software projects, the GeoServer maintainers have experienced a notable surge in security reports generated with the assistance of artificial intelligence tools.
To adapt to this shifting technological landscape, the project has established a dedicated general AI policy and formally updated its overarching security policy. These framework updates acknowledge the proliferation of AI-generated security content and provide clear guidance to researchers utilizing automated tools. While automated scanners and AI models can assist in finding potential code anomalies, they frequently produce reports that are exceptionally verbose, difficult to verify, and prone to generating high volumes of duplicate submissions.
The project notes that reviewing, parsing, and deduplicating AI-assisted reports requires a significant investment of time and human effort from core developers. Consequently, the security team has expressed deep appreciation for reporters who remain actively engaged to clarify complex findings, test proposed patches, and verify fixes as vulnerabilities are addressed. Collaborative community involvement directly lightens the operational burden on the dedicated geoserver-security team.
To sustain the security and health of the ecosystem, project leadership has outlined various ways for organizations and individuals to contribute. Enterprises and institutions that depend heavily on GeoServer for critical geospatial infrastructure are encouraged to financially sponsor the project or enable their technical staff to participate directly in geoserver-security operations and mailing lists. Furthermore, the project is actively working to establish formal project membership pathways for public sector institutions that may face legal or bureaucratic restrictions regarding corporate sponsorship and direct financial contributions.
Addressing questions regarding upgrade cadence, the project reiterated that GeoServer operates on a structured, time-boxed release cycle. Throughout the course of any given year, the project maintains parallel stable and maintenance release branches to ensure ongoing support. Administrators are strongly advised to upgrade their GeoServer installations to a supported release at least once a year to guarantee continuous receipt of essential security patches and bug fixes, with comprehensive upgrade instructions available through the official user guide documentation.
Organizations or independent researchers who discover potential security flaws in the future are instructed to follow the project’s established security policy, which mandates reporting vulnerabilities privately through GitHub security advisories rather than disclosing them prematurely through public channels. By maintaining disciplined reporting habits, respecting coordinated disclosure timelines, and keeping instances up to date, the GeoServer community aims to maintain the security and integrity of geospatial data infrastructure worldwide.