The GeoServer project has released a comprehensive security recap detailing a turbulent summer of 2026, which featured a high-pressure zero-day exploit, a supply chain advisory, and a notable surge in automated vulnerability submissions. Project maintainers are urging all administrators and organizations relying on the widely used open-source geospatial software to update their installations immediately to mitigate ongoing risks.
According to the project’s security advisory, users must upgrade their systems without delay to newly released versions. For those managing active deployments, the immediate directive is to apply patches by updating to GeoServer version 3.0.1, version 2.28.5, or version 2.27.6 depending on their specific branch. These releases contain crucial fixes designed to close critical security gaps that have emerged over recent months.
The GeoServer development team operates under a strict coordinated vulnerability disclosure policy. Under this framework, vulnerabilities are systematically addressed and patched across both stable and maintenance releases before any Common Vulnerabilities and Exposures (CVE) details are made public. The core objective of this policy is to provide the global user community with an adequate window of opportunity to apply necessary updates before malicious actors can weaponize the underlying flaws.
The August Zero-Day Incident
That coordinated approach faced a severe test in August, when GeoServer was hit with a zero-day vulnerability—an active exploit in the wild with no pre-existing official patch at the time of its wider exposure. Prior to the public leak, the underlying problem had already been handled responsibly through private disclosures by several independent researchers, with a formal fix already scheduled to roll out as part of the normal GeoServer 3.0.1 release cycle.
However, the situation escalated rapidly when an unconnected third party, entirely distinct from the project maintainers and the original reporting researchers, publicly disclosed the vulnerability on social media. The consequences were immediate and aggressive. Within hours of the social media post, automated security scans and malicious probes targeting this specific vulnerability were detected across the internet.
The velocity of the response from both the threat landscape and the project team was remarkable. The incident quickly drew external media coverage and prompted an urgent advisory across the official user forum. Project leadership formally extended their gratitude to reporter Ravie Lakshmanan, who first notified project leadership through the Open Source Geospatial Foundation, helping trigger the emergency response.
Maintainers noted that this intense experience powerfully reaffirms the critical importance of adhering strictly to coordinated vulnerability disclosure protocols and emphasizing the necessity for users to apply patches the moment new releases become available.
Review of Previously Published CVEs
The summer security recap also covers vulnerabilities addressed earlier in the season. On June 11, 2026, a series of CVEs were published concurrently with the major milestone release of GeoServer 3.0.0. These earlier disclosures prompted concurrent maintenance updates for branches such as GeoServer 2.27.3, 2.26.4, and foundational updates for the 2.27.0 release train. The project routinely backports security fixes into active maintenance streams to protect organizations that cannot immediately migrate to a major new software version.
Supply Chain Advisory and Infrastructure Security
In addition to direct software vulnerabilities, the project addressed a notable supply chain advisory encountered over the summer months. Supply chain advisories carry the inherent potential to compromise the integrity of software downloads and build environments.
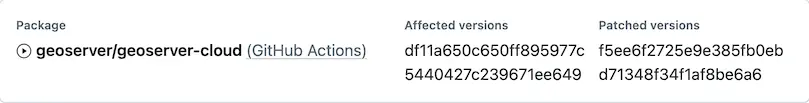
Significantly, this marked the first time the GeoServer project had to navigate an infrastructure-level advisory of this nature. Because the issue did not map directly to a traditional software release of GeoServer itself, it was formally designated as a "geoserver/geoserver-cloud (GitHub Actions)" advisory and did not qualify for a standard CVE identifier.
Project maintainers emphasized that no official GeoServer releases were compromised or affected by this supply chain concern. Standard GeoServer production releases are compiled and distributed using a dedicated Jenkins build server that publishes verified artifacts securely to both SourceForge and official Open Source Geospatial Foundation infrastructure.
Managing the Wave of AI-Assisted Vulnerability Reports
Reflecting a broader industry-wide trend affecting numerous open-source software projects, the GeoServer team reported a significant wave of vulnerability reports generated with the assistance of artificial intelligence tools. While AI tools can assist researchers in analyzing code, the sheer volume of verbose, automated, and frequently duplicative submissions has placed a heavy burden on the core security team.
To address this shift, the project has established a dedicated general AI policy and updated its official security policy. These framework updates acknowledge the reality of automated tool usage and provide clear, structured guidance for individuals submitting findings. Maintainers noted that when dealing with verbose AI-generated reports, having reporters on hand to clarify technical details, assist in reviewing duplicates, and verify whether a reported issue is genuine is deeply appreciated.
The security team noted that reviewing, validating, and testing fixes for these automated reports consumes substantial time. Community members who can actively test and verify patches as they are developed provide invaluable assistance in keeping the project secure and sustainable.
Community Support and Upgrade Cadence
As the project navigates an increasingly complex threat landscape, maintainers have appealed directly to the organizations and commercial entities that rely heavily on GeoServer infrastructure. Businesses and institutions are encouraged to financially sponsor the project or allow internal staff to directly participate in the geoserver-security working groups. Furthermore, the project is actively working to establish formal project membership pathways for public institutions and governmental agencies that often face rigid institutional restrictions regarding direct financial sponsorship and open-source participation.
Addressing questions regarding system maintenance, project leads stressed that GeoServer adheres to a predictable time-boxed release cycle. This model maintains active stable and maintenance releases across a rolling annual schedule. Administrators are strongly advised to upgrade their deployments to a supported release at least once every year to ensure continuous receipt of vital security patches and bug fixes. Comprehensive instructions for transitioning between versions are maintained within the official user guide to assist system administrators with migration planning.
Organizations seeking to report new security issues privately are directed to consult the project’s official security policy on GitHub, which outlines the secure channels required for responsible disclosure before any public advisories are issued.