The GeoServer project has issued a comprehensive security review and recap of advisories published over the summer of 2026. The period was marked by significant developments, including the handling of a high-profile zero-day vulnerability, a series of Common Vulnerabilities and Exposures (CVEs), a supply chain advisory impacting GitHub Actions, and the growing prevalence of automated, AI-assisted security submissions. For administrators and organizations managing geospatial data infrastructure, the immediate takeaway remains urgent: operators must update their deployments to the latest patched versions—specifically GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6—to ensure system integrity.
Throughout its operational history, the GeoServer project has maintained a strict adherence to coordinated vulnerability disclosure policies. Under this framework, security flaws are identified, analyzed, and remediated across both stable and maintenance branches before any detailed CVE information is made public. This strategic delay is deliberately designed to grant administrators a vital window of opportunity to apply necessary updates, thereby mitigating the risk of widespread exploitation prior to public disclosure. However, maintaining this balance requires vigilance from both the development core and the broader user community.
The fragility of this coordinated approach was underscored during the summer months when GeoServer confronted an active zero-day vulnerability. In August, an exploit emerged in the wild without a pre-existing public fix, though the underlying issue had already been flagged privately by several independent security researchers. A remediation patch had been scheduled for inclusion in the forthcoming GeoServer 3.0.1 release, adhering to the standard pipeline.
The situation escalated unexpectedly when an unrelated third party publicly disclosed the vulnerability details on social media platforms. The fallout was immediate and aggressive. Automated security scanners and threat actors began probing for the vulnerability within hours of the social media post. The rapid velocity of this malicious scanning activity triggered widespread media coverage and prompted project leadership to issue urgent upgrade notices across community communication channels, including the official user forums. Project leadership formally acknowledged the swift reporting efforts of security researcher Ravie Lakshmanan, who first notified project leadership via the Open Source Geospatial Foundation.
This incident served as a stark reminder of why coordinated vulnerability disclosure remains paramount. When premature public disclosures bypass established channels, organizations lose their protective buffer, forcing maintainers and system administrators into reactive emergency patching cycles. The subsequent releases of GeoServer 3.0.1, GeoServer 2.28.5, and GeoServer 2.27.6 were rushed out to close this window of exposure, reinforcing the critical need for users to apply updates immediately upon release.
In addition to the August zero-day event, the summer review cataloged previously published vulnerabilities. Earlier in the season, specifically on June 11, 2026, a series of CVEs were disclosed in tandem with the major release of GeoServer 3.0.0. These advisories required subsequent maintenance updates across older branches, including versions 2.27.3, 2.26.4, and specific patches for the 2.27.0 release train. These continuous updates highlight the ongoing complexity of maintaining a robust open-source geospatial platform that relies on a diverse ecosystem of dependencies and libraries.
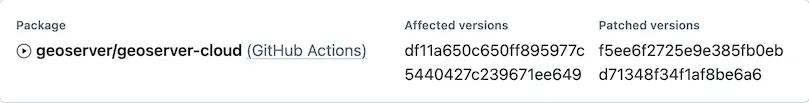
Adding to the complexity of the summer security landscape, the GeoServer project faced its first-ever infrastructure-level supply chain advisory. Supply chain security events carry inherent risks because they have the potential to compromise the integrity of software artifacts downloaded by end users. In this instance, the advisory was officially categorized under "geoserver/geoserver-cloud (GitHub Actions)" because it did not correspond directly to a core release of the GeoServer application itself. Consequently, the incident did not qualify for a traditional CVE number.
Project maintainers moved quickly to clarify the scope of the supply chain warning, emphasizing that no official GeoServer releases were compromised or affected by the GitHub Actions issue. Standard GeoServer releases are compiled and published through a secure Jenkins build server, which distributes the final software artifacts directly to SourceForge and official Open Source Geospatial Foundation (OSGeo) infrastructure, isolating them from the specific cloud pipeline warning flagged in the advisory.
Beyond traditional code vulnerabilities and infrastructure concerns, the GeoServer security team has noted a dramatic shift in how vulnerability reports are generated and submitted. Like many large open-source software projects, GeoServer is currently experiencing an unprecedented wave of security reports produced with the assistance of artificial intelligence tools. While AI can aid researchers in finding anomalies, the resulting submissions often present distinct operational challenges for maintainers.
In response to this trend, the project has established a formal AI Policy and updated its comprehensive Security Policy. These documents are designed to formally acknowledge the utilization of AI-generated content in vulnerability research and to provide clear guidance to submitters. AI-generated reports frequently exhibit extreme verbosity, requiring significantly more time and human effort from core developers to review, evaluate, deduplicate, and verify. Project maintainers have emphasized that when researchers utilize AI tools to generate reports, being readily available to clarify ambiguous findings, test hypotheses, and assist in verifying proposed fixes is invaluable to the overwhelmed security team.
Sustaining the security posture of an enterprise-grade open-source project requires active collaboration from the organizations and individuals who rely on its infrastructure daily. Project leadership continues to call upon corporate users and public institutions to support the ecosystem, whether through direct financial sponsorship or by having technical staff participate actively in the geoserver-security working group. Furthermore, to accommodate public institutions and government bodies that face regulatory or administrative restrictions regarding direct financial sponsorship, the project is actively working to establish alternative pathways for formal project membership.
Administrators frequently question how frequently they need to update their instances to maintain a secure environment. GeoServer operates under a structured, time-boxed release cycle that routinely maintains both "stable" and "maintenance" release branches over the course of any given year. Security guidelines strongly recommend that production environments upgrade to a fully supported release at least once annually to ensure uninterrupted access to critical security patches and bug fixes. Comprehensive upgrading instructions are documented within the official user guide to assist administrators through the migration process.
For those who discover potential security flaws within the software, the project maintains a clear and structured protocol. Vulnerabilities should never be disclosed publicly before a fix is prepared; instead, they must be reported privately using the GitHub security advisories mechanism outlined in the project’s security policy. Through these ongoing measures, the GeoServer community continues to adapt to an evolving threat landscape defined by rapid zero-day exploits, complex supply chains, and the rising tide of AI-driven vulnerability discovery.