As the summer of 2026 draws to a close, the GeoServer project has published a comprehensive security recap detailing a series of advisories, newly assigned Common Vulnerabilities and Exposures (CVEs), a notable supply chain incident, and an updated organizational policy addressing the influx of artificial intelligence-assisted vulnerability reports. The overarching message for administrators and organizations running geospatial infrastructure is clear and urgent: maintaining secure operations requires proactive upgrading, with immediate attention directed toward the latest patch releases.
For system administrators and IT professionals responsible for managing GeoServer instances, the immediate remediation path involves moving swiftly to recently issued software versions. The project team has strongly urged users to update their deployments to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6. These updates contain critical fixes designed to secure instances against vulnerabilities that have recently surfaced, reinforcing the project’s ongoing commitment to platform stability and data integrity.
The GeoServer project maintains a strict coordinated vulnerability disclosure policy. Under this framework, security flaws are thoroughly investigated and fixed across both stable and maintenance release branches before any CVE details or technical specifics are made public. This methodology is designed to give the global user community a fair and adequate opportunity to apply updates and secure their environments prior to public disclosure, thereby minimizing the window of exposure for operational systems.
However, maintaining the delicate balance of coordinated disclosure was severely tested during the summer months when GeoServer encountered a high-profile zero-day vulnerability in August. A zero-day vulnerability refers to a security flaw that is actively being exploited in the wild before an official fix has been publicly released and widely distributed. In this instance, the underlying issue had already been reported privately to the project by several independent security researchers, and a formal fix was already actively scheduled for inclusion in the forthcoming GeoServer 3.0.1 release.
The zero-day crisis materialized when an unrelated third party—completely disconnected from both the core project development team and the original researchers who discovered the flaw—publicly disclosed the vulnerability details on social media. The consequences of this premature disclosure were immediate and severe. Automated scans and targeted exploitation attempts against unpatched GeoServer instances were detected within hours of the public social media post going live.
The velocity of the attacker response was remarkable, quickly attracting widespread industry news coverage and forcing the project leadership to issue urgent calls for updates across official user forums. Project leadership formally acknowledged the situation and extended their gratitude to reporter Ravie Lakshmanan, who first notified project leadership through the Open Source Geospatial Foundation. This intense experience powerfully reaffirmed the fundamental importance of strictly adhering to coordinated vulnerability disclosure policies and underscored why community members must apply patches immediately upon release.
In addition to the August zero-day event, the summer review also cataloged previously published CVEs that had entered the public domain earlier in the season. These included security notices published on June 11, 2026, which coincided directly with the major feature release of GeoServer 3.0.0. Those disclosures addressed specific flaws within older branches, prompting updates such as GeoServer 2.27.3, GeoServer 2.26.4, and GeoServer 2.27.0, illustrating the continuous maintenance effort required to secure complex open-source geospatial mapping software.
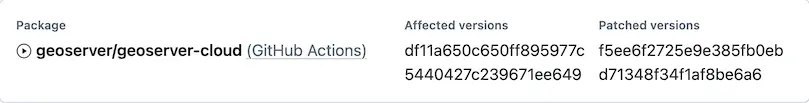
Beyond traditional application-level vulnerabilities, the summer months also brought a unique challenge in the form of a supply chain advisory. Supply chain advisories inherently carry the potential to undermine the cryptographic integrity and trustworthiness of software packages downloaded by end users. This marked the very first time the GeoServer project has had to navigate an infrastructure-level advisory of this nature. Because the incident did not correspond directly with a standard source code release of GeoServer itself, the advisory was formally categorized under the GitHub Actions identifier for geoserver/geoserver-cloud, rendering it ineligible for a traditional CVE tracking number.
Crucially, project maintainers emphasized that no official GeoServer software releases were compromised or affected by this supply chain event. Standard GeoServer releases continue to be compiled and distributed using a dedicated Jenkins build server that securely publishes verified artifacts to both SourceForge and official OSGeo infrastructure repositories. The transparency surrounding this infrastructure advisory demonstrates the project’s dedication to maintaining absolute clarity regarding software supply chain security.
Another prominent theme of the summer review was the escalating volume of automated security submissions. Like many large and active open-source software projects, the GeoServer security team has experienced a substantial wave of vulnerability reports generated with the assistance of artificial intelligence tools. While AI can sometimes assist in identifying patterns, the sheer volume of verbose and often repetitive AI-generated reports has created a significant administrative and technical review burden for the volunteer-driven security team.
In response to this modern trend, the project has established a general AI policy and updated its overarching security policy. These governance documents formally acknowledge the existence and utilization of AI-assisted tools in security research while providing clear guidance for submitters. Project maintainers noted that when dealing with verbose AI-generated reports, human availability to clarify ambiguous technical claims, verify findings, and test potential fixes is immensely appreciated. Reducing the friction involved in reviewing duplicate or low-quality automated reports helps the security team direct its limited resources toward genuine risks.
As the project looks toward the future, maintainers have outlined several ways for the broader community to contribute to the long-term health and security of GeoServer. Organizations whose operational capabilities depend heavily on GeoServer are encouraged to consider financial sponsorship or to allow their technical staff to directly participate in the work of the geoserver-security team. Furthermore, the project is actively working to establish formal project membership pathways specifically tailored for public institutions and government agencies that frequently face administrative or legal restrictions regarding direct corporate sponsorship and participation.
Addressing questions regarding upgrade cadences, project maintainers reiterated that GeoServer operates on a structured, time-boxed release cycle. This cycle actively maintains both stable and maintenance release branches over the course of each year. Organizations are strongly advised to upgrade their deployments to a supported, patched release at least once every twelve months to ensure continuous coverage against newly discovered security issues, utilizing the official User Guide documentation for upgrade procedures.
For security researchers and administrators seeking to report newly discovered vulnerabilities, the project continues to enforce private disclosure channels. Submissions should be handled strictly through the established security policy guidelines, utilizing private reporting mechanisms such as GitHub security advisories to ensure that fixes can be properly engineered, tested, and deployed before malicious actors can leverage them against global geospatial infrastructure.