The maintainers of the widely used open-source GeoServer project have issued a comprehensive security recap detailing a turbulent summer of 2026. The period was marked by newly disclosed Common Vulnerabilities and Exposures (CVEs), a high-profile zero-day exploit, a supply chain advisory, and a growing influx of AI-assisted vulnerability reports that have prompted updates to the project’s security policies.
For administrators and organizations responsible for managing GeoServer instances, the immediate imperative is clear. The project team strongly urges all users to update their systems to the newly released patches: GeoServer version 3.0.1, GeoServer version 2.28.5, or GeoServer version 2.27.6. These releases contain critical fixes designed to protect spatial data infrastructures from active exploitation.
The GeoServer project traditionally operates under a strict coordinated vulnerability disclosure policy. Under this framework, security flaws are collaboratively identified, analyzed, and patched across both stable and maintenance release lines before any official CVE details or technical descriptions are made public. The overarching goal of this coordinated approach is to give administrators a fair window of opportunity to apply necessary updates, thereby preventing attackers from leveraging newly discovered flaws against unprepared systems.
However, this summer’s security landscape tested those mechanisms significantly, most notably during an incident involving an August zero-day vulnerability. The flaw, which represented an active exploit in the wild with no pre-existing official fix, had already been brought to the attention of project maintainers through private disclosures by several independent security researchers. A formal patch had already been scheduled for inclusion in the forthcoming GeoServer 3.0.1 release.
The zero-day situation escalated unexpectedly when an unconnected third party publicly disclosed details of the vulnerability on social media platforms. The public disclosure bypassed the coordinated timeline entirely. Within hours of the social media post, automated scanning activity and active exploitation attempts targeting the vulnerability were detected across the internet.
The rapid weaponization of the flaw triggered widespread media coverage and prompted project leadership to issue urgent upgrade warnings across official user forums. Project leaders extended their gratitude to reporter Ravie Lakshmanan for first notifying project leadership via the Open Source Geospatial Foundation, helping galvanize the rapid response. This intense experience heavily underscored the critical importance of adhering strictly to coordinated vulnerability disclosure timelines and emphasized why prompt action from system administrators is necessary the moment new maintenance releases become available.
The summer security advisory cycle also encompassed previously published CVEs that initially came to light earlier in the season. These included security updates tied to the major GeoServer 3.0.0 release in June, as well as targeted patches for the 2.27 and 2.26 maintenance branches. Managing multiple active release streams requires substantial coordination from the core development team, balancing new feature rollouts with the rigorous demands of ongoing vulnerability management.
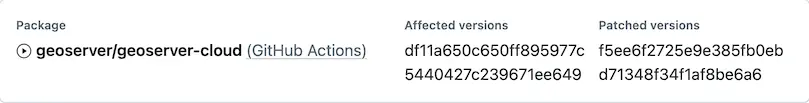
In addition to traditional code-level vulnerabilities, the project encountered a distinct challenge involving a supply chain advisory. Because supply chain advisories have the potential to compromise the integrity of downloaded software components, handling them requires immense transparency. This particular incident marked the first time the GeoServer project had to navigate an infrastructure-level advisory of this nature. Because the issue was tied to GitHub Actions workflows within the geoserver/geoserver-cloud repository rather than an official software release, it did not qualify for a traditional CVE number.
Project maintainers were quick to reassure the user community that no official GeoServer software releases were affected by the cloud infrastructure advisory. Standard GeoServer releases are compiled and published through a secure Jenkins build server infrastructure, distributing verified artifacts directly through SourceForge and official OSGeo hosting infrastructure.
Beyond external vulnerabilities and supply chain considerations, the project has also found itself grappling with a modern software development phenomenon: a significant wave of security vulnerability reports generated with the assistance of artificial intelligence. Like many large open-source projects, GeoServer has seen an influx of AI-generated vulnerability submissions.
In response to this trend, the project has established a general AI policy and updated its core security policy on GitHub. These policy updates are designed to formally acknowledge the use of AI tools in security research and provide clear guidance to researchers utilizing them. While automated tools can assist in identifying potential code paths, AI-generated reports are frequently very verbose and often require extensive manual review by maintainers to validate, rule out false positives, or determine if a submission is simply a duplicate of an existing ticket.
Project maintainers emphasize that community members who are familiar with the codebase can provide invaluable assistance by helping review, test, and verify fixes as they are developed. Reducing the administrative and verification burden on the core security team directly accelerates the delivery of stable patches.
For organizations whose core business operations and spatial data services rely heavily on GeoServer, project leadership encourages deeper forms of engagement. Institutions and enterprises can support the ongoing health and security of the platform by financial sponsorship or by having technical staff directly participate in the geoserver-security working groups and mailing lists. Furthermore, the project is actively working to establish formal project membership pathways for public sector institutions that may face bureaucratic or legal restrictions regarding direct financial sponsorship.
Addressing questions regarding maintenance schedules, project maintainers remind the community that GeoServer follows a structured time-boxed release cycle. Over the course of any given year, the project maintains parallel stable and maintenance release lines. Organizations are strongly advised to establish a regular upgrade cadence, updating their production and staging environments to a supported release at least once every year to ensure continuous access to security patches and bug fixes. Comprehensive instructions and upgrade paths are documented in the official GeoServer User Guide to assist administrators through the transition process.
For security researchers and community members seeking to report newly discovered vulnerabilities, the project maintains clear and confidential reporting channels. Private vulnerability disclosures should be submitted through GitHub security advisories in accordance with the project’s established security policy, ensuring that issues can be properly vetted and patched before public awareness leads to potential exploitation.