The GeoServer open-source project has published a comprehensive security recap detailing a turbulent summer of 2026, which included managing a critical zero-day exploit, addressing prior Common Vulnerabilities and Exposures (CVEs), navigating a supply chain infrastructure advisory, and updating project policies to handle a growing surge of AI-generated security reports.
For administrators and organizations responsible for maintaining mapping and geospatial infrastructure, the immediate operational directive is clear: systems must be updated promptly. Project maintainers strongly urge users to upgrade to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6 to mitigate the risks exposed over recent months.
The GeoServer project traditionally operates under a strict coordinated vulnerability disclosure policy. Under this framework, security flaws are investigated, patches are developed, and fixes are applied to both stable and maintenance releases prior to the public publication of CVE details or technical specifics. This methodology is specifically designed to provide administrators with an adequate window of opportunity to apply updates and secure their environments before malicious actors can weaponize the flaws. However, maintaining this protective buffer was severely tested during the summer months due to premature disclosures and shifting industry landscapes.
The August Zero-Day Incident
The most critical event of the period occurred in August, when GeoServer was hit with a zero-day vulnerability—an active exploit in the wild with no official patch immediately available to the general public at the moment of disclosure. Prior to the public breach, the underlying problem had already been privately identified and reported by several independent researchers. A permanent fix had been scheduled for inclusion in the forthcoming GeoServer 3.0.1 release.
The zero-day situation escalated rapidly when a third party, entirely unconnected to the project or the original researchers who discovered the issue, publicly disclosed the vulnerability on social media. The consequences of this premature disclosure were instantaneous and severe. Automated scans searching for vulnerable GeoServer instances were detected within hours of the public social media post, catching the project off guard and forcing an immediate response.
The speed of the community and project response was remarkable. News coverage quickly picked up the unfolding story, prompting urgent calls to action and upgrade warnings across the official GeoServer user forums. Project leadership publicly expressed gratitude to reporter Ravie Lakshmanan, who first notified project leadership through the Open Source Geospatial Foundation. The incident starkly reaffirmed the vital importance of adhering to coordinated vulnerability disclosure policies and underscored why system administrators must apply new releases the moment they become available.
Previously Published CVEs and Release Cycles
The summer security updates also encompassed vulnerability disclosures from earlier in the season. On June 11, 2026, alongside the major release of GeoServer 3.0.0, a series of CVEs were published. These vulnerabilities required targeted updates across multiple active branches, specifically affecting deployments running GeoServer versions 2.27.3, 2.26.4, and 2.27.0.
These updates reflect GeoServer’s structured approach to software lifecycle management. The project operates on a time-boxed release cycle that maintains both stable and maintenance release branches over the course of a year. To maintain robust defense postures, maintainers advise organizations to upgrade to a supported release at least once every twelve months to ensure continuous coverage for newly discovered security issues. Comprehensive upgrade instructions are maintained within the official user guide documentation to assist administrators through the transition processes.
Supply Chain Advisory and Infrastructure Integrity
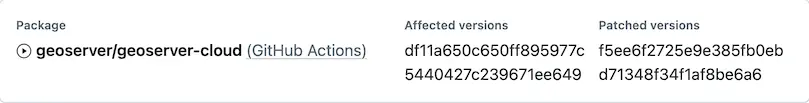
In addition to direct application vulnerabilities, the project encountered its first-ever infrastructure supply chain advisory. Because this particular advisory did not correspond to a direct release of the GeoServer application code, it did not qualify for a traditional CVE number. Instead, project maintainers categorized the advisory specifically under GitHub Actions for the geoserver/geoserver-cloud repository.
Crucially, project leadership emphasized that no official GeoServer releases were compromised or affected by this supply chain event. Standard GeoServer production releases continue to be compiled using an isolated Jenkins build server, which subsequently publishes verified artifacts to both SourceForge and official OSGeo infrastructure repositories. This distinction highlights the growing complexity of software supply chains, where ancillary development and automation pipelines can face scrutiny independent of the core application binaries.
Managing the Wave of AI-Assisted Vulnerability Reports
Beyond traditional software bugs and infrastructure challenges, the GeoServer project reported a significant operational hurdle: an unprecedented wave of security vulnerability reports generated with the assistance of artificial intelligence tools.
Like many open-source software initiatives across the global technology ecosystem, GeoServer maintainers are spending substantial time processing verbose, AI-generated reports. These submissions frequently introduce administrative bottlenecks, as they often require extensive manual review just to determine authenticity or identify whether a report is merely a duplicate of an existing ticket. Furthermore, validating these findings and testing potential fixes demands specialized domain knowledge and significant human hours from the core security team.
To address this modern shift, the project has established a dedicated general AI policy and updated its core security policy on GitHub. These updated guidelines explicitly acknowledge the integration of AI-generated content in vulnerability submissions and provide clear instructions for researchers using these tools. Project leadership has noted that when researchers utilize AI tools to generate reports, being readily available to clarify details, test patches, and assist the geoserver-security team is deeply appreciated and critically necessary to keep the development cycle moving forward.
Community Involvement and Reporting Guidelines
As the scope of security maintenance grows more complex, the GeoServer project continues to rely heavily on its user base and institutional partners for support. Organizations that rely extensively on geospatial data infrastructure are encouraged to consider formal project sponsorship or to allow their technical staff to participate directly in the geoserver-security working groups. Additionally, the project is actively working to establish formal project membership pathways for public institutions and government agencies that frequently face administrative or legal restrictions regarding traditional financial sponsorship and corporate participation.
For individuals or organizations needing to report a newly discovered security vulnerability, the project mandates strict adherence to private disclosure guidelines. Security issues should never be posted to public trackers or social media channels. Instead, reports must be submitted privately using GitHub security advisories, allowing the core development team adequate time to investigate, develop patches, and coordinate secure releases across the global ecosystem.