As the open-source community reflects on the security landscape of the summer of 2026, the GeoServer project has issued a comprehensive review of recent vulnerability disclosures, a critical supply chain advisory, and vital updates to its administrative security policies. Central to this summer update is an urgent call for administrators managing GeoServer instances to apply the latest security releases immediately to protect their geospatial data infrastructure from active exploitation.
For organizations responsible for deploying and maintaining GeoServer instances, the primary and most immediate action required is updating to the newly issued versions. Project maintainers have strongly urged administrators to upgrade to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6 depending on their active deployment branches. These releases contain critical patches designed to address vulnerabilities that came to light during the peak of the summer season.
The GeoServer project traditionally operates under a strict coordinated vulnerability disclosure policy. Under this framework, security flaws are thoroughly investigated, validated, and resolved across both stable and maintenance release branches before any Common Vulnerabilities and Exposures (CVE) details are made publicly available. The foundational goal of this cooperative approach is to provide system administrators, enterprise users, and institutional stakeholders with adequate opportunity to apply necessary updates and fortify their systems prior to public knowledge of the flaws, thereby minimizing the window of exposure for live production environments.
The August Zero-Day Incident
The resilience of this coordinated disclosure model was severely tested in August, when GeoServer encountered a high-profile zero-day vulnerability—defined as a security flaw actively exploited in the wild with no official patch immediately available to the broader public. Prior to this public breach, the underlying problem had already been privately reported to the project by several independent security researchers, and a formal remediation had already been scheduled for inclusion in the forthcoming GeoServer 3.0.1 release.
The emergency zero-day situation materialized when an unrelated third party, operating completely outside the core project development team and independent of the original researchers, chose to bypass standard disclosure protocols and publish details of the vulnerability openly on social media. The fallout from this premature disclosure was swift and measurable. Automated security scanners and malicious actors began actively probing for the newly publicized vulnerability within hours of the social media post going live.
The remarkable speed with which malicious entities mobilized triggered immediate media coverage from prominent cybersecurity outlets, alongside urgent warnings broadcast across official user forums. Project leadership extended formal public gratitude to security researcher Ravie Lakshmanan for initially notifying project leadership through the channels of the Open Source Geospatial Foundation. The swift deployment of GeoServer 3.0.1, alongside updated maintenance versions 2.28.5 and 2.27.6, helped stem the tide of potential exploitation. Nevertheless, project leaders noted that the incident powerfully reaffirmed the critical importance of adhering to coordinated vulnerability disclosure timelines and emphasized the absolute necessity for the user community to apply patches the moment official updates are published.
Previously Published CVEs and Release Cycles
The summer security review also accounted for a series of vulnerabilities published earlier in the season. On June 11, 2026, alongside the major release of GeoServer 3.0.0, project maintainers published a wave of CVEs affecting earlier iterations of the software, prompting simultaneous maintenance updates for branches such as GeoServer 2.27.3, 2.26.4, and the foundational 2.27.0 release.
To manage this continuous stream of updates, GeoServer operates on a structured time-boxed release cycle. Over the course of any given year, the project actively maintains separate "stable" and "maintenance" release branches. Because software vulnerabilities are an inevitable reality in complex enterprise applications, project maintainers strongly advise organizations to upgrade their instances to a supported release at least once every year. Maintaining an annual upgrade cadence ensures that production environments continue to receive vital security fixes and architectural improvements. Comprehensive guidance for managing these transitions is readily available through the official user guide documentation under the existing upgrade protocols.
Supply Chain Advisory and Build Infrastructure
In addition to traditional application-level vulnerabilities, the summer of 2026 brought a unique challenge involving the project’s software supply chain. Supply chain advisories carry distinct implications because they have the potential to undermine the baseline integrity of the software packages downloaded by end users.
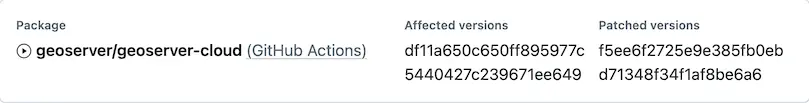
This marked the first time the GeoServer project had to navigate an infrastructure-level advisory of this nature. Because the advisory specifically pointed to issues within the geoserver/geoserver-cloud GitHub Actions build pipelines rather than a direct flaw in the source code of an official application release, it did not neatly map to traditional CVE numbering criteria.
Crucially, project leadership confirmed that no official GeoServer releases were compromised or affected by the incident. Standard GeoServer production releases are compiled and distributed using an isolated Jenkins build server, which publishes verified artifacts directly to SourceForge and official Open Source Geospatial Foundation (OSGeo) infrastructure repositories. This strict separation of development pipelines ensured that user downloads remained secure, even as the project addressed the cloud configuration advisory.
AI-Assisted Vulnerability Reports and Policy Updates
Mirroring a broader trend affecting open-source software projects across the global technology ecosystem, GeoServer has experienced a dramatic surge in vulnerability reports generated with the assistance of artificial intelligence tools. While automated and AI-assisted scanning can sometimes help identify potential code anomalies, they frequently produce large volumes of verbose, generalized, or redundant submissions that require significant manual triage by volunteer maintainers.
To address this growing operational challenge, the project has established a dedicated general AI policy and updated its core security policy on GitHub. These policy documents are designed to acknowledge the shifting landscape of security reporting, set clear expectations for researchers utilizing AI generation tools, and provide practical guidance on how submissions should be formatted and verified.
Project maintainers have noted that dealing with AI-generated reports often demands a substantial investment of time to properly review, de-duplicate, and validate. Consequently, the project has emphasized that having security contributors on hand to clarify verbose reports, test proposed patches, and verify fixes is immensely valuable. Any community efforts that streamline the workload for the core security team directly contribute to the long-term stability and responsiveness of the project.
Sustaining the Project and Reporting Security Issues
As the demands on core maintainers continue to evolve, the GeoServer project relies heavily on the active participation and financial backing of the organizations that depend on its technology. Enterprises and commercial entities that rely on GeoServer for critical geospatial operations are encouraged to support the project financially through sponsorship programs or by allowing internal engineering staff to directly participate in the geoserver-security working groups. Furthermore, the project is actively working to establish formal project membership pathways specifically tailored for public institutions and government agencies that frequently face administrative or legal restrictions regarding traditional commercial sponsorship.
For security researchers and system administrators seeking to report newly discovered vulnerabilities, the project maintains a strict private disclosure protocol. Rather than resorting to public disclosure or social media channels, individuals are instructed to consult the official security policy hosted on the project’s GitHub repository, which outlines the secure procedures for submitting vulnerability details privately via GitHub security advisories.