The open-source geospatial community is reckoning with a demanding summer of security updates, highlighted by a high-profile zero-day vulnerability, multiple CVE disclosures, and evolving challenges surrounding automated security reports. Administrators and organizations relying on GeoServer instances are being strongly urged to apply the latest round of patches immediately to secure their mapping infrastructure against potential exploitation.
Project maintainers have published a comprehensive recap of the security advisories issued throughout the summer of 2026. The update addresses a wave of recently published Common Vulnerabilities and Exposures (CVEs), a notable supply chain advisory affecting auxiliary components of the ecosystem, and a growing influx of automated security submissions. At the center of this maintenance cycle is an urgent call for administrators to update their systems to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6 without delay.
The GeoServer project traditionally operates under a strict coordinated vulnerability disclosure policy. Under this framework, security flaws are identified, investigated, and patched across both stable and maintenance release lines prior to any public disclosure of CVE details. This methodology is designed to give system administrators a vital window of opportunity to apply updates and protect their networks before malicious actors become aware of the specific mechanics behind a flaw. However, recent events during the summer months tested the limits of this coordinated approach, putting the spotlight on the speed at which unpatched vulnerabilities can transition from obscurity to active targeting.
The August Zero-Day Incident
The most critical test for the project arrived in August, when GeoServer was struck by a zero-day vulnerability—an active exploit in the wild for which no official patch had yet been publicly released. Prior to the incident, the underlying problem had already been handled through private channels by several independent researchers who reported it responsibly. A remediation plan and fix had been scheduled to coincide with the planned rollout of GeoServer 3.0.1.
The containment strategy shifted abruptly, however, when an unrelated third party publicly disclosed the vulnerability on social media. The external poster had no connection to the GeoServer project team or to the original researchers who had discovered and reported the issue. The fallout from the premature disclosure was immediate and severe. Within hours of the social media post appearing online, automated security scans searching for vulnerable instances were detected across the internet, demonstrating how rapidly threat actors can weaponize prematurely disclosed technical details.
The speed and aggressiveness of the scanning activity triggered an urgent response from project leadership. The incident quickly garnered outside media coverage, prompting emergency notices and urgent calls to action posted across the official OSGeo user forum. Project leadership formally acknowledged the swift reporting and communication efforts surrounding the crisis, thanking security researcher Ravie Lakshmanan for initially notifying project leadership via the Open Source Geospatial Foundation.
This turbulent episode has strongly reaffirmed the critical necessity of adhering to coordinated vulnerability disclosure practices. Maintainers continue to emphasize that when new patched versions are made available, administrators must act promptly to update their deployments before details can be hijacked by unauthorized third parties.
Previously Published CVEs and Release Cycles
The summer security review also accounted for vulnerability disclosures made earlier in the season. On June 11, 2026, a series of CVEs were published in tandem with the major release of GeoServer 3.0.0. These earlier advisories targeted various components within the software stack, prompting subsequent updates across the active maintenance branches, including versions 2.27.3, 226.4, and 227.0.
These updates are part of GeoServer’s established time-boxed release cycle, which systematically manages stable and maintenance branches over the course of a calendar year. Project maintainers continually remind the user community that staying secure requires regular maintenance. Organizations are strongly advised to upgrade their operational GeoServer instances to a supported release at least once a year to ensure they continue receiving vital security backports and patches. Detailed upgrade paths and instructions remain documented in the official user guide to assist system administrators through the migration process.
Navigating Supply Chain Advisories
Beyond direct application vulnerabilities, the project recently encountered its first encounter with an infrastructure-level supply chain advisory. Because supply chain concerns have the potential to compromise the integrity of downloaded software artifacts, transparency remains a priority for the core team.
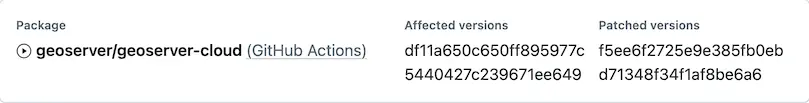
In this instance, the advisory was officially categorized under the label "geoserver/geoserver-cloud (GitHub Actions)" because it did not map cleanly to a standard release of the core GeoServer application. Consequently, the issue did not qualify for a traditional CVE number. Project leaders emphasized a crucial distinction for users: no official GeoServer releases were impacted by the supply chain advisory. Standard GeoServer releases continue to be compiled securely using an internal Jenkins build server that publishes verified artifacts directly to SourceForge and the official OSGeo infrastructure.
Managing AI-Assisted Vulnerability Reports
Like many other prominent open-source software projects, the GeoServer maintainers are currently navigating a significant wave of security vulnerability reports generated with the assistance of artificial intelligence tools. While AI technologies can aid in identifying potential code issues, they frequently produce a high volume of verbose, complex, or duplicate submissions that require substantial manual effort from core developers to triage.
To address this modern challenge constructively, the project has established a dedicated general AI policy and updated its core security policy on GitHub. These policy documents formally acknowledge the utilization of AI tools in security research and provide clear guidance for researchers submitting findings.
Reviewing AI-assisted reports demands considerable time from the security team, particularly when sorting through redundant submissions or verifying complex, automated findings. Maintainers have expressed that having researchers on hand to clarify verbose reports, test hypotheses, and verify fixes greatly alleviates the administrative burden on the volunteer-driven geoserver-security team.
Community Support and Engagement
Maintaining a complex, widely deployed open-source geospatial platform requires continuous effort and collaboration between developers, institutions, and the organizations that rely upon the software every day. The GeoServer project relies heavily on community backing to sustain its security operations and development roadmap.
Organizations whose operational workflows depend heavily on GeoServer are encouraged to consider financial sponsorship of the project or to support the direct participation of their engineering staff in the geoserver-security working group. Furthermore, to accommodate public institutions and government agencies that often face rigid legal or bureaucratic restrictions regarding direct corporate sponsorship and open-source participation, the project is actively working to establish formal project membership frameworks via specific initiatives like GSIP-243.
For those seeking to report newly discovered security concerns, the project maintains strict guidelines. Security researchers are instructed to review the official security policy and utilize private reporting channels via GitHub security advisories to ensure vulnerabilities are handled responsibly before any public discussion or patching takes place.