The open-source geospatial community has experienced a demanding and eventful summer in 2026, marked by critical security advisories, a high-profile zero-day exploit, a supply chain warning, and a noticeable influx of automated security submissions. Project maintainers for GeoServer have released a comprehensive recap of these developments, accompanied by an urgent call to action for system administrators worldwide to update their deployments to the latest secure versions.
For organizations and infrastructure managers responsible for maintaining active mapping and geospatial services, the immediate takeaway from the summer security cycle is clear: administrators must promptly update their software instances. The GeoServer project has rolled out targeted patches across its supported branches, resulting in the launch of GeoServer 3.0.1, GeoServer 2.28.5, and GeoServer 2.27.6.
Maintaining the integrity of distributed geospatial infrastructure relies heavily on coordinated disclosure practices. Under its standard operating procedures, the GeoServer project strictly adheres to a coordinated vulnerability disclosure policy. This framework ensures that security flaws are fully resolved and patches are prepared for both stable and maintenance releases prior to any public disclosure of Common Vulnerabilities and Exposures (CVE) details. The primary objective of this coordinated approach is to provide all users and system administrators with an adequate window of opportunity to apply necessary updates before malicious actors can weaponize the underlying weaknesses.
The August Zero-Day Incident
The fragility of this defensive window was underscored during a tense period in August, when GeoServer encountered a severe zero-day vulnerability—an active exploit in the wild with no pre-existing official fix available at the time of discovery. Prior to the public exposure, the underlying problem had already been privately reported to project maintainers by several independent security researchers, and a formal remedy had already been scheduled for inclusion in the forthcoming GeoServer 3.0.1 release.
However, the situation escalated rapidly when an unrelated third party, operating completely independently of the project leadership and the original reporting researchers, publicly disclosed the technical details of the vulnerability on social media. The consequences were immediate and dramatic. Automated security scanners and malicious actors began probing for vulnerable instances within hours of the public social media post.
The velocity of this malicious response triggered widespread media attention, alongside an urgent, high-priority call to action distributed across the official GeoServer user forum. Project leadership expressed deep gratitude to security researcher Ravie Lakshmanan, who first notified project leadership through the Open Source Geospatial Foundation, helping mobilize the rapid response that culminated in the swift delivery of GeoServer 3.0.1, GeoServer 2.28.5, and GeoServer 2.27.6.
This high-pressure incident forcefully reaffirmed the critical importance of adhering strictly to coordinated vulnerability disclosure principles. It also served as a stark reminder of why system administrators must prioritize applying new updates the moment they are made publicly available by the development team.
Previously Published CVEs and Release Cycles
The summer security updates built upon a foundation established earlier in the season. On June 11, 2026, coinciding with the major milestone release of GeoServer 3.0.0, project maintainers published a series of CVEs addressing various historical vulnerabilities across older iterations. These included specific security adjustments applied to the 2.27.3, 2.26.4, and 2.27.0 branches.
Navigating these frequent security updates requires an understanding of how the project manages its software lifecycle. GeoServer operates on a structured, time-boxed release cycle that maintains both designated stable and maintenance releases over the course of any given year. Because the threat landscape constantly evolves, project maintainers strongly advise organizations to upgrade their deployments to a supported release at least once every year to ensure uninterrupted access to critical security fixes and patches. Comprehensive guidance for managing these transitions can be found within the official user guide documentation under the upgrading existing versions section.
Supply Chain Advisory and Infrastructure Security
In addition to direct software vulnerabilities, the summer of 2026 brought unique challenges concerning software integrity. For the first time in its history, the GeoServer project had to address and work through a supply chain infrastructure advisory.
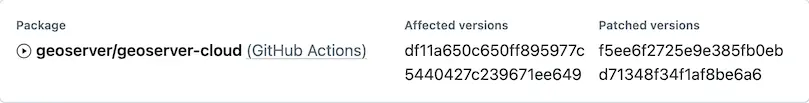
Because supply chain advisories directly impact the trustworthiness of downloaded software, they command immediate scrutiny. In this specific instance, the advisory was formally categorized under "geoserver/geoserver-cloud (GitHub Actions)." Project maintainers emphasized that this advisory did not correspond to an official release of GeoServer itself, and consequently, it did not qualify for a traditional CVE number.
Crucially, project leadership confirmed that no official GeoServer releases were compromised or affected by the incident. Standard GeoServer releases are compiled and distributed using a dedicated Jenkins build server that publishes verified artifacts to both SourceForge and official OSGeo infrastructure, maintaining a strict firewall between cloud-based CI/CD workflows and the distribution of stable software binaries.
The Rising Wave of AI-Assisted Vulnerability Reports
Beyond traditional exploits and supply chain warnings, the GeoServer security team has faced an unprecedented operational hurdle: a massive surge in vulnerability reports generated with the assistance of artificial intelligence tools.
Like many prominent open-source software projects, GeoServer has experienced a wave of verbose, automated, or semi-automated vulnerability submissions. Reviewing these AI-generated reports requires a significant investment of time and engineering effort, particularly when determining whether multiple lengthy submissions represent duplicate findings or distinct issues.
To manage this evolving landscape, the project has established a formal AI Policy and updated its broader Security Policy. These documents explicitly acknowledge the growing utilization of AI generation tools and provide clear guidance for researchers. Maintainers emphasize that when utilizing AI tools to scan and report on software, human oversight and a willingness to remain on hand to clarify complex or verbose reports are deeply appreciated. Having researchers available to test and verify proposed fixes significantly eases the burden on the volunteer-driven geoserver-security team.
Community Participation and Reporting Vulnerabilities
As the demands on open-source maintainers continue to grow, the GeoServer leadership team has actively encouraged deeper community involvement to ensure the long-term sustainability of the project’s security operations.
Organizations that rely heavily on GeoServer for their critical geospatial infrastructure are urged to consider financial sponsorship or to authorize their internal technical staff to participate directly in the geoserver-security working group. Furthermore, the project is actively working to establish alternative pathways for project membership, specifically tailored for public institutions and government agencies that often face rigid institutional restrictions regarding corporate sponsorship and direct open-source participation.
For security researchers and developers seeking to report newly discovered vulnerabilities, the project maintains a strict protocol. Individuals are requested to consult the official security policy guidelines for detailed instructions on how to submit vulnerability details privately using GitHub security advisories, ensuring that bugs can be remediated safely before any public disclosure occurs.