U.S. federal investigators pursuing the notorious ShinyHunters hacking group—which recently compromised sensitive U.S. government data, including high-profile breaches targeting the FBI—have identified executives at two separate ransomware negotiation firms who maintained unusually close and illicit relations with the extortion collective. According to sources close to the unfolding federal probe, at least one of these executives, based in the United States, actively assisted the ShinyHunters operation by helping to run a public website designed to pressure victims into paying exorbitant ransoms.
The revelations mark a significant escalation in an international cybersecurity investigation that has increasingly focused on the intersection between cybercriminals and the corporate middlemen hired to handle them. Hackers aligned with ShinyHunters have claimed responsibility for dozens of major corporate and institutional data breaches dating back to 2019. In its early days, the group was primarily operated by cybercriminals residing in France. However, as those original members were systematically arrested, extradited, or jailed, control over the ShinyHunters brand eventually passed to a teenage hacker from Amman, Jordan, known online as "Rey," who was identified by authorities last year. According to estimates provided by the FBI, ShinyHunters has successfully extorted more than $70 million from victims globally this year alone.
The group’s operational audacity reached a peak in late September, when ShinyHunters compromised the FBI recruitment website, fbijobs.gov. The hackers publicly taunted law enforcement by threatening to publish a cache of stolen internal files. Reports indicated that the compromised data included sensitive medical and psychological records, Social Security numbers, home addresses, and detailed information regarding the individual specializations and units of agency employees.
The breach of the FBI jobs portal prompted the bureau to move with uncommon speed, detaining and questioning individuals who had maintained communications with Rey or other suspects linked to the ShinyHunters network. On October 3, Reuters reported that Rey had been detained by Jordanian authorities and was actively cooperating with federal investigators.

Rey’s ascent to administrative control over the hacking group had been enabled by the sudden incapacitation of a senior member. On the evening of September 15, law enforcement officers in the Netherlands executed a high-stakes raid, arresting convicted hacker and ShinyHunters suspect Pepijn van der Stap. Dutch police reportedly deployed flash-bang grenades to stun and apprehend Van der Stap while he remained actively logged into various online accounts.
According to sources close to the investigation, authorities apprehended Van der Stap while he was using his Signal instant messaging account. This tactical advantage allowed investigators to immediately inspect recent communications with frequent contacts, including ransomware negotiators located in Canada and the United States.
Multiple sources with direct knowledge of the matter revealed that Van der Stap’s Signal messages served as a critical roadmap for investigators, helping to unravel a separate murder-for-hire plot that surfaced immediately following his arrest. The Dutch news outlet RTL reported that two murders were allegedly planned to be carried out abroad, with indications pointing to Van der Stap as the individual who issued the orders, though investigators found no evidence that the plots were ever executed.
On October 9, federal authorities arrested a 54-year-old Canadian cybersecurity executive named Edward Dubrovsky in connection with the broadening ShinyHunters investigation. Dubrovsky, who recently published a book on handling cyber extortion that advised companies to always engage with hackers, was charged in U.S. court with threatening to disclose stolen data and interfering with interstate commerce through extortion. Prosecutors subsequently asked that Dubrovsky remain in custody pending trial, with court records related to the case kept under seal.
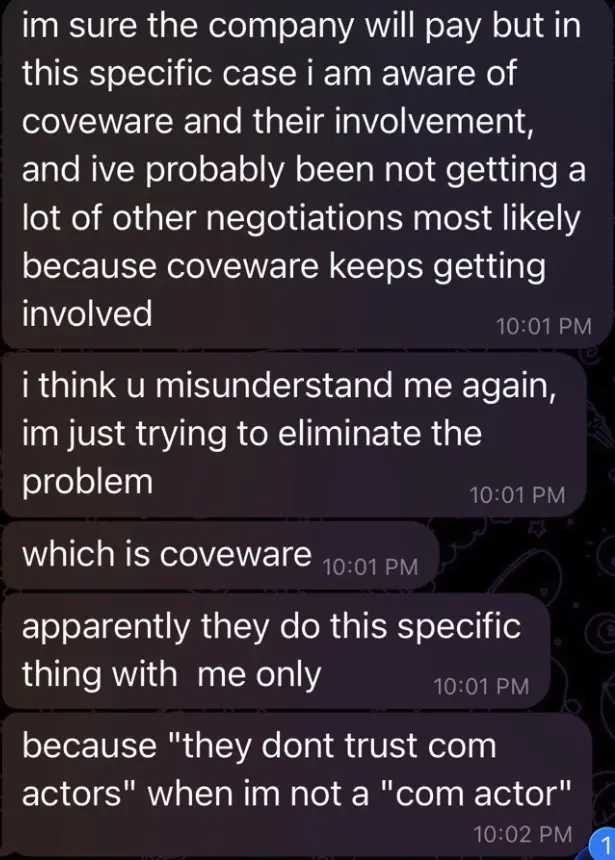
Investigative sources indicated that Van der Stap’s Signal message logs showed frequent conversations between the Dutch hacker, Dubrovsky, and at least one executive at a prominent U.S.-based consulting firm. Remarkably, these executives often possessed detailed information regarding new ShinyHunters victims before the victim organizations themselves were even aware they had been breached. Furthermore, federal investigators discovered that Dubrovsky knew ShinyHunters had exfiltrated highly sensitive data from FBI servers but never notified the bureau prior to the group’s public threats on social media to publish deeply personal personnel files.

SHINYWIRE
Federal investigators believe that at least one executive at the U.S.-based consulting firm played an active role in operating the now-defunct victim extortion portal known as "shinywire.com." Investigators and cybersecurity researchers have tracked the site’s lifecycle as a central nexus for the criminal enterprise.
The Shinywire domain was active from approximately May 3, 2026, until October 16, cataloging nearly 100 organizations compromised by ShinyHunters. Each listing on the platform urged targeted entities to engage directly with the cybercrime syndicate to negotiate payment terms. The web pages also displayed samples of stolen files, warning victims that their data would be publicly disseminated if ransom demands were ignored.
Cached internet scans revealed extortion listings targeting prominent corporations, such as Intuitive Surgical, an American medical technology firm that suffered a breach after an employee fell victim to a targeted phishing campaign. Under the group’s operational model, victim organizations that refused to negotiate within a strict seven-day window found their stolen data published on the primary ShinyHunters shaming blog, which is hosted on the Tor anonymity network.
The legal and professional fallout from the investigation has reverberated across the cybersecurity sector. In October, The Globe and Mail reported that Edward Dubrovsky had filed a lawsuit in Ontario earlier in the year against Daniel Tobok, the former chief executive of Cypfer, a Toronto-founded cybersecurity firm with international offices. Dubrovsky alleged that he had become collateral damage in a campaign by his former business partner to destroy him professionally following a corporate falling out in 2024. Tobok denied the allegations and filed a counterclaim, accusing Dubrovsky of misappropriating confidential information and competing unfairly through another entity called CyberSteward Inc.

GHOSTBYTE
The investigation has also shed light on historical ties within the ransomware ecosystem. According to interviews with several former colleagues, Daniel Tobok was known to ransomware purveyors years ago by the moniker "Ghostbyte." In 2018, a Canadian company compromised by Dharma—a prolific Russian-language ransomware affiliate program operating since 2016—sought assurances that the hackers would honor their word if a ransom was paid.
According to historical correspondence reviewed by investigators, a Dharma representative advised the victim to contact an IT company in Canada that routinely handled such arrangements, directing them to the email address [email protected]. While it remains unclear whether Tobok actively used that specific address, threat intelligence data from Constella Intelligence indicates that a primary email address frequently used by Tobok, [email protected], is associated with online accounts utilizing the username "ghostbyte," including a Snapchat profile. Constella data further linked the Dharma representative’s email address to a cryptocurrency wallet that processed substantial transactions totaling dozens of bitcoins.
In response to media inquiries, Cypfer issued a statement clarifying that its business operations do not involve facilitating ransomware payments and that the company had no prior knowledge of Dubrovsky’s arrest. The firm emphasized that Cypfer and CyberSteward are entirely separate entities with no shared leadership or employees, and noted that Cypfer was recently acquired by the Apros Group, a holding company led by former FBI special agent Jason Hogg.
CONFLICTING INTERESTS

The investigation highlights ongoing ethical and legal controversies surrounding the ransomware negotiation industry. While paying ransoms to retrieve encryption keys or secure promises of data deletion is not inherently illegal under U.S. federal law unless directed at sanctioned entities, the financial models underpinning negotiation firms have drawn intense scrutiny from law enforcement and industry veterans alike.
Many incident response firms operate on fee structures tied directly to the size of the ransom payment, creating an inherent conflict of interest. Critics argue that negotiators financially incentivized by a percentage of the payout lack motivation to drive down ransom amounts.
Industry leaders have increasingly called for transparency. Mark Camillo, chief executive of CyberAcuView, noted that practices where negotiators profit proportionally from transaction sizes undermine trust within the ecosystem. The Department of Justice has pursued multiple criminal cases against negotiation executives accused of defrauding clients by secretly paying hackers behind their backs or colluding with cybercriminals to maximize extortion payouts. As federal prosecutors continue to untangle the web of relationships connecting corporate consultants to groups like ShinyHunters, the case underscores systemic vulnerabilities within the global response to digital extortion.