The GeoServer open-source project has released a comprehensive security recap detailing a turbulent summer of 2026, highlighting a high-profile August zero-day vulnerability, previously published Common Vulnerabilities and Exposures (CVEs), a supply chain infrastructure advisory, and a newly updated security policy regarding AI-assisted vulnerability reports. Administrators responsible for managing GeoServer instances are being strongly advised to apply the latest security updates immediately by upgrading to GeoServer version 3.0.1, GeoServer version 2.28.5, or GeoServer version 2.27.6.
Throughout the lifecycle of the project, the GeoServer development and security teams have maintained a strict coordinated vulnerability disclosure policy. Under this framework, security flaws are thoroughly investigated and fixed across both stable and maintenance releases prior to any public CVE details being published. The primary objective of this coordinated approach is to ensure that system administrators and organizations around the world have an adequate opportunity to apply necessary updates to their production environments before malicious actors can weaponize the underlying flaws.
The challenges of modern vulnerability disclosure were vividly demonstrated in August 2026, when GeoServer encountered a severe zero-day vulnerability. This situation involved an active exploit operating in the wild with no official fix yet deployed to the general public, although the underlying problem had already been privately reported by several independent security researchers. A fix had been actively scheduled and prepared for inclusion in the forthcoming GeoServer 3.0.1 release.
However, the zero-day crisis escalated rapidly when an unrelated third party—completely unconnected to either the core project team or the researchers who originally discovered the flaw—publicly disclosed the vulnerability details on social media. The consequences of this unauthorized disclosure were immediate and severe. Automated vulnerability scans and targeted exploit attempts against unpatched GeoServer instances were detected within hours of the initial social media post.
The extraordinary speed at which attackers mobilized led to widespread industry news coverage and triggered an urgent, high-priority call to action across official user forums. Project leadership formally extended their gratitude to reporter Ravie Lakshmanan for first notifying the Open Source Geospatial Foundation regarding the active targeting of the vulnerability. This intense operational experience heavily reaffirmed the critical importance of adhering strictly to coordinated vulnerability disclosure policies and underscored why prompt action from administrators is vital whenever new software releases are made available.
In addition to the August zero-day emergency, the project recap outlined security activities from earlier in the summer. A series of CVEs were officially published on June 11, 2026, coinciding directly with the major feature release of GeoServer 3.0.0. These historical disclosures required targeted maintenance patches across multiple active branches, reinforcing the necessity for regular software lifecycle management among enterprise users who rely on geospatial data infrastructure.
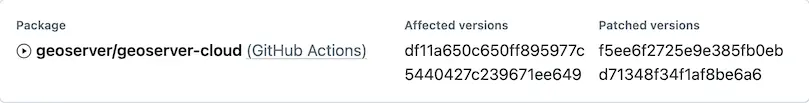
Furthermore, the summer months brought the project’s first encounter with a non-release infrastructure security event. A supply chain advisory was issued, carrying the potential to affect the integrity of downloaded software components. Because this advisory specifically targeted the geoserver/geoserver-cloud GitHub Actions environment rather than a formal software release of GeoServer itself, it did not qualify for a traditional CVE number.
Project maintainers emphasized strongly that no official GeoServer software releases were compromised or affected by this supply chain event. Standard GeoServer releases continue to be built exclusively using a dedicated Jenkins build server that publishes verified artifacts to both SourceForge and the official Open Source Geospatial Foundation infrastructure. Nevertheless, managing this infrastructure advisory highlighted the evolving threat landscape surrounding modern software development pipelines and third-party continuous integration workflows.
Another notable development during the summer of 2026 was the management of an increasing wave of automated, AI-assisted vulnerability reports. Much like other prominent open-source software projects, the GeoServer security team has experienced a significant influx of vulnerability submissions generated with the assistance of artificial intelligence tools. To address this phenomenon constructively, the project has established a general AI policy and updated its official security policy. These framework updates acknowledge the realities of AI-generated tooling and provide clear guidance for researchers utilizing these platforms.
Reviewing AI-assisted reports presents unique operational hurdles for maintainers. These submissions are frequently characterized by extreme verbosity, requiring substantial time and effort from security volunteers to review, validate, determine uniqueness, and filter out false positives or duplicates. The project has noted that having reporters on hand to clarify complex or lengthy AI-generated claims is deeply appreciated. Furthermore, contributors who are positioned to independently test, verify, and assist in validating proposed fixes provide invaluable support to the overextended geoserver-security team.
To sustain the ongoing security and maintenance of the platform, the project has actively encouraged organizations whose core operations depend on GeoServer to consider financial sponsorship or direct staff participation within the geoserver-security working group. Discussions are also underway to establish formal project membership pathways for public institutions and governmental entities that frequently face bureaucratic or legal restrictions regarding commercial sponsorship and direct open-source project participation.
Addressing questions regarding upgrade frequency, project maintainers reiterated that GeoServer operates on a time-boxed release cycle. This cycle maintains both stable and maintenance release branches over the course of a calendar year. Organizations are strongly advised to upgrade their deployments to a fully supported release at least once every twelve months to ensure continuous access to critical security patches and bug fixes. Comprehensive documentation and guidance for performing these upgrades smoothly are maintained within the official GeoServer User Guide.
For security researchers and system administrators seeking to report newly discovered vulnerabilities or coordinate safe disclosures, the project maintains clear instructions within its official security policy repository. Submissions should be routed privately through GitHub security advisories to ensure adherence to responsible disclosure guidelines and protect global users from premature exposure.