The GeoServer project team has published a comprehensive security recap detailing a turbulent summer of 2026, which included managing a high-profile zero-day vulnerability, addressing previously published Common Vulnerabilities and Exposures (CVEs), navigating a supply chain advisory, and introducing updated policies to handle a growing wave of AI-assisted vulnerability reports.
Administrators and organizations responsible for maintaining GeoServer instances have been urged to apply the latest security patches immediately. The immediate action item for all system operators is to update their software to GeoServer version 3.0.1, version 2.28.5, or version 2.27.6, depending on which stable or maintenance branch their infrastructure currently utilizes.
Throughout its operational history, the GeoServer project has strictly adhered to a coordinated vulnerability disclosure policy. Under this framework, security flaws are thoroughly investigated, and patches are developed and tested for both stable and maintenance releases well before any CVE details are made public. The fundamental objective of this approach is to provide the entire user community with an adequate window of opportunity to update their systems and secure their environments prior to public disclosure, thereby minimizing the risk of active exploitation.
The security landscape shifted dramatically in August when GeoServer encountered a critical zero-day vulnerability, defined as an exploit actively observed in the wild without a pre-existing official fix available to the general public. The underlying flaw had already been reported privately to the project through responsible channels by several independent researchers, and a formal patch had already been scheduled for inclusion in the upcoming GeoServer 3.0.1 release.
However, the containment strategy was disrupted when an unrelated third party—completely unconnected to either the core project team or the researchers who originally discovered the issue—publicly disclosed the vulnerability details on social media. The consequences were immediate and severe. Within hours of the public social media post, automated security scans and malicious probes targeting this specific vulnerability were detected across the internet.
The velocity of this malicious response underscored the precarious nature of modern software security and generated significant industry news coverage, alongside urgent operational warnings broadcast across the official GeoServer user forums. Project leadership expressed deep gratitude to reporter Ravie Lakshmanan for initially notifying them of the circulating reports via the Open Source Geospatial Foundation. This intense incident served as a stark reaffirmation of why strict adherence to coordinated vulnerability disclosure policies remains paramount, and why prompt patching by system administrators is critical the moment new releases become available.
Before the August zero-day incident, the project had already addressed several other security challenges earlier in the season. On June 11, 2026, concurrent with the major GeoServer 3.0.0 release, a series of previously published CVEs were officially disclosed and resolved across supported maintenance branches, including updates for GeoServer versions 2.27.3, 2.26.4, and 2.27.0. These routine releases form the backbone of the project’s strategy to continuously harden the codebase against newly discovered attack vectors.
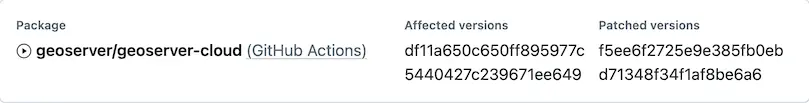
In addition to traditional code vulnerabilities, the project recently confronted its first-ever infrastructure supply chain advisory. Supply chain advisories carry the potential to undermine the integrity of software artifacts downloaded by end users. In this instance, the advisory was specifically categorized under the label "geoserver/geoserver-cloud (GitHub Actions)" because it pertained to the cloud build and automation pipeline rather than a direct source code defect in a software release, meaning it did not qualify for a traditional CVE number.
Project maintainers emphasized a crucial distinction for users: no official GeoServer releases were compromised or affected by this supply chain event. Standard GeoServer releases are compiled and distributed using an independent Jenkins build server that publishes verified artifacts directly to SourceForge and official Open Source Geospatial Foundation infrastructure, providing a secure barrier between development automation tools and final user downloads.
Another major administrative challenge highlighted in the summer review is the modern phenomenon of AI-assisted security reporting. Like many open-source software projects globally, GeoServer has experienced a substantial influx of vulnerability reports generated with the assistance of artificial intelligence tools. While these tools can theoretically help identify potential code anomalies, they frequently produce large volumes of highly verbose, speculative, or duplicate submissions that require intensive manual review by maintainers.
To manage this operational shift, the project has established a general artificial intelligence policy and updated its core GitHub security policy. These documents explicitly acknowledge the utilization of AI tools in security research and provide clear guidance for researchers. Maintainers noted that when dealing with verbose AI-generated reports, researchers who are readily available to clarify ambiguous details, test proposed patches, and help verify fixes provide invaluable assistance to the overburdened security team.
Sustaining the security and ongoing development of GeoServer requires active collaboration between the core team and the organizations that rely on the software for critical geospatial infrastructure. Project leadership continues to encourage organizations dependent on GeoServer to consider corporate sponsorship or to permit their internal engineering staff to participate directly in the dedicated security working groups. Additionally, the project is actively working to establish formal project membership pathways for public institutions and government agencies that frequently face administrative or legal restrictions regarding corporate sponsorship and direct financial contributions.
To maintain robust security postures, the GeoServer project operates under a predictable time-boxed release cycle, systematically maintaining stable and maintenance branches over the course of each calendar year. System administrators are strongly advised to upgrade their operational deployments to a supported release at least once every twelve months to ensure they continue receiving critical security patches and maintenance bug fixes, referencing the official installation and upgrade guides provided in the project user documentation for detailed technical instructions.