The GeoServer project has issued a comprehensive security recap detailing a turbulent summer of 2026, which featured a high-profile zero-day exploit, multiple Common Vulnerabilities and Exposures (CVEs), a supply chain advisory, and an influx of automated vulnerability reports. Project maintainers are strongly urging administrators to update their systems immediately to protect against active threats.
Administrators responsible for managing a GeoServer instance are being directed to apply the latest security patches without delay. The critical patches are available in GeoServer version 3.0.1, version 2.28.5, and version 2.27.6. These releases contain vital fixes meant to secure deployments against vulnerabilities identified over the past several months.
Throughout its operational history, the GeoServer project has strictly adhered to a coordinated vulnerability disclosure policy. Under this protocol, vulnerabilities are thoroughly investigated and fixed across both stable and maintenance releases before any CVE details are made public. The underlying philosophy of this approach is to provide all users and organizations with a fair opportunity to apply updates and secure their environments prior to public disclosure, thereby minimizing the window of opportunity for malicious actors.
The August Zero-Day Incident
The security landscape shifted dramatically in August when GeoServer encountered a zero-day vulnerability, defined as an actively exploited security flaw in the wild for which no official patch had yet been published. Prior to the public leak, the underlying issue had already been reported privately to project maintainers by several independent researchers. A permanent fix had already been scheduled for inclusion in the forthcoming GeoServer 3.0.1 release.
However, the situation escalated rapidly when an unrelated third party—completely unconnected to either the core project or the researchers who originally discovered the flaw—publicly disclosed the vulnerability on social media. The fallout was immediate. Automated scans searching for vulnerable instances were detected within mere hours of the public social media post going live, highlighting the alarming speed with which modern threat actors operationalize public intelligence.
The rapid response required an emergency mobilization by the project leadership, generating widespread media coverage and triggering an urgent call to action across user forums and official communication channels. Project leadership formally acknowledged the assistance of reporter Ravie Lakshmanan, who first notified project leadership through the Open Source Geospatial Foundation, helping to spark the accelerated defensive rollout.
This stressful episode starkly reaffirmed the critical importance of adhering strictly to coordinated vulnerability disclosure policies. It also underscored why administrators must heed update notices immediately upon release, as the gap between public disclosure and active exploitation can be measured in hours rather than weeks.
Previously Published CVEs and Release Cycles
The summer security recap also reviewed vulnerabilities published earlier in the season. On June 11, 2026, a series of CVEs were disclosed alongside the major release of GeoServer 3.0.0. These earlier security disclosures required targeted updates across multiple active branches, specifically impacting legacy and maintenance lines such as GeoServer 2.27.3, 2.26.4, and the 2.27.0 release train.
Managing multiple active versions is a core part of the GeoServer maintenance strategy. The project operates on a structured, time-boxed release cycle that spans a full calendar year, maintaining distinct "stable" and "maintenance" release branches concurrently.
Because of this rapid development and support lifecycle, project maintainers strongly recommend that organizations upgrade their deployments at least once a year to ensure they continue receiving critical security patches and maintenance updates. Upgrading requires following established procedures outlined in the official user guide to ensure a smooth transition between versions.
Supply Chain Security and Infrastructure Advisories
In addition to software code vulnerabilities, the GeoServer project faced a unique challenge over the summer involving its first-ever supply chain infrastructure advisory. This particular advisory had the potential to impact the integrity of software downloads, drawing immediate attention from the core development team.
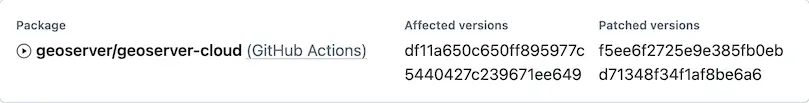
Because the incident did not correspond directly to a traditional software release of GeoServer, it did not qualify for a standard CVE tracking number. Instead, project maintainers formally categorized the advisory under "geoserver/geoserver-cloud (GitHub Actions)" to reflect its precise scope within the continuous integration pipeline.
Crucially, project leadership confirmed that no official GeoServer releases were compromised or affected by the supply chain incident. Standard GeoServer releases are compiled and published using a dedicated Jenkins build server that distributes trusted artifacts to both SourceForge and official Open Source Geospatial Foundation (OSGeo) infrastructure. The clear separation between cloud automation pipelines and core release infrastructure helped prevent a broader security crisis.
AI-Assisted Vulnerability Reports and Policy Updates
Like many other open-source software projects in recent years, the GeoServer team has experienced a noticeable surge in vulnerability reports generated with the assistance of artificial intelligence tools. These AI-generated submissions often arrive in high volumes and tend to be exceptionally verbose, placing a heavy analytical burden on the core maintainers.
Reviewing these automated submissions requires significant time and technical effort, particularly when trying to determine if a report is valid, whether it represents a novel issue, or if it is merely a duplicate of an existing ticket. To address this evolving trend constructively, the project has established a dedicated general AI policy and updated its core security policy. These framework updates are designed to acknowledge the reality of automated tooling, provide clear guidance to researchers, and streamline the triage process.
Project leaders note that when security researchers utilize AI tools to scan and report potential issues, being readily available on hand to clarify technical details is deeply appreciated. Furthermore, contributors who are positioned to test and independently verify proposed fixes provide invaluable assistance to the overburdened security team.
Community Support and Engagement
Securing a widely deployed open-source geospatial platform requires substantial resources, and the GeoServer project continues to rely heavily on community collaboration to maintain its security posture. Organizations and enterprises whose critical infrastructure depends on GeoServer are encouraged to explore formal sponsorship options or allow their technical staff to participate directly in the dedicated geoserver-security mailing list and working groups.
To accommodate public institutions and government bodies that often face strict institutional or legal restrictions regarding traditional commercial sponsorship and direct financial participation, the project is actively working to establish a formalized project membership framework under GSIP-243. This initiative aims to bridge the gap and enable broader institutional collaboration.
For security researchers and developers seeking to report newly discovered vulnerabilities responsibly, the project maintains clear instructions within its official security policy. Developers and administrators can coordinate private disclosures securely utilizing GitHub security advisories, ensuring that bugs can be resolved and patches tested before malicious actors can weaponize them.