The GeoServer project team has released a comprehensive summary of its security advisories and developments from the summer of 2026, highlighting a critical period marked by a high-profile zero-day vulnerability, multiple Common Vulnerabilities and Exposures (CVEs), a supply chain advisory involving GitHub Actions, and an influx of automated vulnerability reports.
For administrators and organizations responsible for maintaining GeoServer instances, the immediate imperative following these summer developments is clear. The project strongly advises users to update their systems to the newly patched versions: GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6.
Throughout its history, the GeoServer project has maintained a strict adherence to a coordinated vulnerability disclosure policy. Under this framework, security flaws are comprehensively addressed and fixed across both stable and maintenance release branches before any technical details or CVE identifiers are made public. The underlying philosophy of this approach is to provide system administrators, enterprises, and public institutions with adequate lead time to apply necessary security updates before malicious actors can weaponize the information.
The August Zero-Day Incident
The summer security landscape was severely tested in August when GeoServer confronted a critical zero-day vulnerability—a flaw that was actively being exploited in the wild before an official patch could be widely deployed. Prior to the public breach, the security issue had already been identified and reported privately to the project by several independent security researchers. A remediation patch had already been scheduled for inclusion in the forthcoming GeoServer 3.0.1 release.
However, the carefully managed timeline was disrupted when an unrelated third party publicly disclosed the vulnerability on social media. The fallout was swift and immediate. Automated scanning tools and threat actors began probing for the vulnerability within hours of the social media post going live.
The rapid escalation generated significant industry attention, including coverage by prominent cybersecurity news outlets like The Hacker News, alongside urgent advisory alerts posted across the official OSGeo user forums. Project leadership formally acknowledged the swift reporting efforts of security researcher Ravie Lakshmanan, who first notified project leadership through the Open Source Geospatial Foundation.
The sudden emergence of the zero-day exploit powerfully reinforced the critical necessity of adhering to coordinated vulnerability disclosure practices. It also served as a stark reminder to the broader user community regarding the importance of applying software updates immediately upon their release.
Previously Published CVEs and Release Cycles
The summer security updates also encompassed a series of vulnerabilities published earlier in the season. On June 11, 2026, alongside the major release of GeoServer 3.0.0, developers rolled out targeted patches addressing previously identified CVEs. These included updates for maintenance branches such as GeoServer 2.27.3, 226.4, and the foundational GeoServer 2.27.0 release.
Managing these vulnerabilities is part of an ongoing operational rhythm for the project. GeoServer operates under a structured, time-boxed release cycle that spans a full calendar year, consistently maintaining both stable and active maintenance release branches. Because software security is an evolving discipline, project maintainers urge organizations to upgrade their instances to a supported release at least once every twelve months to ensure continuous coverage against newly discovered threats and vulnerabilities. Upgrading guidelines and technical documentation are maintained within the official GeoServer User Guide to assist administrators through the transition processes.
Navigating a Supply Chain Advisory
In addition to traditional software vulnerabilities, the GeoServer project encountered a different category of security challenge over the summer: its very first infrastructure supply chain advisory.
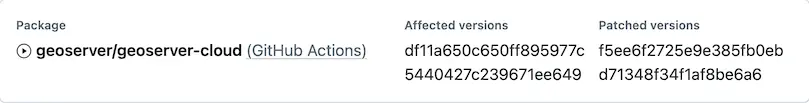
Supply chain advisories carry the inherent potential to undermine the integrity of downloaded software packages, making them a major concern for enterprise architectures. However, project maintainers clarified that the advisory was classified specifically under "geoserver/geoserver-cloud (GitHub Actions)" because it pertained to cloud-based continuous integration infrastructure rather than an official source code release of GeoServer itself. Consequently, the incident did not qualify for a traditional CVE tracking number.
Crucially, the project confirmed that no official GeoServer releases were compromised or affected by the infrastructure incident. Standard GeoServer production releases continue to be compiled using an isolated Jenkins build server, which subsequently publishes validated software artifacts directly to SourceForge and the core OSGeo infrastructure repositories.
Managing AI-Assisted Vulnerability Reports
Like many open-source software projects across the global technology ecosystem, the GeoServer security team has experienced a sharp surge in vulnerability reports generated with the assistance of artificial intelligence tools.
While automated and AI-driven security analysis can occasionally assist in surfacing potential code anomalies, these submissions often present unique administrative challenges. AI-generated reports tend to be exceptionally verbose, frequently introduce duplicate submissions, and require significant manual effort from core developers to review, validate, and test.
In response to this growing trend, the project has established a formal AI Policy and updated its comprehensive GitHub Security Policy. These policy updates explicitly acknowledge the influx of AI-generated content and provide clear guidelines for contributors. The project emphasizes that human involvement—particularly security researchers who are willing to remain on hand to clarify complex reports, test potential fixes, and help verify patches—remains invaluable in lightening the load on the dedicated geoserver-security team.
How the Community Can Support GeoServer Security
Maintaining robust security for a widely deployed geospatial platform requires sustained effort and community collaboration. Project leadership has outlined several pathways for organizations and individuals looking to support the ecosystem.
Enterprises and commercial entities that rely heavily on GeoServer for critical operations are encouraged to financially sponsor the project or enable their internal technical staff to participate directly in the geoserver-security working group and mailing lists. Furthermore, to accommodate public institutions and government agencies that often face strict institutional or legal barriers regarding direct corporate sponsorship, the project is actively working to establish formalized project membership pathways under GSIP-243.
For security researchers, developers, and system administrators seeking to report newly discovered vulnerabilities, the project maintains strict confidential reporting guidelines. Vulnerabilities should never be disclosed publicly before a coordinated patch is available; instead, reports must be submitted privately through the official GitHub security advisories interface detailed in the project’s core security policy.