The open-source geospatial community has faced a demanding period of security maintenance following a series of advisories published over the summer of 2026. Project maintainers have released critical software patches, addressed a high-profile zero-day vulnerability, navigated a supply chain incident, and updated institutional security policies to adapt to a rising tide of automated, AI-generated vulnerability reports.
For organizations, municipalities, and enterprises responsible for managing mapping infrastructure, the immediate operational directive is clear: administrators must update their deployments to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6 immediately. These releases contain crucial fixes designed to secure instances against active exploits and previously cataloged common vulnerabilities and exposures.
The GeoServer project traditionally operates under a strict coordinated vulnerability disclosure policy. Under this framework, security flaws are identified, analyzed, and patched across both stable and maintenance release lines before any technical details or CVE identifiers are made public. This disciplined approach is intentionally engineered to give system administrators a safe window of time to apply updates, minimizing the risk of widespread exploitation across global infrastructure. However, maintaining this protective barrier requires strict adherence from all participants in the ecosystem.
The August Zero-Day Event
The limits of coordinated disclosure were severely tested in August when GeoServer confronted an active zero-day vulnerability—an operational flaw being actively targeted in the real world with no official fix yet deployed to the general public. Prior to the public breach, the underlying problem had already been responsibly reported through private channels by several independent researchers. Project developers had recognized the severity of the flaw and had scheduled a comprehensive fix to be bundled into the upcoming GeoServer 3.0.1 release.
Unfortunately, the timeline was disrupted when an unrelated third party—completely unconnected to the project leadership or the original research team—publicly disclosed the vulnerability on social media. The consequences were immediate and severe. Automated threat intelligence and network sensors detected malicious scans probing for the vulnerability within hours of the public social media post.
The velocity of this malicious response triggered widespread concern, prompting urgent news coverage and an emergency broadcast across the official GeoServer user forums. Project leadership expressed gratitude to security researcher Ravie Lakshmanan, who first notified the project leadership via the Open Source Geospatial Foundation, helping trigger the rapid mobilization of developer resources.
This dramatic incident underscored the vulnerability of open-source projects to premature public disclosures. It reaffirmed the vital importance of the coordinated vulnerability disclosure policy and reinforced the necessity for the user community to apply patches the moment they are made available.
Previously Published CVEs and Release Management
The summer security review also encompassed a series of Common Vulnerabilities and Exposures published earlier in the season. On June 11, 2026, coinciding with the major release of GeoServer 3.0.0, project maintainers rolled out patches for several earlier versions, including updates for GeoServer 2.27.3, GeoServer 2.26.4, and GeoServer 2.27.0.
Managing vulnerabilities across multiple active release branches requires considerable coordination. GeoServer follows a structured, time-boxed release cycle that maintains both stable and maintenance branches over the course of a year. Because software security is an ongoing operational commitment, the project strongly advises organizations to upgrade their instances to a supported release at least once every twelve months. Regular upgrades ensure that systems continue to receive vital security backports and stability enhancements. Comprehensive upgrading instructions are documented in the user guide to assist system administrators through the migration process.
Supply Chain Advisory and Infrastructure Security
In addition to direct software vulnerabilities, the project faced its first encounter with a supply chain advisory during the summer review cycle. Supply chain advisories carry the potential to undermine the inherent integrity of downloaded software artifacts, making them a critical concern for enterprise risk management.
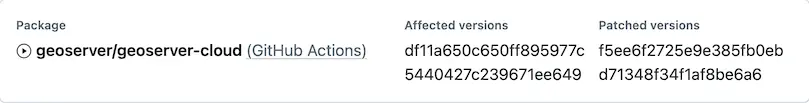
Because this specific supply chain advisory affected GitHub Actions within the geoserver/geoserver-cloud repository rather than an official core release of GeoServer, it did not map directly to a standard software release and therefore did not qualify for a traditional CVE number. Project leadership emphasized a critical distinction for users: no official GeoServer software releases were affected by this advisory. Authentic GeoServer releases are built securely using a dedicated Jenkins build server that publishes verified artifacts directly to SourceForge and official Open Source Geospatial Foundation infrastructure.
AI-Assisted Vulnerability Reports and Policy Updates
Like many prominent open-source software projects, GeoServer has experienced a significant surge in vulnerability reports generated with the assistance of artificial intelligence. While automated tools can sometimes aid in code analysis, AI-generated submissions frequently present unique operational challenges for maintainers. These reports are often extremely verbose, repetitive, or inaccurate, requiring substantial human effort to review, validate, and deduplicate.
To manage this influx effectively, the project has established a dedicated general AI policy and updated its core security policy on GitHub. These documents formally acknowledge the reality of AI-assisted security submissions and provide clear guidance for researchers utilizing automated tools.
Project maintainers noted that when dealing with verbose AI-generated submissions, having researchers on hand to clarify ambiguities, test assumptions, and verify proposed fixes is immensely helpful. Community members who can actively assist the security team by reviewing reports, testing patches, and reducing noise play an invaluable role in sustaining the project’s health.
Community Participation and Reporting
Securing a widely deployed open-source project like GeoServer is a collaborative responsibility that extends far beyond the core development team. Organizations whose operational continuity depends heavily on GeoServer are encouraged to support the project financially through official sponsorships or by permitting their technical staff to participate directly in the geoserver-security working groups. Furthermore, the project is actively working to establish formal project membership pathways for public institutions and government agencies that frequently face administrative or legal restrictions regarding traditional commercial sponsorships and direct participation.
For security researchers and system administrators seeking to report a newly discovered vulnerability, the project maintains clear protocols. All suspected security flaws should be reported privately through responsible disclosure channels utilizing GitHub security advisories, ensuring that maintainers have adequate time to develop, test, and distribute secure patches before any public disclosure occurs.