The GeoServer project has released a comprehensive security recap detailing a tumultuous summer of 2026 that tested the open-source mapping platform’s defenses, response mechanisms, and community policies. Highlighting the period are critical updates, an August zero-day vulnerability that triggered active exploitation in the wild, a supply chain advisory involving GitHub Actions, and the introduction of updated policies to manage an influx of AI-generated vulnerability reports.
Administrators responsible for running GeoServer instances are being urged to apply the latest security patches immediately. The core recommendation across the board is for users to update their deployments to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6 depending on their active branch. These patches contain vital fixes meant to seal the gaps exposed over the summer months.
The GeoServer development team strictly adheres to a coordinated vulnerability disclosure policy. Under this framework, security flaws are patched across both stable and maintenance release lines prior to the public publication of any Common Vulnerabilities and Exposures (CVE) details. The foundational goal of this methodology is to give every organization and system administrator sufficient opportunity to update their software before malicious actors gain access to technical exploitation details. However, maintaining this protective window proved challenging during the recent warm-weather months due to external pressures and premature disclosures.
August Zero-Day Vulnerability Sparks Rapid Response
The most alarming incident of the season occurred in August, when GeoServer was struck by a zero-day vulnerability—an active exploit in the wild with no official fix ready at the exact moment of public exposure. Prior to the leak, the underlying security flaw had already been privately reported to project maintainers by several independent researchers, and a formal fix had appropriately been scheduled for inclusion in the upcoming GeoServer 3.0.1 release.
Unfortunately, the secure timeline was disrupted when an unrelated third party, completely unconnected to either the project or the initial reporting researchers, chose to disclose the vulnerability publicly on social media. The fallout was swift and measurable. Automated scans designed to detect and exploit this specific vulnerability were observed by network monitors within mere hours of the social media post going live.
The speed of this hostile response was remarkable, driving immediate mainstream news coverage and forcing the project leadership to issue urgent calls to update across user forums and communication channels. Project leadership expressed gratitude to security researcher Ravie Lakshmanan, who first notified project leadership via the Open Source Geospatial Foundation, helping galvanize the swift engineering response.
This high-pressure experience vividly reaffirmed the critical importance of strictly following coordinated vulnerability disclosure policies. It also underscored why the project continually urges every user and organization to apply updates immediately upon release rather than delaying maintenance cycles.
Previously Published CVEs and Release Cycles
The summer security updates built upon earlier administrative measures taken earlier in the season. On June 11, 2026, alongside the major rollout of the GeoServer 3.0.0 release, a series of CVEs were published to address foundational security weaknesses found within older lines. These updates spanned targeted maintenance releases like GeoServer 2.27.3 and 2.26.4, as well as broader feature updates such as GeoServer 2.27.0.
Navigating these security updates requires understanding how the project manages its software lifecycle. GeoServer operates on a time-boxed release cycle, systematically maintaining both "stable" and "maintenance" release branches over the course of any given year. Because vulnerabilities are discovered continuously across aging codebases, project maintainers strongly advise organizations to upgrade to a supported release at least once every twelve months to ensure continuous coverage and access to critical security patches. Comprehensive instructions for handling these transitions are maintained within the official user guide documentation for upgrading existing versions.
Supply Chain Advisory and Infrastructure Integrity
In addition to direct application-level code vulnerabilities, the GeoServer project faced a different kind of security test over the summer: its first-ever supply chain infrastructure advisory. Supply chain advisories carry the inherent potential to disrupt the integrity of software downloads by calling into question whether the binaries compiled and distributed to the public can be fully trusted.
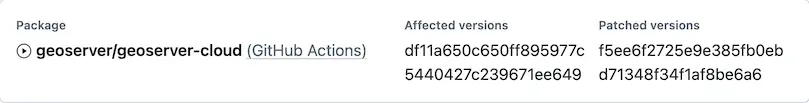
To handle this unique situation transparently, the project designated the advisory under the label "geoserver/geoserver-cloud (GitHub Actions)." Maintainers carefully clarified that this infrastructure event did not correspond with a standard release of the GeoServer software itself, and consequently, it did not qualify for a traditional CVE number.
Crucially, project leaders emphasized that no actual GeoServer software releases were affected by the cloud infrastructure incident. Standard GeoServer production releases continue to be built using a dedicated Jenkins build server that publishes final artifacts securely to both SourceForge and official OSGeo infrastructure, maintaining a strict firewall between cloud automation pipelines and core distribution channels.
Managing the Wave of AI-Assisted Vulnerability Reports
Like many other prominent open-source software projects in the modern ecosystem, the GeoServer maintainers are currently experiencing an unprecedented wave of vulnerability reports generated with the assistance of artificial intelligence. While AI tools can assist researchers in spotting anomalies, they frequently generate verbose, redundant, or speculative findings that require significant human effort to triage, verify, and deduplicate.
To adapt to this technological shift, the project has established a general AI Policy and updated its core Security Policy. These documents acknowledge the rising tide of automated submissions and provide clear guidance to contributors on how to submit meaningful reports. The project stresses that when working with AI-generated reports—which are often extremely long and complex—having the original reporters on hand to clarify ambiguities is deeply appreciated.
Reviewing these automated submissions, determining if they represent novel bugs or mere duplicates, and validating proposed patches consumes substantial volunteer and developer bandwidth. Consequently, community members who are positioned to test and verify security fixes as they are developed provide invaluable assistance to the overburdened geoserver-security team.
Community Involvement and How to Help
As the complexity of securing enterprise geospatial infrastructure grows, the GeoServer team continues to rely heavily on its global community for support. Organizations whose daily operations depend on the stability and security of GeoServer are encouraged to consider corporate sponsorship or to allow their internal engineering staff to participate directly in geoserver-security operations.
Furthermore, to accommodate public institutions and government agencies that often face strict bureaucratic or legal restrictions regarding direct commercial sponsorship and open-source participation, the project is actively working to establish formal project membership structures under GSIP-243.
For individuals and organizations needing to report a newly discovered security vulnerability, the process remains strictly confidential. Detailed instructions for reporting vulnerabilities privately using GitHub security advisories can be found directly within the project’s official security policy documentation on GitHub.