The GeoServer project has issued a comprehensive security recap covering a turbulent summer of 2026, highlighting a series of newly published Common Vulnerabilities and Exposures (CVEs), a notable supply chain advisory, and an unexpected zero-day exploit that forced the project’s maintainers to accelerate their patching schedule. Alongside these technical challenges, the project has also responded to the modern landscape of software security by updating its policies regarding AI-assisted vulnerability disclosures.
For administrators and organizations responsible for deploying and maintaining GeoServer instances, the immediate takeaway from the summer security cycle is clear: operators must update their software promptly. The project has released versions 3.0.1, 2.28.5, and 2.27.6 to address the critical flaws discovered over the past few months.
GeoServer traditionally adheres to a strict coordinated vulnerability disclosure policy. Under this framework, security flaws are investigated, validated, and patched across both stable and maintenance release lines before any CVE details or technical descriptions are made public. The fundamental goal of this coordinated approach is to provide system administrators and organizations with an adequate window of opportunity to apply security updates prior to malicious actors becoming aware of the underlying weaknesses. However, maintaining this protective buffer relies heavily on adherence to the disclosure timeline by all participating researchers and third parties.
The August Zero-Day Incident
The fragility of public coordination was put to the test in August 2026, when GeoServer encountered a zero-day vulnerability—an active exploit occurring in the wild with no official fix yet deployed to the general public. Prior to this public exposure, the underlying problem had already been reported privately through appropriate channels by several independent security researchers, and a formal fix had already been scheduled for inclusion in the upcoming GeoServer 3.0.1 release.
The zero-day crisis materialized because an unrelated third party, operating completely outside the project and unconnected to the researchers who initially flagged the issue, publicly disclosed the vulnerability details on social media. The consequences of this premature disclosure were immediate and severe. Automated scanning activity and active exploitation attempts targeting the vulnerability were detected by security monitors within mere hours of the social media post going live.
The speed with which malicious actors mobilized following the leak was remarkable, prompting widespread news coverage and an urgent, high-priority call for users to update their installations via the official user forum. Project leadership expressed gratitude to reporter Ravie Lakshmanan for first notifying the Open Source Geospatial Foundation regarding the active targeting of the flaw. The rapid rollout of GeoServer 3.0.1, alongside updated maintenance versions 2.28.5 and 2.27.6, mitigated the immediate threat, but the incident powerfully reaffirmed the critical importance of respecting coordinated vulnerability disclosure policies and ensuring rapid deployment of patches by the user community.
Previously Published CVEs and Release Cycles
The summer security updates built upon earlier vulnerability disclosures made earlier in the year. On June 11, 2026, coinciding with the major rollout of the GeoServer 3.0.0 release, a separate batch of CVEs was published to address vulnerabilities discovered in preceding versions. These disclosures necessitated swift updates across the software’s active maintenance branches, including versions 2.27.3, 2.26.4, and the foundational 2.27.0 release.
Managing these multifaceted security cycles requires significant coordination between core developers and the broader open-source community. GeoServer operates under a time-boxed release cycle that spans a full calendar year, maintaining both designated stable and regular maintenance releases to ensure backward compatibility and reliable upgrade paths for enterprise environments.
Project maintainers strongly advise organizations to upgrade their GeoServer instances to a supported release at least once every year to ensure they continue receiving vital security backports and bug fixes. Upgrading too infrequently leaves systems exposed to well-documented vulnerabilities for which public exploits may already exist. Comprehensive guidance for managing these upgrades is maintained within the official user guide documentation.
Supply Chain Advisory and Infrastructure Integrity
In addition to direct software vulnerabilities, the GeoServer project navigated its first-ever infrastructure supply chain advisory during this period. Because supply chain advisories directly concern the integrity of downloaded software artifacts, they require careful handling and transparent communication to maintain user trust.
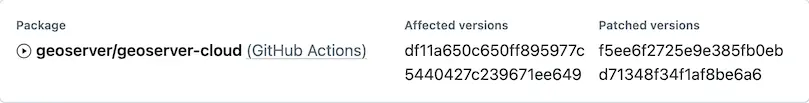
The advisory in question was uniquely categorized under GitHub Actions for the geoserver/geoserver-cloud repository rather than corresponding to a traditional official release of GeoServer itself. Consequently, because it did not stem from a standard software release artifact, it did not qualify for a traditional CVE number.
Crucially, project leadership emphasized that no official GeoServer releases were compromised or affected by this supply chain event. Standard GeoServer releases are compiled and published using an isolated Jenkins build server, which securely distributes official artifacts to both SourceForge and the core OSGeo infrastructure, maintaining a strict separation from cloud-based auxiliary tooling.
Managing AI-Assisted Vulnerability Reports
Like many other prominent open-source software projects, the GeoServer team has recently experienced a significant influx of vulnerability reports generated with the assistance of artificial intelligence tools. While automated and AI-driven analysis can sometimes assist in identifying edge cases, these reports often present unique administrative challenges for maintainers.
AI-generated reports are frequently very verbose, sometimes lacking critical context, and occasionally resulting in a high volume of duplicate submissions. Reviewing these extensive submissions, determining their validity, and filtering out noise consumes considerable time and effort from the volunteer-driven security team. Furthermore, verifying fixes and testing patches against AI-submitted claims requires specialized expertise.
To address this modern trend, the project has established a dedicated AI policy and updated its core security policy on GitHub. These policy updates explicitly acknowledge the use of AI tools in security research and provide clear guidelines for researchers submitting findings. Maintainers have noted that when researchers using AI tools are readily available to clarify their submissions, test proposed fixes, and assist with verification, the burden on the security team is substantially alleviated.
Sustaining the Project and How to Help
Securing a widely deployed geospatial server platform requires continuous effort, financial backing, and active community participation. The GeoServer maintainers rely on the organizations and enterprises that depend on their software to help sustain ongoing development and security operations.
Organizations utilizing GeoServer in production environments are encouraged to consider financial sponsorship through the project’s official channels or to permit their internal engineering staff to participate directly in the geoserver-security working groups and mailing lists. Additionally, the project is actively working to establish formal project membership structures for public institutions and government agencies that may face legal or administrative restrictions preventing them from traditional corporate sponsorship or open-source participation.
For individuals or security researchers who discover genuine security flaws, the project maintains a transparent and secure reporting procedure. Security vulnerabilities should always be reported privately through GitHub security advisories as outlined in the repository’s official security policy, ensuring that issues can be properly addressed, patched, and coordinated before any public disclosure takes place.