The maintainers of GeoServer, a widely used open-source geospatial data server, have published a comprehensive security recap detailing a turbulent summer of 2026. The update covers newly discovered Common Vulnerabilities and Exposures (CVEs), a notable supply chain advisory affecting the project’s cloud infrastructure, and a formal policy update addressing the rising tide of AI-assisted vulnerability disclosures. Most crucially, project administrators are urging all system administrators and organizations responsible for GeoServer deployments to apply urgent patches immediately by upgrading to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6.
The open-source project strictly adheres to a coordinated vulnerability disclosure policy. Under this framework, security flaws are investigated, patches are developed, and fixes are successfully integrated into both stable and maintenance releases prior to any public disclosure of CVE details. The fundamental goal of this coordinated approach is to provide the global user base with an adequate window of opportunity to update their systems and secure their infrastructure before malicious actors become aware of the specific technical vectors involved. However, maintaining this balance became exceptionally challenging during the late summer months following an unexpected zero-day incident.
August Zero-Day Incident Highlights Risks of Premature Disclosure
In August, GeoServer faced a high-pressure zero-day vulnerability situation, referring to an actively exploited security flaw in the wild for which no official public fix had yet been deployed across all user environments. The underlying problem had already been responsibly reported in private by several independent researchers, and developers had scheduled a proper fix to be bundled into the upcoming GeoServer 3.0.1 release.
The security crisis escalated unexpectedly when a third-party entity—completely unconnected to either the core project team or the original independent researchers who discovered the flaw—publicly disclosed the vulnerability on social media. The fallout was swift and severe. Automated scans and active attempts to exploit the newly publicized vulnerability were detected across the internet within mere hours of the social media post going live.
The extraordinary speed at which attackers mobilized prompted immediate news coverage across cybersecurity outlets and triggered an urgent call to action on the official GeoServer user forums maintained by the Open Source Geospatial Foundation. Project leadership expressed gratitude to reporter Ravie Lakshmanan for first notifying the foundation of the active exploitation. This dramatic episode served as a stark reaffirmation of why coordinated vulnerability disclosure policies are vital to the ecosystem, and why administrators must apply new releases rapidly as soon as they become available to the public.
Previously Published CVEs and Release Cycles
The summer security updates also encompass several vulnerabilities published earlier in the season. On June 11, 2026, alongside the major release of GeoServer 3.0.0, a series of CVEs were formally disclosed to the community, prompting immediate maintenance releases for older supported branches, including updates for versions 2.27.3, 2.26.4, and the 2.27.0 release train.
Navigating these frequent security updates requires a clear understanding of the project’s maintenance schedule. GeoServer operates on a time-boxed release cycle that actively maintains both stable and maintenance versions over the course of a single calendar year. Because software dependencies and underlying libraries continually evolve, security maintainers strongly recommend that organizations upgrade their deployed instances to a supported release at least once every year to ensure they continue receiving critical security backports and vulnerability fixes. Comprehensive guidance for performing these transitions smoothly is documented in the official upgrading resources provided within the user manual.
Supply Chain Advisory Addresses GitHub Actions Infrastructure
Beyond traditional application-level vulnerabilities, the summer review brought attention to a supply chain advisory that threatened to undermine confidence in software download integrity. Supply chain advisories carry the potential to affect the overall trustworthiness of binaries and source code obtained from external repositories, making them a top priority for project maintainers.
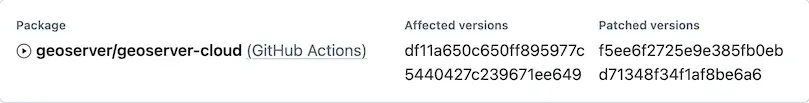
This incident marked the first time the GeoServer project has had to navigate an infrastructure-level advisory of this nature. Because the issue did not directly correspond to a standard source code release of GeoServer, it did not qualify for a traditional CVE tracking number. Instead, project maintainers formally classified the advisory under the designation of "geoserver/geoserver-cloud (GitHub Actions)."
Crucially, the project confirmed that no official GeoServer software releases were compromised or affected by the infrastructure incident. Standard GeoServer releases continue to be compiled using a dedicated Jenkins build server that publishes final distribution artifacts securely to both SourceForge and official OSGeo infrastructure. The incident nevertheless underscored the complex threat landscape surrounding modern software supply chains and automated CI/CD pipelines.
Responding to the Wave of AI-Assisted Vulnerability Reports
Like many other prominent open-source software projects across the global technology landscape, the GeoServer development and security teams have experienced a sudden, overwhelming wave of vulnerability reports generated with the assistance of artificial intelligence tools. While AI automation can occasionally assist researchers in discovering edge cases, it frequently generates massive volumes of verbose, low-signal reports that require extensive manual analysis by human maintainers.
Reviewing these AI-generated submissions consumes considerable time, particularly when determining whether a verbose report describes a genuine novel vulnerability or merely represents a duplicate of an existing ticket. To address this evolving trend, the project has established a dedicated general AI policy and updated its core security policy on GitHub. These policy updates explicitly acknowledge the integration of AI-generated content in the reporting pipeline and provide clear guidance to researchers on how to submit manageable, verifiable data.
Maintainers emphasize that when researchers utilize AI tools to generate submissions, being readily available on hand to clarify technical ambiguities is deeply appreciated. Furthermore, contributors who are positioned to independently test and verify proposed fixes significantly ease the heavy workload carried by the volunteer-driven geoserver-security team.
Community Participation and Reporting Vulnerabilities
As the demands on core maintainers continue to grow, the project is actively seeking deeper collaboration from the organizations and enterprises that rely on its geospatial technology for daily operations. Companies and public entities whose infrastructure depends on GeoServer are encouraged to financially sponsor the project or permit their internal engineering staff to directly participate in the geoserver-security working groups. Additionally, project leadership is working to establish formal project membership pathways specifically tailored for public institutions and government agencies that frequently face administrative restrictions regarding traditional financial sponsorships or external commercial participation.
For organizations and security researchers seeking to report a newly discovered security concern, the project maintains strict private disclosure channels. Confidential vulnerability reports should never be posted to public issue trackers or discussion forums. Instead, reporters are instructed to consult the official security policy hosted on the project’s GitHub repository, which outlines the secure procedures for submitting findings privately using GitHub security advisories and ensuring responsible coordination before any public notification takes place.