WASHINGTON — Several staff members inside the White House have been utilizing computers and mobile devices equipped with residential proxy services that inadvertently render their secure internet addresses available for outside entities to rent, according to cybersecurity experts. This unexpected exposure creates a glaring security loophole, allowing anonymous third parties to route their web traffic directly through the official networks of the Executive Office of the President.
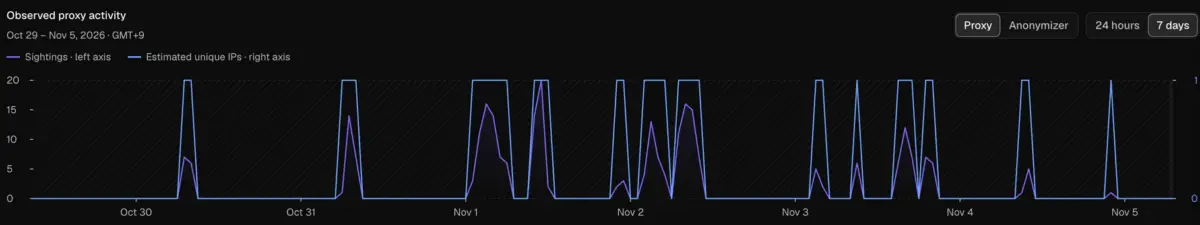
The alarming discovery was first made public by security firm Layer3 Intel, which reported that it detected multiple residential proxy nodes beaconing out from the specific internet address network reserved for the White House, designated as AS2650. According to Layer3, the proxy activity was relatively persistent over a month-long monitoring window, occurring frequently between October 5 and November 3. During this period, a comprehensive review of the active proxies available from the AS2650 range showed that they successfully exited from the White House network a total of 236 times.
Adding to the gravity of the situation, investigators found that one of the primary proxy services operating on the network is Infatica, a company with deep historical ties to Russian cyber operations. Proxy tracking company Synthient highlighted on social media platform X that the traffic originating from AS2650 was directly tied to multiple Windows 11 installations running the Infatica service. Infatica is a commercial proxy program frequently bundled into seemingly innocuous "free" mobile and desktop applications.
The roots of Infatica trace back to its founder, Vladimir Fomenko, a Russian national whose previous web hosting business, King Servers, served as the launchpad for major cyberattacks a decade ago. In 2016, King Servers was identified by researchers and intelligence agencies as the infrastructure provider for six of the eight internet addresses utilized by Russian state security services to breach and compromise election system databases in Arizona and Illinois.
Residential proxy providers operate in a legal and technical gray area, with dozens of varying legitimacy scattered across the globe, particularly in jurisdictions like Russia and China. At their core, these services allow customers to rent the residential or corporate internet addresses of unsuspecting everyday users to anonymize their online activities or spoof their true geographic locations. From the perspective of any website or service receiving traffic, the incoming connections appear to originate from the rented IP address rather than the actual proxy customer, effectively masking the user’s true identity and origin.
Data gathered by Layer3 Intel reveals that the proxy exit nodes operating out of the White House network spanned across six distinct internet addresses. This activity was recorded on 26 out of the 30 days monitored by the firm, with the vast majority of the connections taking place during evening hours, specifically between 5:00 p.m. and midnight local time.
More concerning still is that Infatica was not an isolated anomaly. Layer3 Intel disclosed that its investigation uncovered a total of 28 separate residential proxy services that were somehow able to route their traffic and exit through the official White House network.
"This is public access," the Layer3 Intel research team wrote in a detailed analysis of the incident. "Anybody can obtain it by signing up to a public residential proxy service, paying a few dollars and sending requests through it. We did not selectively target this network or try to make our probes exit from it. We caught this by chance, simply by requesting global rotating access through these services."
The White House did not immediately respond to requests for comment regarding the security findings.
The exposure highlights a broader, systemic cybersecurity challenge that has grown increasingly severe over recent years. Residential proxy services have emerged as a primary vector for a wide array of malicious and unwanted traffic across the digital landscape. Cybercriminals routinely lean on these networks to execute account takeover attacks, perpetrate online advertising fraud, and carry out large-scale content scraping operations to feed data-hungry artificial intelligence projects.
Beyond general fraud, these services introduce profound local network vulnerabilities. In late 2025, security researchers uncovered a widespread campaign where malicious actors systematically exploited architectural vulnerabilities inherent in residential proxy frameworks. These flaws allowed attackers to probe individual proxy endpoints to discover vulnerable systems residing on local networks, subsequently infecting them with malware. The situation escalated to a crisis point in January 2026, when dozens of proxy networks were forced to scramble and patch their infrastructure after Synthient Founder Ben Brundage publicly demonstrated how cybercriminals were exploiting these vulnerabilities to seize direct administrative control over devices sitting securely behind the firewalls of unsuspecting users.
"Some of these resellers sell bandwidth for as low as 60 cents a Gigabyte, that means for less than a dollar you can gain access into some of the most confidential and trusted networks," Brundage told KrebsOnSecurity, emphasizing how loose verification standards exacerbate the threat. "The reseller ecosystem further enables this with any criminal able to buy access while skipping KYC [Know Your Customer] processes."
The propagation of these services typically begins on the endpoint devices of everyday users, which are frequently brought directly into high-security corporate and government workplaces. Application developers frequently integrate software development kits (SDKs) provided by residential proxy networks into consumer software to monetize their products. By doing so, developers receive a modest financial payout for every installation, turning ordinary user devices into commercial proxy nodes without the user fully understanding the security implications.
While the presence of residential proxies on government networks sounds like an extreme anomaly, security telemetry suggests it is surprisingly common. A webinar conducted by proxy tracking service Spur in January 2026 revealed that residential proxies had been detected operating within nearly 300 government-owned and operated networks. The same tracking data found similar infections across 318 utility companies, 166 healthcare organizations and hospitals, and 141 financial and banking institutions. Furthermore, security firm Infoblox reported earlier this year that an astonishing 65% of its entire enterprise customer base had corporate devices querying one or more residential proxy-related domains.