The GeoServer project has issued a comprehensive security recap detailing a turbulent summer of 2026, highlighted by an unpatched zero-day vulnerability, multiple Common Vulnerabilities and Exposures (CVEs), a notable supply chain advisory, and an influx of AI-assisted vulnerability reports.
Administrators and organizations responsible for managing GeoServer instances are being strongly advised to apply the latest security patches immediately. The project has released version 3.0.1, version 2.28.5, and version 2.27.6 to address critical vulnerabilities affecting the widely used open-source geospatial data server.
For years, the GeoServer project has adhered strictly to a coordinated vulnerability disclosure policy. Under this framework, security flaws are thoroughly investigated, validated, and patched across both stable and maintenance release lines before any official CVE details or technical specifics are made public. The core objective of this responsible disclosure timeline is to provide system administrators, enterprise IT teams, and public institutions with adequate opportunity to test and deploy updates before malicious actors can reverse-engineer the patches and weaponize the flaws. However, maintaining this protective buffer relies heavily on discretion from all participating researchers and third-party observers.
The August Zero-Day Incident
That careful equilibrium was severely tested in August 2026, when GeoServer encountered its first major zero-day vulnerability of the year—an active exploit in the wild with no official fix deployed at the exact moment of public disclosure. The underlying technical problem had already been identified and reported privately to the project through responsible channels by several independent security researchers. A remediation patch had already been scheduled and queued up for inclusion in the forthcoming GeoServer 3.0.1 release cycle.
The zero-day situation escalated rapidly because an unrelated third party—completely unconnected to the core development team or the original researchers who discovered the issue—decided to publicly disclose the vulnerability details on social media. The fallout was immediate and severe. Automated vulnerability scanners and threat actors began probing systems for the flaw within hours of the public social media post going live.
The velocity of the subsequent exploitation attempts caught the attention of cybersecurity journalists, leading to widespread industry news coverage and an urgent directive for administrators to patch their systems disseminated through the official GeoServer user forums. Project leadership publicly expressed their gratitude to security reporter Ravie Lakshmanan, who first notified project leadership through the Open Source Geospatial Foundation, helping trigger the emergency response.
The rapid rollout of GeoServer 3.0.1, GeoServer 2.28.5, and GeoServer 2.27.6 was designed to stem the tide of potential breaches. This tense episode powerfully reaffirmed the absolute necessity of adhering strictly to coordinated vulnerability disclosure policies and underscored why enterprise users must prioritize updating their mapping infrastructure the moment new releases become available.
Previously Published CVEs and Release Management
The summer security turbulence was not limited to the August zero-day event. Earlier in the season, on June 11, 2026, the project published a separate batch of CVEs coinciding with the major rollout of GeoServer 3.0.0. These vulnerabilities impacted several preceding versions, prompting immediate updates across the older maintenance branches, including GeoServer 2.27.3, 22.6.4, and specific components of GeoServer 2.27.0.
Managing these multifaceted security updates is part of a broader, time-boxed release cycle that the GeoServer project maintains over the course of each year, balancing both stable and maintenance release lines. Because software environments are constantly evolving, relying on outdated mapping infrastructure leaves organizations exposed to discovered flaws that are no longer receiving backported patches. Project maintainers strongly recommend that organizations upgrade their deployments to a supported release at least once a year to ensure continuous access to critical security fixes and patches. Comprehensive instructions and upgrade paths are documented in the official user guide to assist administrators through the transition process.
Navigating the Software Supply Chain Advisory
In addition to direct software vulnerabilities, the GeoServer project faced a different kind of security test earlier in the season with a supply chain advisory. Supply chain advisories carry the inherent potential to disrupt the integrity of software downloads, creating widespread anxiety among enterprise users who rely on trusted binaries.
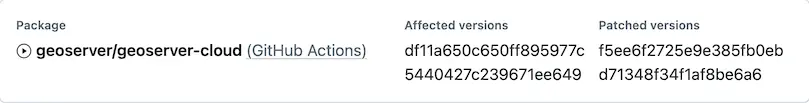
This instance marked the first time the project had ever had to navigate an infrastructure-level advisory of this nature. Because the issue did not directly correspond to a formal release of the GeoServer application itself, it did not neatly qualify for a traditional CVE tracking number. Instead, project maintainers classified the advisory specifically under GitHub Actions associated with the geoserver/geoserver-cloud repository.
Crucially, the project confirmed that no official GeoServer releases were compromised or affected by the supply chain incident. Standard GeoServer releases are compiled using an isolated Jenkins build server that publishes final software artifacts directly to SourceForge and the official Open Source Geospatial Foundation infrastructure, maintaining a secure separation from third-party workflow environments.
The Rising Wave of AI-Assisted Vulnerability Reports
Beyond traditional vulnerabilities and infrastructure concerns, the GeoServer security team has faced an unprecedented surge in security reports generated with the assistance of artificial intelligence tools. Like many prominent open-source software projects across the global technology ecosystem, GeoServer is currently experiencing a wave of automated and AI-assisted vulnerability submissions that often produce large volumes of verbose, generalized text.
To manage this new operational reality, the project has established a general AI policy and updated its core security policy on GitHub. These policy updates explicitly acknowledge the integration of AI tools in security research and provide clear guidance for individuals submitting reports.
While AI tools can assist in the broad exploration of codebases, they frequently generate false positives, duplicate submissions, or complex, verbose descriptions that require substantial human effort to parse. Reviewing these reports, determining if they represent novel issues or duplicates, and verifying potential fixes consumes considerable time from the volunteer-driven security team. Project maintainers have emphasized that human researchers who are willing to stay on hand to clarify verbose AI-generated submissions, test proposed patches, and verify fixes provide invaluable assistance to the overburdened security workflow.
Community Support and Security Participation
Securing a complex, enterprise-grade open-source geospatial platform requires a collaborative commitment from the entire community of users, organizations, and institutional stakeholders. Maintaining a dedicated security team and rapid response infrastructure depends heavily on continuous resourcing and active participation.
Organizations whose critical business operations, public utilities, or governmental workflows depend on GeoServer are encouraged to consider financial sponsorship of the project. Alternatively, organizations can support the ecosystem by allowing their technical staff to directly participate in the geoserver-security workgroup and mailing lists.
Furthermore, to accommodate public institutions and government agencies that often face rigid institutional restrictions regarding direct commercial software sponsorship and participation, the project is actively working to establish formal project membership pathways via GSIP-243. This initiative aims to clear bureaucratic hurdles and enable broader institutional collaboration in safeguarding critical open-source geographic information systems.
Administrators seeking to report newly discovered vulnerabilities privately can do so by reviewing the project’s security policy on GitHub, which outlines instructions for utilizing private security advisories. By working together through responsible disclosure channels, the global GeoServer community can better navigate emerging zero-day threats, supply chain complexities, and the evolving landscape of AI-assisted security research.