The GeoServer project has issued a comprehensive security recap detailing a turbulent summer of 2026, which included managing a critical zero-day vulnerability, addressing previously published Common Vulnerabilities and Exposures (CVEs), navigating a software supply chain advisory, and adapting to an influx of AI-generated vulnerability reports. Project maintainers are urging all administrators responsible for deploying GeoServer instances to update immediately to the newly released patches: GeoServer version 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6.
The recent security events underscore the vital importance of maintaining up-to-date geographic information system software and following responsible disclosure guidelines. GeoServer operates under a coordinated vulnerability disclosure policy. Under this framework, security flaws are patched simultaneously across both stable and maintenance release branches prior to the public publication of CVE details. The fundamental objective of this approach is to provide all users and system administrators with a reasonable window of opportunity to apply necessary updates before malicious actors can weaponize the information.
August Zero-Day Vulnerability Sparks Rapid Response
The most alarming incident of the summer occurred in August, when GeoServer faced a high-pressure zero-day vulnerability—an active exploit in the wild operating without a known official fix at the time of discovery. Prior to the public breach, the underlying problem had already been reported privately to project maintainers by several independent researchers. A permanent fix had been scheduled for inclusion in the upcoming GeoServer 3.0.1 release cycle.
However, the situation escalated rapidly when an unconnected third party outside the core project and independent research groups publicly disclosed the vulnerability on social media. The consequences were immediate and severe. Automated scanning activity and active exploitation attempts targeting this specific vulnerability were detected by monitoring systems within hours of the public social media post.
The velocity of this security event prompted urgent news coverage across the cybersecurity landscape, alongside immediate warning announcements disseminated through the Open Source Geospatial Foundation user forums. Project leadership formally acknowledged the swift reporting efforts of security researcher Ravie Lakshmanan, who initially notified the Open Source Geospatial Foundation of the unfolding situation.
The emergency releases of GeoServer 3.0.1, GeoServer 2.28.5, and GeoServer 2.27.6 were expedited to neutralize the threat. Project organizers noted that this intense episode dramatically reaffirms the critical importance of adhering strictly to coordinated vulnerability disclosure policies and underscores why administrators must apply patches immediately upon publication.
Previously Published CVEs and Software Lifecycle Management
The summer security recap also highlights a series of vulnerabilities published earlier in the season. On June 11, 2026, concurrent with the major rollout of the GeoServer 3.0.0 release, a batch of CVEs was disclosed. These historical entries required coordinated updates across multiple maintenance branches, including GeoServer versions 2.27.3, 2.26.4, and the initial 2.27.0 release train.
Managing vulnerabilities across multiple active codebases requires significant coordination from the volunteer and contributor community. GeoServer operates on a time-boxed release cycle, maintaining designated stable and maintenance versions over the course of a single calendar year. Because of this continuous evolution, project maintainers strongly recommend that organizations upgrade their deployments to a supported release at least once every twelve months to ensure continuous coverage against newly discovered security threats. Detailed migration paths and upgrade guidance are maintained within the official GeoServer user documentation to assist administrators through the transition processes.
Navigating Supply Chain Advisories and Infrastructure Security
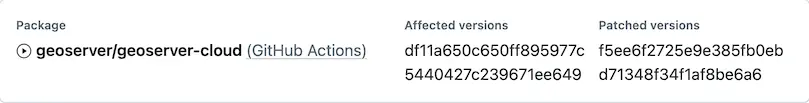
In addition to traditional application-level software flaws, the GeoServer project encountered a unique hurdle involving a software supply chain advisory during the summer review period. This incident marked the first time the project has had to navigate an infrastructure-level advisory of this nature. Because the advisory targeted the build and continuous integration pipeline—specifically affecting the "geoserver/geoserver-cloud" configuration within GitHub Actions—rather than a direct source code release of GeoServer itself, it did not qualify for a standard CVE tracking number.
Project leadership emphasized a critical point of reassurance for enterprise users: no official GeoServer software releases were compromised or affected by this supply chain event. Standard GeoServer software releases are compiled and published through an isolated Jenkins build server, which subsequently distributes validated artifacts to SourceForge and official Open Source Geospatial Foundation infrastructure repositories. Nonetheless, supply chain advisories of this nature carry the potential to cause uncertainty regarding the integrity of downloaded development components, prompting project maintainers to document and transparently address the pipeline-level warning.
Adapting to the Wave of AI-Assisted Vulnerability Reports
Like many prominent open-source software communities, the GeoServer project has experienced a dramatic surge in vulnerability reports generated with the assistance of artificial intelligence tools. These AI-generated submissions frequently present unique logistical challenges for core developers, as they tend to be exceptionally verbose, time-consuming to review, and difficult to deduplicate against existing known issues.
To manage this growing administrative overhead, the project has established a dedicated general AI policy and formally updated its overarching security policy. These institutional updates are designed to acknowledge the modern reality of AI-assisted security research while providing clear guidance for external submitters. Maintainers have noted that when security researchers utilize AI tools to generate reports, being readily available on communication channels to clarify ambiguities, test proposed patches, and verify fixes is immensely appreciated by the overburdened security team. Alleviating the workload for core developers helps ensure that genuine security threats can be triaged and remediated with maximum efficiency.
Community Participation and Reporting Vulnerabilities
As the GeoServer ecosystem continues to power critical geographic infrastructure worldwide, sustaining its security operations remains an ongoing challenge. Project leadership has issued an open call for support from organizations that rely heavily on the platform. Enterprise users are encouraged to consider financial sponsorship through the official project channels or to authorize engineering staff to participate directly in the dedicated GeoServer security mailing lists and working groups. Furthermore, the project is actively working to establish formal project membership structures to accommodate public institutions and government agencies that frequently face administrative restrictions regarding direct corporate sponsorship and participation.
For individuals or organizations seeking to report newly discovered security vulnerabilities, the GeoServer project maintains a strict private reporting protocol. Security researchers and system administrators are instructed to consult the official security policy hosted on the project’s GitHub repository, which provides explicit guidelines for submitting vulnerability details privately utilizing GitHub security advisories prior to any public disclosure.