The GeoServer project has issued a comprehensive security recap detailing a turbulent summer of 2026, highlighted by an urgent August zero-day vulnerability, multiple previously published Common Vulnerabilities and Exposures (CVEs), and a notable supply chain advisory. In response to these developments, project maintainers are strongly urging all administrators and organizations responsible for GeoServer instances to update their deployments immediately to either GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6.
The open-source geospatial project strictly adheres to a coordinated vulnerability disclosure policy. Under this framework, security flaws are thoroughly investigated, patched, and fixed across both stable and maintenance release branches before any official CVE details are published to the public. The primary objective of this staggered timeline is to provide system administrators, enterprises, and public institutions worldwide with an adequate window of opportunity to apply necessary updates and secure their environments prior to broad public awareness.
However, this carefully managed security process faced a significant disruption during the summer months, putting the spotlight back on the critical importance of timely patching and responsible disclosure practices across the broader software ecosystem.
The August Zero-Day Incident
In August 2026, the GeoServer project encountered a severe zero-day vulnerability, representing an actively exploited security flaw in the wild for which no official fix was publicly available at the time of the leak. Prior to the public exposure, the underlying problem had already been responsibly reported through private channels by several independent security researchers, and a formal remediation patch had been scheduled for inclusion in the upcoming GeoServer 3.0.1 release.
The volatile zero-day situation materialized when an unrelated third party—completely unconnected to the core development project or the original researchers who discovered the issue—decided to disclose the technical details publicly on social media. The fallout from this premature disclosure was swift and immediate. Automated network scans and targeted exploit attempts searching for vulnerable GeoServer instances were detected by security monitors within mere hours of the social media post going live.
The rapid escalation triggered widespread media coverage and prompted project leadership to issue an urgent call to action across official user forums, urging administrators to update their software without delay. Project leadership publicly expressed gratitude to reporter Ravie Lakshmanan for first notifying project leadership via the Open Source Geospatial Foundation, helping accelerate awareness before malicious exploitation could spread further.
This intense episode reaffirmed the vital importance of strictly adhering to coordinated vulnerability disclosure policies and underscored why system administrators must prioritize applying new releases the moment they are made available by the maintainers.
Previously Published CVEs and Release Cycles
The summer security recap also reviewed vulnerabilities published earlier in the season, notably on June 11, 2026, which coincided with the major release of GeoServer 3.0.0. Those earlier security advisories impacted multiple branches, resulting in rapid updates across versions such as GeoServer 2.27.3, 2.26.4, and 2.27.0 to neutralize risks.
GeoServer operates using a structured, time-boxed release cycle that maintains both stable and maintenance release lines over the course of a year. To maintain robust defense postures against evolving threat landscapes, maintainers strongly recommend that organizations upgrade their software installations to a supported release at least once every year. Consistent upgrading ensures that server instances continue to receive crucial security backports and bug fixes. Administrators seeking detailed technical guidance can consult the official user guide documentation regarding upgrading existing versions.
Supply Chain Advisory and Infrastructure Security
Adding to the complexity of the summer months, the project encountered its first-ever supply chain infrastructure advisory. Because supply chain advisories have the potential to compromise the integrity of software downloads, maintainers closely scrutinized the situation to protect the user base.
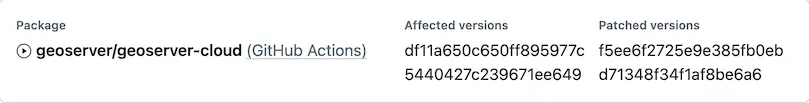
It is important to note that no official GeoServer releases were actually affected by this infrastructure event. Standard GeoServer releases are compiled and published using a dedicated Jenkins build server that distributes artifacts securely to both SourceForge and the Open Source Geospatial Foundation infrastructure. Instead, the specific supply chain advisory was classified under the designation of "geoserver/geoserver-cloud (GitHub Actions)" because it did not correspond with an official release of the core GeoServer software package and, consequently, did not qualify for a traditional CVE tracking number. This distinction highlights the growing complexity of modern software supply chains, where ancillary development and automation pipelines require just as much vigilance as the primary application code.
AI-Assisted Vulnerability Reports and Updated Policies
In addition to handling traditional security disclosures, the GeoServer maintainers reported experiencing a massive surge in vulnerability reports generated with the assistance of artificial intelligence tools, a trend mirroring challenges faced by numerous other open-source software projects across the industry.
To manage this growing influx, the project has established a general AI Policy and updated its comprehensive Security Policy. These updated guidelines officially acknowledge the reality of AI-generated submissions and provide clear instructions for researchers utilizing automated tools. Because AI-generated reports are frequently very verbose and can generate significant noise, project maintainers emphasize that having researchers on hand to clarify technical details is deeply appreciated.
Reviewing these automated submissions often consumes substantial time, requiring security teams to carefully analyze lengthy text, determine validity, and identify duplicate submissions. Project maintainers note that researchers who are able to actively test and verify proposed fixes as they are developed provide invaluable assistance, helping lighten the workload for the dedicated geoserver-security team.
Community Participation and Reporting Vulnerabilities
As the GeoServer project continues to navigate these security challenges, maintainers are actively encouraging organizations that depend heavily on geospatial infrastructure to contribute to the project’s sustainability. Enterprises and private entities can support the project financially through sponsorships or by authorizing internal staff to directly participate in the geoserver-security working groups. Furthermore, the project is working to establish new pathways for project membership specifically tailored to public institutions that may face bureaucratic restrictions regarding direct financial sponsorships or community participation.
For individuals or security researchers who discover potential security flaws within the software, the GeoServer project maintains a transparent reporting channel. Detailed instructions on how to report vulnerabilities privately using GitHub security advisories can be found directly within the project’s official security policy documentation.