Federal Bureau of Investigation agents have arrested a high-ranking executive from a Canadian cybersecurity firm in Pennsylvania, marking a dramatic new phase in an escalating international investigation into the notorious ShinyHunters hacking collective. The arrest follows a brazen cyberattack by the group that compromised sensitive personnel records of thousands of FBI agents, according to multiple sources familiar with the matter.
The New York Times reported that federal authorities apprehended the Canadian man in Pennsylvania on suspicion of assisting ShinyHunters. While neither the initial newspaper report nor a social media statement from FBI Director Kash Patel officially identified the suspect by name, sources close to the unfolding investigation confirmed his identity to KrebsOnSecurity.
According to investigators, the suspect had traveled to Pennsylvania to attend a prominent cyber insurance conference. His professional background and company specialization centered heavily on handling high-stakes ransomware negotiations and corporate extortion cases on behalf of targeted organizations. Separate sources familiar with the federal probe indicated that operational control and prosecution efforts concerning the ShinyHunters case have recently been centralized at a specialized FBI field office in Texas.
Publicly available records and conference schedules show that the Cyber Risk Summit took place at the Loews Philadelphia Hotel. The multi-day event featured numerous corporate participants and sponsors, with a Canadian cybersecurity firm named Cypfer listed as its premier sponsor.

Corporate and professional networking profiles reveal further connections within the close-knit Canadian cybersecurity community. One of Cypfer’s former affiliates is Edward Dubrovsky, who later became associated with another Canadian security firm and conference sponsor, CyberSteward. Approximately a month prior to the conference, Dubrovsky publicly shared on social media his plans to attend the Cyber Risk Summit alongside members of the CyberSteward team.
Following inquiries into the executive’s professional history, a spokesperson for Cypfer clarified that Dubrovsky was never a founder or co-founder of the firm, contrary to claims on his professional profile, but instead served as a managing director prior to his resignation.
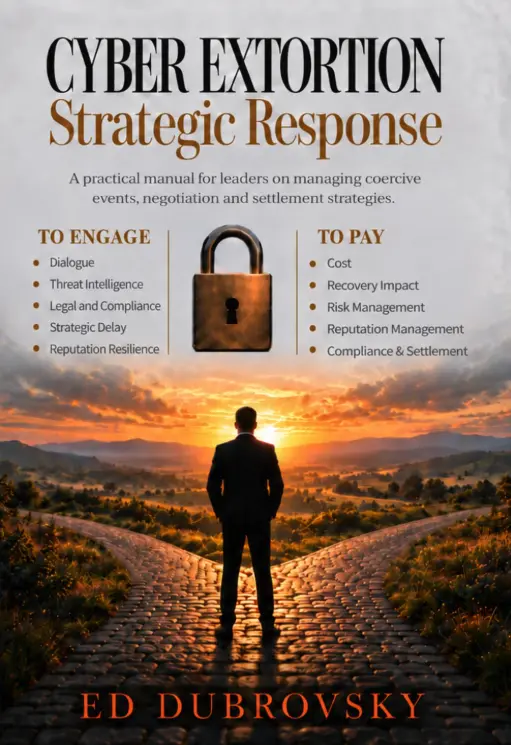
Prior to his legal troubles, Dubrovsky maintained a public profile as an expert in extortion defense and strategy. He authored a comprehensive book focusing on the intricacies of ransomware incidents, which purported to guide organizations through post-breach decision-making, crisis communication, and crisis recovery. Promotional materials for the publication emphasized a key operational distinction: that communicating with cyber extortionists is fundamentally separate from negotiating a financial settlement, and that opening lines of communication does not equate to a commitment to pay criminal actors. Instead, professional engagement with threat groups can be utilized to verify attacker claims, collect critical threat intelligence, buy operational time, and preserve strategic options.
Federal court records indicate that an individual named Edward Dobrovsky—with a slight spelling variation in the last name—was taken into custody in Pennsylvania on October 8, facing serious federal charges including cyber extortion and conspiracy. While the core criminal complaint and several related documents have been placed under seal by the court, a docket summary indexed on public legal databases outlines specific charges. The defendant is formally accused of conspiracy to threaten the impairment of information confidentiality with the intent to extort money, alongside charges of interference with commerce through threats.
U.S. Bureau of Prisons inmate records initially located a 54-year-old Edward Dubrovsky within a federal holding facility in Philadelphia. However, court filings indicate that the legal proceedings were officially transferred to the U.S. District Court for the Eastern District of Texas. Legal representatives or court-appointed counsel for Dubrovsky were not immediately established in the initial public dockets, and the defendant could not be reached for immediate comment. Representatives for CyberSteward have likewise been sought for comment regarding the ongoing situation.

The federal investigation centers on the activities of ShinyHunters, a prolific cybercriminal syndicate known for utilizing targeted phishing campaigns and compromised credentials to infiltrate corporate software-as-a-service environments. Once inside corporate networks, the group siphons vast quantities of proprietary and sensitive data, subsequently issuing extortion demands and threatening to publish the stolen material publicly unless substantial ransom payments are met. According to estimates provided by the FBI, the hacking group has successfully extorted upward of $70 million from corporate and organizational victims throughout the year.
The current wave of arrests stems from a concerted international law enforcement push. Last month, Dutch authorities arrested Pepijn van der Stap, a convicted cybercriminal, during coordinated raids connected to the ShinyHunters syndicate. Federal investigators have since been meticulously analyzing electronic devices seized during the European operation. Sources familiar with the ongoing inquiry suggest that additional criminal charges against key figures at other specialized ransomware negotiation and advisory firms could be forthcoming as the investigation widens.
The pressure on the hacking collective intensified dramatically following Van der Stap’s arrest. A prominent threat actor operating under the online moniker "Rey" assumed leadership of the ShinyHunters group and launched a public taunting campaign against law enforcement. This provocation followed a high-profile security breach that compromised the FBI’s online recruitment portal, exposing sensitive records detailing agents’ individual unit assignments, specific specializations, and confidential medical and psychiatric documentation.
Investigative reports subsequently identified "Rey" as a teenager named Saif Al-din Khader. Law enforcement authorities tracked and detained the young hacker as the cybercrime collective attempted to execute an extortion campaign against a digital aviation and navigation unit that had been divested by Boeing. Khader has since been cooperating with federal investigators as the sprawling multi-jurisdictional inquiry continues to unfold.