The GeoServer project has published a comprehensive security recap detailing a turbulent summer of 2026, highlighted by a high-profile zero-day vulnerability, multiple Common Vulnerabilities and Exposures (CVEs), and emerging challenges surrounding AI-generated security reports. Project maintainers are urging all administrators running affected instances to update immediately to the newly released patches.
For organizations managing GeoServer deployments, the immediate directive is clear: administrators should upgrade their instances to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6 without delay. These releases contain critical fixes designed to close security gaps that have emerged over recent months.
The open-source project traditionally operates under a strict coordinated vulnerability disclosure policy. Under this framework, security flaws are patched simultaneously across both stable and maintenance release branches prior to the public publication of CVE details. The overarching goal of this coordinated approach is to give every user and enterprise organization a fair opportunity to apply updates before malicious actors can analyze vulnerability details and develop weaponized exploits.
However, maintaining this security equilibrium faced a severe test during the summer months due to premature public disclosures and changing technological landscapes within the broader open-source community.
The August Zero-Day Incident
In August, the GeoServer project confronted a critical zero-day vulnerability—an active exploit in the wild for which no official patch had yet been publicly released. Prior to the incident, the underlying security problem had already been privately reported to project maintainers by several independent researchers. A comprehensive fix had already been scheduled and queued for inclusion in the upcoming GeoServer 3.0.1 release.
The zero-day situation escalated rapidly when an unrelated third party, having no connection to the project or the original researchers who discovered the issue, chose to disclose the vulnerability publicly on social media channels. The consequences of this premature disclosure were instantaneous and measurable. Automated security scans searching for vulnerable instances were detected across the internet within hours of the public social media post appearing online.
The speed and aggressiveness of this automated exploitation response underscored the severe risks associated with uncoordinated disclosures. It quickly generated widespread news coverage across cybersecurity publications and prompted an urgent call to action on the official GeoServer user forum. Project leadership formally acknowledged the situation and extended their gratitude to journalist Ravie Lakshmanan for first notifying project leadership regarding the active exploitation via the Open Source Geospatial Foundation.
Following the incident, the rapid deployment of GeoServer 3.0.1, GeoServer 2.28.5, and GeoServer 2.27.6 successfully mitigated the active threats. Project organizers noted that this turbulent experience forcefully reaffirmed the absolute importance of adhering to coordinated vulnerability disclosure policies and emphasized why prompt upgrading remains essential whenever new releases become publicly available.
Previously Published CVEs and Release History
The summer security updates built upon a foundation of earlier patches released earlier in the year. On June 11, 2026, alongside the major GeoServer 3.0.0 release, project maintainers published a series of CVEs addressing various security defects across multiple supported versions, ensuring that both legacy and current installations received necessary hardening.
These historical patches highlight the continuous maintenance lifecycle of the platform, where developers constantly work to identify and neutralize potential entry points for attackers. Enterprise users maintaining long-term deployments have consistently been advised to keep abreast of these scheduled releases rather than relying on isolated installations that miss critical maintenance cycles.
Navigating a Supply Chain Advisory
In addition to direct software vulnerabilities, the project encountered a unique security hurdle involving a supply chain advisory. Supply chain advisories carry the inherent potential to disrupt the integrity of software downloads by casting doubt on the build pipeline or third-party dependencies utilized during development.
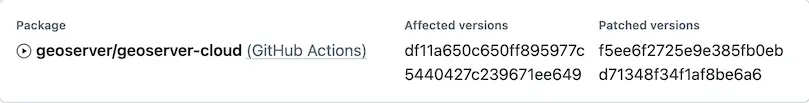
This event marked the first time the GeoServer project has had to navigate an infrastructure advisory of this nature. Because the issue did not originate from or correspond with an official release of the GeoServer codebase itself, it did not meet the traditional criteria required to qualify for a CVE identifier. Consequently, the project categorized the advisory specifically under "geoserver/geoserver-cloud (GitHub Actions)" to reflect its true origin within cloud-based automation tooling rather than the core application source code.
Crucially, project leadership confirmed that no official GeoServer releases were affected by this supply chain concern. GeoServer releases are compiled and published through a secure, dedicated Jenkins build server that distributes trusted artifacts to both SourceForge and the core OSGeo infrastructure, maintaining a strict firewall between cloud-based auxiliary tooling and final production binaries.
The Rise of AI-Assisted Vulnerability Reports
Like many other prominent open-source software projects in the modern threat landscape, the GeoServer security team has experienced a significant surge in vulnerability reports generated with the assistance of artificial intelligence tools.
These AI-generated submissions often present unique administrative challenges for maintainers. Because automated tools frequently generate highly verbose outputs filled with speculative analysis, security teams must expend considerable time and human resources to review the submissions, verify whether reported flaws are genuine, and determine if incoming reports are mere duplicates of existing tickets. Furthermore, verifying these reports often requires hands-on testing to validate fixes as vulnerabilities are addressed.
To manage this evolving trend constructively, the project has established a general AI Policy and updated its comprehensive Security Policy. These policy updates formally acknowledge the utilization of AI tools in vulnerability research and provide clear guidance for researchers submitting findings to the project. Maintainers have emphasized that while automated tooling can assist researchers, having knowledgeable individuals on hand to clarify findings, test proposed fixes, and assist the geoserver-security team remains profoundly appreciated.
Community Support and Participation
Securing a widely used open-source geospatial platform requires robust community collaboration and sustained resource allocation. Organizations and public institutions that depend heavily on GeoServer for critical spatial data infrastructure are encouraged to support the project financially through sponsorship programs or by allowing their internal technical staff to participate directly in the geoserver-security working groups.
Additionally, the project is actively working to establish formal project membership structures tailored specifically for public institutions and governmental agencies that may face institutional restrictions regarding traditional financial sponsorship or direct participation in open-source foundations.
Upgrade Cadence and Best Practices
GeoServer operates on a structured, time-boxed release cycle, systematically maintaining both "stable" and "maintenance" release lines over the course of each calendar year. To maintain robust defense-in-depth postures, administrators are strongly advised to upgrade their operational deployments to a supported release at least once every year to ensure uninterrupted access to critical security patches, bug fixes, and performance improvements. Detailed upgrade instructions and migration paths are maintained within the official user guide for existing installations.
For security researchers and enterprise administrators seeking to report newly discovered vulnerabilities privately, the project maintains a formal disclosure process utilizing GitHub security advisories, ensuring that potential flaws are handled securely and responsibly before any public remediation steps are taken.