Federal Bureau of Investigation agents have arrested a prominent Canadian cybersecurity executive in Pennsylvania in connection with an escalating international investigation into the notorious ShinyHunters hacking group. The high-profile arrest comes on the heels of a massive breach in which the cybercrime collective managed to siphon sensitive data concerning thousands of law enforcement personnel directly from the bureau.
Multiple sources confirmed the arrest to KrebsOnSecurity, noting that the suspect was taken into custody while visiting the United States to attend a prominent cyber insurance and risk conference. While initial reports from outlets like The New York Times and public statements from FBI Director Kash Patel confirmed the detention of a Canadian man in Pennsylvania on suspicion of assisting ShinyHunters, they initially withheld specific identifying details. However, subsequent federal court records and industry sources have shed light on the unfolding case, which has quickly become one of the most sensitive cybercrime prosecutions of the year.
A Conference Interrupted by Federal Agents
According to sources close to the unfolding investigation, the Canadian executive traveled to Pennsylvania during the first week of October to participate in the annual Cyber Risk Summit, which took place at the Loews Philadelphia Hotel between October 5 and October 7. The multi-day event draws leaders from across the cyber insurance, legal, and security sectors to discuss emerging threats, risk management, and the complex landscape of digital extortion.
While the summit featured numerous sponsors, online documentation from the event indicates that its largest financial backer was Cypfer, a Canadian security firm specializing in digital forensics and incident response. Background searches on LinkedIn and corporate registries link the arrested executive to both Cypfer and another security firm participating as a conference sponsor, CyberSteward. Approximately a month prior to the conference, the executive had publicly shared his travel plans and enthusiasm on professional networking platforms, anticipating continued industry discussions regarding global ransomware advisory, negotiation, and settlement strategies.
Following inquiries regarding corporate affiliations, a spokesperson for Cypfer clarified that the individual had previously served as a managing director before resigning from the firm in November 2025, disputing claims on professional profiles regarding a co-founder status.

Court Filings and Relocation to Texas
Federal court documents filed on October 8 under the name Edward Dobrovsky—reflecting a slight spelling variation of the suspect’s last name—reveal that he faces severe federal charges including cyber extortion and conspiracy. While several core documents, including the primary criminal complaint, remain under seal to protect ongoing investigative measures, a summary indexed at CourtListener.com outlines specific charges. The defendant is accused of "conspiracy to threaten to impair the confidentiality of information with the intent to extort money" and "interference with commerce by threats."
U.S. Bureau of Prisons inmate locator data initially indicated that a 54-year-old individual matching the suspect’s description was being held at a federal detention facility in Philadelphia. However, court dockets show that a transfer order was swiftly executed on October 9, moving the legal proceedings to the U.S. District Court for the Eastern District of Texas. According to individuals familiar with the matter, the Texas field office has become the centralized command center for the expansive, multi-jurisdictional investigation targeting the ShinyHunters network.
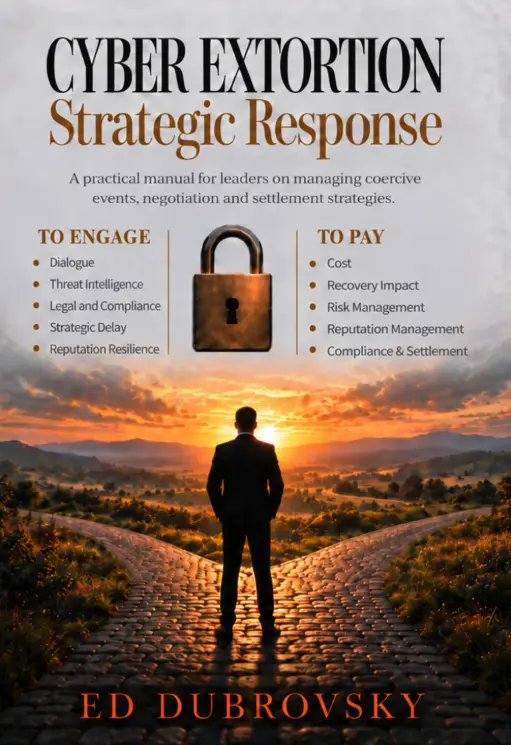
The suspect’s professional background intersects directly with the legal charges he now faces. He is the author of a comprehensive 252-page volume titled Cyber Extortion Strategic Response, a manual intended to guide organizations through the complex decision-making processes required during ransomware attacks. An excerpt from the book’s promotional materials underscores a recurring theme in his professional philosophy: communicating with malicious actors is distinct from negotiating a payment, and engagement can serve tactical objectives such as testing attacker claims, gathering intelligence, and buying time.
At the time of his initial court appearances, available records indicated that the defendant had not yet retained private legal counsel or been formally assigned a public defender by the court. Representatives for CyberSteward and other associated entities could not be immediately reached for comment regarding the arrest.
The Broader ShinyHunters Campaign
The federal case against the security executive unfolds against the backdrop of an aggressive wave of digital extortion orchestrated by ShinyHunters. The collective typically employs sophisticated phishing tactics and stolen corporate credentials to infiltrate software-as-a-service providers, exfiltrating vast proprietary datasets and threatening public leaks unless exorbitant ransoms are satisfied. According to assessments shared by federal law enforcement, the group has successfully extorted upward of $70 million from corporate and institutional victims over the course of the year.

The investigation has accelerated rapidly in recent weeks following coordinated international law enforcement actions. Last month, Dutch police apprehended Pepijn van der Stap, a reformed hacker suspected of involvement with the syndicate, prompting investigators to pore over seized digital devices for operational intelligence. Sources indicate that these forensic examinations may soon yield additional charges against principals at other specialized ransomware negotiation and advisory firms.
The arrest also follows a period of intense provocation directed at federal authorities. Immediately following Van der Stap’s capture, an individual operating under the online moniker "Rey" assumed leadership of ShinyHunters and began openly taunting the FBI. The group published stolen records harvested from the bureau’s online recruitment portal, exposing sensitive personnel data including unit assignments, professional specializations, and confidential medical and psychiatric histories.
Subsequent international reporting identified "Rey" as a teenager named Saif Al-din Khader. Law enforcement authorities detained Khader as the collective attempted to execute an extortion scheme targeting a navigation and digital aviation division recently divested by Boeing. Investigators later confirmed that Khader began cooperating with federal authorities following his apprehension.
As federal prosecutors begin laying out their case in the Eastern District of Texas, the investigation into how corporate advisory networks intersect with criminal extortion syndicates remains active, with further developments anticipated as court proceedings advance.