The GeoServer project team has released a comprehensive security recap detailing a turbulent summer of 2026, highlighted by an urgent zero-day exploit, a series of Common Vulnerabilities and Exposures (CVEs), a software supply chain advisory, and the formal introduction of new policies regarding artificial intelligence-generated security reports. Administrators managing GeoServer instances are being strongly urged to review their current deployments and update immediately to the latest patched versions.
For organizations and system administrators responsible for maintaining an active GeoServer instance, the immediate takeaway from the summer security cycle is straightforward: administrators should update their environments to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6 without delay. These releases contain critical fixes designed to close security gaps that emerged during the busy summer months.
The GeoServer project maintains a strict coordinated vulnerability disclosure policy. Under this framework, vulnerabilities are identified, evaluated, and fixed across both stable and maintenance releases prior to any public disclosure of CVE details. The fundamental objective of this policy is to ensure that all users and system operators are given an adequate, equitable opportunity to apply necessary updates before malicious actors can weaponize the underlying flaws. However, maintaining this protective window relies entirely on the cooperation of researchers, third parties, and the broader open-source community.
The vulnerability landscape shifted dramatically in August when GeoServer confronted its first major zero-day vulnerability of the year—an active exploit in the wild for which no official patch had yet been publicly distributed. Prior to the public disclosure, the underlying flaw had already been reported privately to the project by several independent security researchers, and developers had already scheduled a comprehensive fix for inclusion in the upcoming GeoServer 3.0.1 release.
The zero-day crisis materialized because an unrelated third party, having no connection to the GeoServer project or to the original researchers who discovered the issue, disclosed the vulnerability publicly on social media channels. The consequences of this premature disclosure were immediate and severe. Automated vulnerability scans targeting the newly exposed flaw were detected within hours of the public social media post, triggering an urgent race to protect vulnerable installations across the globe.
The speed of the response from the development community and project leadership was remarkable. The incident quickly drew external media coverage and prompted urgent, high-visibility calls for action across official user forums and communication channels. Project leadership formally acknowledged the situation and extended their gratitude to security researcher Ravie Lakshmanan, who first notified project leadership through the Open Source Geospatial Foundation. The swift deployment of GeoServer 3.0.1, GeoServer 2.28.5, and GeoServer 2.27.6 mitigated the immediate threat, but the episode powerfully reaffirmed the vital importance of adhering to coordinated vulnerability disclosure protocols and emphasized why users must apply updates the moment they become available.
This summer’s security workload also encompassed a series of previously published CVEs that rolled out earlier in the season. On June 11, 2026, alongside the major release of GeoServer 3.0.0, the project published a set of related CVEs affecting earlier iterations of the software, requiring targeted updates for GeoServer versions 2.27.3, 2.26.4, and 2.27.0. These scheduled updates formed part of the project’s ongoing maintenance cycle, ensuring that users running different supported branches of the software remained protected against discovered weaknesses.
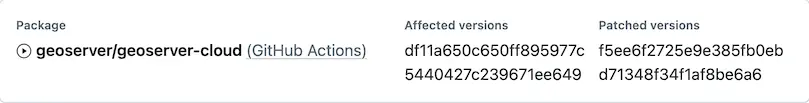
In addition to direct software vulnerabilities, the project navigated its first-ever infrastructure supply chain advisory during the review period. Supply chain advisories carry inherent risks because they have the potential to undermine the integrity of software downloaded by end users. Because this particular advisory did not correspond to an official release of GeoServer itself—and therefore did not meet the traditional criteria required to qualify for a CVE number—project maintainers specifically categorized the warning as a "geoserver/geoserver-cloud (GitHub Actions)" advisory.
Crucially, project leaders emphasized that no official GeoServer releases were compromised or affected by the supply chain incident. Standard GeoServer releases continue to be built using a dedicated Jenkins build server, with artifacts securely published to both SourceForge and official Open Source Geospatial Foundation infrastructure, keeping the core distribution pipeline secure and reliable for the user base.
The summer months also highlighted a broader industry trend that is increasingly impacting open-source maintainers: a surge in vulnerability reports generated with the assistance of artificial intelligence tools. Like many other prominent software development projects, the GeoServer team has experienced a steady wave of AI-assisted security submissions. In response to this influx, the project has established a general AI Policy and updated its comprehensive Security Policy to officially acknowledge the utilization of these tools and provide clear guidance for submitters.
Managing AI-generated vulnerability reports presents unique operational challenges for maintainers. These automated or AI-assisted reports are frequently very verbose, requiring significant manual effort to parse, evaluate, and determine whether a submission represents a genuine novel vulnerability or merely a duplicate of an existing ticket. Project maintainers noted that having reporters on hand to clarify ambiguities is deeply appreciated. Furthermore, because these reviews are time-consuming, assistance from community members who are positioned to test, verify, and validate fixes as they are developed helps lighten the load on the dedicated geoserver-security team.
For organizations whose core operations depend heavily on the stability and security of GeoServer, project leadership encourages active engagement and support. Organizations can contribute to the long-term sustainability of the platform by sponsoring the project financially or by allowing their internal staff to directly participate in geoserver-security operations and list discussions. Additionally, the project is actively working to establish formal project membership structures tailored specifically for public institutions and government agencies that often face regulatory or administrative restrictions regarding traditional corporate sponsorships and open-source participation.
Addressing questions regarding upgrade frequency, maintainers noted that GeoServer operates on a time-boxed release cycle that maintains both stable and maintenance release branches over the course of any given year. Administrators are strongly advised to upgrade their deployments to a supported release at least once a year to ensure continuous access to critical security patches and bug fixes. Comprehensive technical guidance for performing these updates is readily available in the official user documentation under the upgrading existing versions section.
Anyone discovering a potential security vulnerability within the platform is asked to follow the established protocols outlined in the project’s security policy, which instructs researchers and administrators on how to submit reports privately using GitHub security advisories rather than disclosing them prematurely in public forums.