
The GeoServer project has issued a comprehensive security recap detailing a turbulent summer of 2026, which featured a high-profile zero-day exploit, a series of Common Vulnerabilities and Exposures (CVEs), a notable supply chain advisory, and the growing challenge of managing AI-assisted security reports. Administrators and organizations responsible for running GeoServer instances are being urged to update their software immediately to mitigate active risks.
According to the project leadership, all users managing active instances should apply the latest patches without delay. Specifically, administrators are instructed to update their deployments to GeoServer version 3.0.1, version 2.28.5, or version 2.27.6 depending on their specific branch and maintenance cycle. These releases contain critical security fixes designed to protect spatial data infrastructures from exploitation.
The GeoServer development team strictly adheres to a coordinated vulnerability disclosure policy. Under this framework, security flaws are identified, investigated, and successfully patched across both stable and maintenance releases prior to any public disclosure of CVE details. The primary objective of this coordinated approach is to provide system administrators, enterprises, and public institutions with an adequate window of opportunity to apply necessary updates before malicious actors can weaponize the information. However, maintaining this protective buffer became challenging during the recent summer months due to unexpected external disclosures.
The August Zero-Day Incident
The most pressing security hurdle of the season occurred in August, when GeoServer was struck by a zero-day vulnerability—an active exploit occurring in the wild for which no official public fix had yet been deployed. Prior to this incident, the underlying security flaw had already been reported privately to the project through responsible channels by several independent researchers. A permanent fix had been scheduled for inclusion in the upcoming GeoServer 3.0.1 release, adhering to the project’s standard remediation timeline.
The zero-day crisis materialized when an unrelated third party, operating completely independently of both the core project team and the original reporting researchers, publicly disclosed the technical details of the vulnerability on social media. The fallout was swift and immediate. Automated scanning tools and malicious actors began probing for vulnerable instances within hours of the public social media post.
The rapid escalation triggered widespread news coverage and prompted an urgent call to action disseminated across the official user forum. Project leadership expressed gratitude to security researcher Ravie Lakshmanan, who first formally notified project leadership via the Open Source Geospatial Foundation, helping catalyze the rapid release cycle that followed. The prompt deployment of GeoServer 3.0.1, along with patches for maintenance lines 2.28.5 and 2.27.6, helped curb the potential impact of the exposure. Project organizers noted that this intense experience powerfully reaffirmed the critical importance of strictly following coordinated vulnerability disclosure policies and urged the global user base to prioritize applying patches the moment they are made available.
Previously Published CVEs and Release Cycles
The summer security recap also encompassed vulnerabilities addressed earlier in the season. On June 11, 2026, a series of CVEs were published simultaneously with the major milestone release of GeoServer 3.0.0. These vulnerabilities required subsequent maintenance efforts to secure older branches, including updates for GeoServer versions 2.27.3, 2.26.4, and specific component updates tied to version 2.27.0.
These events underscore the continuous nature of maintaining complex open-source geospatial software. GeoServer operates on a structured, time-boxed release cycle that spans a single calendar year, maintaining distinct "stable" and "maintenance" release lines to accommodate enterprise users who require stability alongside those who embrace cutting-edge features. Project documentation strongly recommends that organizations upgrade their deployed instances to a fully supported release at least once every twelve months to ensure continuous coverage against newly discovered security flaws.
Supply Chain Advisory and Infrastructure Integrity
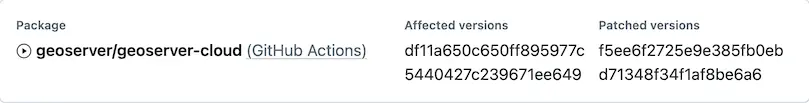
In addition to direct application vulnerabilities, the project encountered a distinct hurdle regarding supply chain integrity. For the first time in its history, the GeoServer project had to address and work through an infrastructure-level advisory. Because this particular advisory did not correspond to a direct release of the GeoServer application itself, it did not meet the traditional criteria required to receive a formal CVE number. Instead, the project categorized the advisory under "geoserver/geoserver-cloud (GitHub Actions)."
Project leaders emphasized a crucial distinction for concerned users: no official GeoServer software releases were compromised or affected by this supply chain event. Standard GeoServer releases are compiled and published through a dedicated Jenkins build server, which securely distributes official artifacts to both SourceForge and the core OSGeo infrastructure. The cloud-based advisory served as a reminder of the complex web of third-party actions and automated workflows involved in modern software delivery pipelines, prompting heightened scrutiny of internal build environments and CI/CD pipelines.
Managing the Wave of AI-Assisted Vulnerability Reports
Another prominent theme highlighted in the summer security review is the modern proliferation of AI-assisted vulnerability reports. Like many prominent open-source software projects, the GeoServer maintainers have observed a substantial surge in vulnerability submissions generated, expanded, or heavily structured using artificial intelligence tools.
To address this shifting landscape, the project has established a dedicated general AI policy and updated its core GitHub security policy. These framework updates acknowledge the reality of automated tool usage and provide clear guidance for researchers utilizing AI assistance. While these technologies can sometimes help surface potential areas for review, they frequently result in exceptionally verbose submissions that require significant human effort to analyze.
Project maintainers noted that reviewing these AI-generated reports consumes considerable time, particularly when determining whether a submission represents a genuine novel vulnerability or merely an overly verbose duplicate of a known issue. Furthermore, because AI tools can occasionally misinterpret codebase contexts, having reporters available to clarify findings, test assumptions, and verify proposed fixes is considered immensely helpful. Alleviating the burden on the dedicated geoserver-security team remains a priority for the community.
Community Support and Engagement
As the project navigates these evolving technical and security landscapes, leadership continues to emphasize the importance of community collaboration. Organizations and enterprises that rely heavily on GeoServer for critical spatial data infrastructure are encouraged to support the project financially through sponsorship programs or by allowing their internal technical staff to participate directly in the geoserver-security working groups.
Additionally, the project is actively working to establish formal project membership pathways for public institutions and governmental agencies that often face rigid institutional restrictions regarding direct financial sponsorship or external participation. Through sustained collaboration, timely upgrading habits, and adherence to responsible disclosure practices, the GeoServer community aims to maintain the security and resilience of its widely used geospatial platform.




