
The GeoServer project has issued a comprehensive security recap detailing a tumultuous summer of 2026 marked by coordinated vulnerability disclosures, a high-profile zero-day exploit, a supply chain infrastructure advisory, and an influx of automated AI-generated vulnerability reports. Administrators maintaining GeoServer instances are being strongly urged to update their software immediately to the newly released versions—GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6—to safeguard their systems against active exploitation.
The open-source geospatial project operates under a strict coordinated vulnerability disclosure policy. Under this framework, security issues are traditionally addressed and fixed across both stable and maintenance release branches before any Common Vulnerabilities and Exposures (CVE) details are publicly disseminated. The primary objective of this coordinated approach is to provide all system administrators and organizations with a reliable window of opportunity to apply necessary updates before malicious actors can weaponize the flaws. However, maintaining this protective buffer proved challenging over the recent summer months due to unforeseen external disclosures and shifting industry landscapes.
August Zero-Day Vulnerability and Early Exploitation
The most critical security incident of the period occurred in August, when GeoServer was confronted with an active zero-day vulnerability—a severe flaw being exploited in the wild before an official patch could be widely deployed. Prior to the public leak, the underlying security problem had already been identified and reported privately by several independent security researchers. Project maintainers had scheduled a comprehensive fix to be rolled out as part of the upcoming GeoServer 3.0.1 release.
The situation escalated rapidly when a third party, entirely unconnected to either the core project development team or the original researchers who discovered the issue, disclosed the vulnerability details publicly on social media. The fallout was immediate and severe. Automated security scans and exploitation attempts targeting the unpatched vulnerability were detected within mere hours of the public social media post.
The extraordinary speed at which malicious actors mobilized underscored the volatile nature of modern vulnerability management. The incident quickly drew external media coverage and prompted project leadership to issue an urgent call for updates across the official user forum. Project leadership formally acknowledged the assistance of security researcher Ravie Lakshmanan, who first notified project leadership regarding the active exploitation via the Open Source Geospatial Foundation.
To mitigate the zero-day threat, administrators must upgrade immediately to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6. Project representatives noted that this intense ordeal strongly reaffirms the critical importance of strictly adhering to coordinated vulnerability disclosure practices and emphasized that users must remain vigilant about applying patches the moment they are made available.
Previously Published CVEs and Release Cycles
The summer security recap also highlights a series of vulnerabilities previously disclosed on June 11, 2026, which coincided with the major rollout of the GeoServer 3.0.0 release. Those earlier advisories addressed multiple security deficiencies across older legacy and active branches, including specialized fixes designated for GeoServer versions 2.27.3, 2.26.4, and the initial 2.27.0 release.
GeoServer maintains a structured, time-boxed release cycle that spans a full calendar year, dividing development and support efforts between designated "stable" and "maintenance" branches. Project maintainers strongly advise organizations to establish a regular upgrade cadence, recommending that system administrators update their deployments to a supported release at least once every year to ensure they continuously receive critical security backports and bug fixes. Comprehensive technical guidance for performing these upgrades is readily available through the official GeoServer user guide and installation documentation.
Supply Chain Advisory and Infrastructure Security
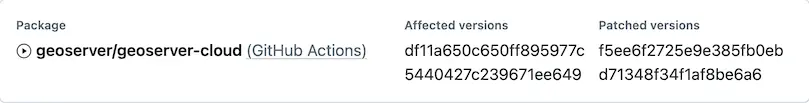
In addition to traditional software vulnerabilities, the GeoServer project faced a distinct supply chain advisory during the summer review period. This marked the first time the project has had to manage an infrastructure-level security advisory of this nature. Because the advisory specifically pertained to the "geoserver/geoserver-cloud" configuration utilizing GitHub Actions rather than a direct software source release of GeoServer itself, it did not qualify for a traditional CVE tracking number.
Project maintainers emphasized a crucial distinction for users concerned about software integrity: no official GeoServer software releases were affected by this supply chain incident. Authentic GeoServer releases are strictly compiled and published using an isolated Jenkins build server, which subsequently pushes official build artifacts to trusted repositories on both SourceForge and the Open Source Geospatial Foundation (OSGeo) infrastructure. The advisory served as a reminder of the complex dependencies inherent in modern continuous integration pipelines and the vigilance required to secure developer toolchains.
Managing AI-Assisted Vulnerability Reports
Like numerous other prominent open-source software initiatives, the GeoServer project has experienced a significant surge in security vulnerability reports generated with the assistance of artificial intelligence tools. These AI-generated submissions often present unique administrative challenges because they tend to be exceptionally verbose, frequently obscure genuine security risks within mountains of automated text, and regularly result in a high volume of duplicate submissions.
In response to this administrative burden, the project has established a dedicated general AI policy and updated its core security policy on GitHub. These policy updates are designed to formally acknowledge the utilization of automated tools by security researchers and provide clear guidelines on what the project expects from submitters. Maintainers have noted that human researchers who are willing to remain on hand to clarify complex reports, assist in determining if a submission is a duplicate, and actively test and verify proposed fixes provide invaluable assistance to the overburdened security team.
Community Support and Collaboration
Securing a widely deployed enterprise open-source project requires substantial technical resources and community collaboration. The GeoServer project relies heavily on the dedication of its core developers and security contributors, but the increasing frequency of zero-day threats, complex supply chain considerations, and high-volume AI-generated reports have placed additional strains on available capacity.
Organizations and enterprises that rely heavily on GeoServer for their critical geospatial data infrastructure are being encouraged to support the project’s ongoing sustainability. Stakeholders can contribute by becoming official project sponsors or by embedding staff directly into the geoserver-security working group to share the operational workload. Furthermore, the project is actively working to establish formal project membership pathways specifically tailored for public institutions and government agencies that frequently face administrative or legal restrictions regarding corporate sponsorship and direct open-source participation.
For individuals or organizations seeking to report a newly discovered security vulnerability responsibly, the GeoServer project maintains clear instructions within its official security policy. Security researchers are strongly urged to utilize private reporting channels via GitHub security advisories to ensure vulnerabilities are thoroughly patched and verified before any public disclosure can be leveraged by malicious actors.




