The open-source geospatial community is reckoning with a turbulent summer of security challenges following a wave of vulnerability advisories, a high-profile zero-day exploit, and an evolving landscape shaped by automated threat reporting. Project maintainers for GeoServer have issued an urgent call to action for system administrators worldwide, strongly urging them to apply the latest security updates immediately to protect critical mapping infrastructure.
The core message for anyone responsible for managing a GeoServer instance is direct and unambiguous: administrators must update their systems to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6 without delay. These new releases contain essential patches designed to address vulnerabilities discovered over the past several months, closing critical security gaps that could otherwise expose mapping servers to malicious actors.
The GeoServer project has long adhered to a strict coordinated vulnerability disclosure policy. Under this framework, security flaws are thoroughly investigated and fixed for both stable and maintenance release lines before any Common Vulnerabilities and Exposures (CVE) details are made public. The primary objective of this coordinated approach is to give system administrators, organizations, and infrastructure operators a vital window of opportunity to update their software and secure their environments prior to public disclosure, thereby minimizing the risk of widespread exploitation.
August Zero-Day
That careful cadence of coordinated disclosure was severely tested in August, when GeoServer experienced a zero-day vulnerability—an active exploit in the wild with no known official fix at the time of discovery. Prior to the public leak, the underlying security problem had already been reported privately by several independent security researchers, and a formal patch had been carefully scheduled for inclusion in the upcoming GeoServer 3.0.1 release.
The dangerous zero-day situation arose when an unconnected third party, operating entirely outside the project and independent of the original reporting researchers, publicly disclosed the vulnerability details on social media. The fallout was immediate and severe. Automated threat intelligence and network traffic monitors detected widespread scans probing for this specific vulnerability within mere hours of the public social media post.
The startling speed of the threat landscape’s response generated rapid news coverage and forced project maintainers to issue an emergency call for updates across user forums and mailing lists. Project leadership extended their gratitude to reporter Ravie Lakshmanan, who first notified project leadership via the Open Source Geospatial Foundation, helping trigger the rapid mobilization.
The rapid deployment of GeoServer 3.0.1, alongside maintenance updates 2.28.5 and 2.27.6, helped stabilize the ecosystem. However, this harrowing experience vividly reaffirmed the critical importance of strictly following coordinated vulnerability disclosure policies and the necessity for the user community to apply patches the moment they become available.
Previously Published CVEs
The summer security review also encompasses a series of vulnerabilities previously brought to light earlier in the season. On June 11, 2026, alongside the major launch of the GeoServer 3.0.0 release, project maintainers published a comprehensive batch of CVEs affecting various legacy and transitional versions. These updates required coordinated efforts across multiple supported branches, notably requiring immediate attention for instances running GeoServer 2.27.3, 2.26.4, and the foundational 2.27.0 release.
Managing multiple active release branches simultaneously remains a significant logistical undertaking for the open-source project, highlighting the ongoing resource commitments required to maintain enterprise-grade security standards across the global geographic information systems landscape.
Supply Chain Advisory
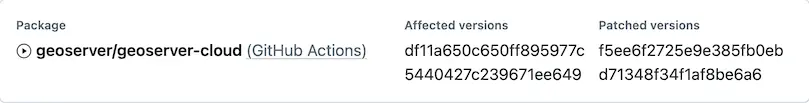
Beyond direct software vulnerabilities, the project recently navigated its first-ever infrastructure supply chain advisory. Supply chain advisories carry the inherent potential to undermine the integrity of the software packages downloaded by end users, making them a top priority for project maintainers and security teams alike.
In this instance, the advisory was specifically categorized under the identifier "geoserver/geoserver-cloud (GitHub Actions)" because it did not correspond directly to a standard GeoServer software release. Consequently, the incident did not qualify for a traditional CVE number. Project leadership was quick to emphasize a vital point for concerned users: absolutely no official GeoServer releases were affected by the supply chain incident. Standard GeoServer releases continue to be built using a dedicated Jenkins build server that publishes finalized artifacts securely to both SourceForge and official Open Source Geospatial Foundation (OSGeo) infrastructure.
AI-Assisted Vulnerability Reports
Like many other prominent open-source software projects, the GeoServer maintainers are currently experiencing an unprecedented wave of security vulnerability reports generated with the assistance of artificial intelligence tools. While AI can aid in security research, the sheer volume and verbosity of these automated submissions have created significant operational hurdles.
In response to this shifting paradigm, the project has established a general AI Policy and updated its comprehensive Security Policy. These updated guidelines explicitly acknowledge the growing prevalence of AI-generated tools in vulnerability research and provide clear instructions for researchers utilizing them.
Handling AI-assisted reports demands considerable time from the security team, particularly because these submissions are frequently overly verbose, difficult to review, and often turn out to be duplicates of previously known issues. Project maintainers have noted that security researchers submitting AI-assisted findings can greatly assist the team by remaining available to clarify complex descriptions, test proposed patches, and verify fixes as vulnerabilities are actively addressed. Any collaborative effort that reduces the administrative and analytical burden on the geoserver-security team helps accelerate the delivery of safe, stable software.
Community Support and Participation
As the demands on open-source maintainers continue to grow, the GeoServer project increasingly relies on active community involvement to sustain its operations. Organizations and enterprises whose critical infrastructure depends on GeoServer are strongly encouraged to consider financial sponsorship or to allow their staff members to participate directly in the ongoing work of the geoserver-security team.
Furthermore, the project is actively working to establish formal project membership pathways specifically tailored for public institutions and government agencies that often face rigid institutional restrictions regarding direct commercial sponsorship and open-source project participation.
Upgrade Cadence and Best Practices
GeoServer operates on a structured, time-boxed release cycle, systematically maintaining both "stable" and "maintenance" release lines over the course of each year. To maintain robust operational security, organizations are strongly advised to upgrade their deployments to a supported release at least once every twelve months to ensure continuous access to critical security patches and bug fixes. Comprehensive upgrade instructions are maintained within the official user guide documentation to assist administrators through the transition processes.
For security researchers and system administrators seeking to report newly discovered vulnerabilities privately, the GeoServer project maintains a formal security policy outlining secure communication channels via GitHub security advisories, ensuring responsible disclosure standards are upheld across the ecosystem.