
The GeoServer development team has released a comprehensive security recap detailing a turbulent summer of 2026, highlighted by a high-profile zero-day vulnerability, multiple Common Vulnerability and Exposures (CVE) disclosures, a significant supply chain advisory, and the formal updating of the project’s security policies to address the growing influx of AI-assisted vulnerability reports.
Administrators and organizations responsible for managing GeoServer instances are being urged to take immediate action. The project team has strongly recommended that all users upgrade their systems without delay to the newly patched versions: GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6. These urgent releases have been pushed out to address critical security flaws that threaten the integrity and safety of spatial data infrastructure worldwide.
The GeoServer project maintains a strict coordinated vulnerability disclosure policy. Under this framework, security flaws are thoroughly investigated, verified, and fixed across both stable and maintenance release branches before any CVE details or technical specifics are made public. The fundamental objective of this policy is to ensure that system administrators and organizations have a fair and adequate window of opportunity to apply necessary updates and patch their systems prior to public awareness and potential exploitation by malicious actors.
However, this careful orchestration was severely tested in August 2026 when GeoServer encountered a critical zero-day vulnerability. A zero-day exploit refers to a security flaw that is actively being exploited in the wild before an official fix has been publicly rolled out. In this particular instance, the underlying technical problem had already been responsibly reported in private by several independent security researchers, and a formal fix was already actively scheduled for inclusion in the upcoming GeoServer 3.0.1 release.
The volatile zero-day situation unfolded when a third party, entirely unconnected to either the core GeoServer project or the original researchers who discovered the issue, chose to disclose the vulnerability publicly on social media channels. The fallout was swift and immediate. Automated scanners and malicious actors began actively probing for the vulnerability within hours of the public social media post going live.
The incredible speed of this malicious response triggered widespread concern, prompting immediate news coverage and urgent warnings broadcast across the official GeoServer user forum. Project leadership expressed deep gratitude to reporter Ravie Lakshmanan for first notifying project leadership via the Open Source Geospatial Foundation, helping bring visibility to the rapid unfolding of events. This stressful real-world episode dramatically reaffirmed the critical importance of adhering strictly to coordinated vulnerability disclosure policies and underscored why user communities must act swiftly when new patched releases are made available.
In addition to the August zero-day crisis, the summer of 2026 saw several other security milestones. Earlier in the season, on June 11, 2026, a series of CVEs were officially published in tandem with the major GeoServer 3.0.0 release. These affected earlier branches, necessitating subsequent maintenance releases like GeoServer 2.27.3, 2.26.4, and 2.27.0 to ensure that organizations running older stable lines were not left exposed to known attack vectors.
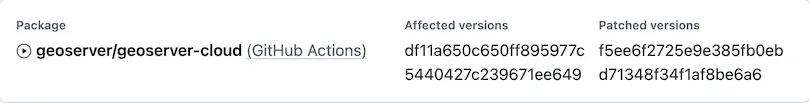
The project also confronted its first-ever infrastructure supply chain advisory over the summer. Supply chain advisories carry the inherent potential to impact the integrity of software downloads by calling into question the build pipeline or repository infrastructure. Because this particular advisory was categorized specifically under GitHub Actions for the geoserver/geoserver-cloud repository rather than corresponding to an official core release of GeoServer, it did not meet the formal criteria required to receive a CVE identifier.
Project maintainers emphasized strongly that no official GeoServer releases were compromised or affected by this supply chain event. Standard GeoServer releases are compiled and published using a secure Jenkins build server that distributes artifacts directly to SourceForge and trusted OSGeo infrastructure, maintaining a strict firewall between cloud experimental environments and production release channels.
As the open-source community continues to grapple with shifting technological landscapes, GeoServer has also had to adapt to changing dynamics in security reporting. Like many other prominent open-source software projects, the GeoServer security team has experienced a massive wave of vulnerability reports generated with the assistance of artificial intelligence. These AI-generated reports often present unique challenges for maintainers, as they frequently arrive in high volumes and are exceptionally verbose, requiring significant manual effort to parse, analyze, and determine whether they represent genuine threats or are merely redundant duplicates.
To address this modern phenomenon head-on, the project has established a general AI Policy and updated its core GitHub Security Policy. These updated guidelines explicitly acknowledge the growing usage of AI-assisted security tools and provide clear guidance to researchers on how to submit findings responsibly. Maintainers noted that when researchers utilize AI tools to generate reports, being readily available on hand to clarify technical details and assist in testing and verifying fixes is deeply appreciated. Collaborative efforts from the community to reduce the heavy workload carried by the volunteer-driven geoserver-security team remain vital to keeping the software secure and sustainable.
Sustaining a complex geospatial project requires robust community backing. Organizations and enterprises whose core operations depend heavily on GeoServer are encouraged to consider financial sponsorship or to allow their internal technical staff to directly participate in the ongoing work of the geoserver-security group. Furthermore, the project is actively working to establish formal project membership pathways specifically tailored for public institutions and government agencies that often face strict institutional restrictions regarding financial sponsorship and open-source participation.
For general maintenance, GeoServer operates under a predictable time-boxed release cycle, steadily maintaining both stable and maintenance release lines throughout the annual calendar. System administrators are strongly advised to upgrade their deployed GeoServer instances to a supported, patched release at least once a year to ensure continuous receipt of vital security patches and bug fixes. Comprehensive documentation, upgrade paths, and technical instructions are readily accessible via the official GeoServer User Guide and installation manuals.
Anyone discovering a potential security vulnerability within the platform is requested to follow the responsible disclosure guidelines outlined in the project’s security policy, utilizing private channels via GitHub security advisories rather than resorting to premature public exposure.




