The GeoServer development team has released a comprehensive security recap detailing a turbulent summer of 2026, which included managing a critical zero-day vulnerability, addressing previously published Common Vulnerabilities and Exposures (CVEs), navigating a supply chain advisory, and adapting to an influx of AI-assisted security reports.
Administrators and organizations responsible for managing GeoServer instances are being strongly advised to apply the latest security patches immediately. The project has made patched versions available, instructing users to update their systems to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6 depending on their specific deployment branch.
Throughout its operations, the GeoServer project strictly adheres to a coordinated vulnerability disclosure policy. Under this framework, security flaws are thoroughly investigated, and fixes are developed and applied to both stable and maintenance releases prior to any public CVE details being published. The primary objective of this coordinated approach is to provide all system administrators and organizations with an adequate window of opportunity to update their software before malicious actors become aware of the vulnerabilities and begin crafting exploits.
The August Zero-Day Event
The stability of the release cycle faced a significant test in August when GeoServer encountered a zero-day vulnerability—an active exploit functioning in the wild with no official fix deployed at the time of discovery. Prior to the public exposure, the underlying problem had already been identified and reported privately by several independent researchers. A permanent fix had been scheduled for inclusion in the upcoming GeoServer 3.0.1 release.
However, the security landscape shifted rapidly when an unconnected third party—independent of both the project leadership and the researchers who originally flagged the issue—chose to disclose the vulnerability publicly on social media. The consequences of this premature disclosure were immediate. Automated scanning tools and threat actors began actively probing for the vulnerability within hours of the social media post going live.
The speed with which the vulnerability was targeted in the wild triggered emergency news coverage and prompted urgent warnings across the project’s user forums. Project leadership expressed gratitude to security researcher Ravie Lakshmanan, who first notified the leadership team via the Open Source Geospatial Foundation. The swift turnaround required to push out GeoServer 3.0.1, GeoServer 2.28.5, and GeoServer 2.27.6 underscored the immense pressure placed on open-source maintainers when coordinated disclosure timelines are disrupted. Project organizers noted that this intense experience powerfully reaffirms the necessity of respecting coordinated vulnerability disclosure policies and highlights why users must act quickly when patches are finally published.
Previously Published CVEs and Release Tracking
The summer security updates also encompassed vulnerabilities identified earlier in the season. On June 11, 2026, alongside the major release of GeoServer 3.0.0, the project published a series of CVEs affecting older branches, requiring prompt maintenance attention for versions such as GeoServer 2.27.3, 226.4, and 2.27.0.
These continuous security updates are a natural product of GeoServer’s structured, time-boxed release cycle. The project routinely maintains both stable and maintenance release branches over the course of a calendar year. Because software security is an evolving discipline, project maintainers strongly recommend that organizations upgrade their GeoServer installations to a supported release at least once every year to ensure they continue receiving critical security patches and infrastructure improvements. Comprehensive upgrade guidance is maintained within the official user installation documentation to assist administrators with the transition process.
Supply Chain Advisory and Infrastructure Integrity
In addition to software-specific vulnerabilities, the project recently confronted its first-ever infrastructure supply chain advisory. Because supply chain issues have the potential to compromise the integrity of downloaded software artifacts, the project treated the situation with extreme urgency.
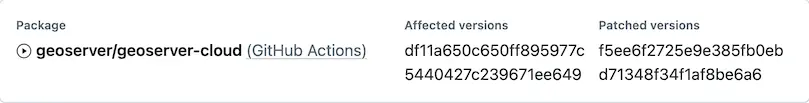
The advisory was formally cataloged under the designation "geoserver/geoserver-cloud (GitHub Actions)." Project maintainers clarified that this specific advisory did not correspond with an official release of the core GeoServer software, and consequently, it did not qualify for a traditional CVE number. Most importantly, the project confirmed that no official GeoServer releases were impacted by the supply chain incident. Standard GeoServer releases continue to be securely generated using a dedicated Jenkins build server, which subsequently publishes verified artifacts to both SourceForge and official OSGeo infrastructure repositories.
Managing AI-Assisted Vulnerability Reports
Like many other prominent open-source software projects in recent months, GeoServer has experienced a noticeable surge in vulnerability reports generated with the assistance of artificial intelligence tools. While these tools aim to improve security research, they frequently generate large volumes of verbose, repetitive, or duplicate submissions that require significant manual triage by the core development team.
To address this modern challenge, the project has established a formal AI Policy and updated its broader Security Policy on GitHub. These policy documents are designed to formally acknowledge the use of AI tools in vulnerability discovery and provide clear guidance for researchers utilizing them. Maintainers have emphasized that when submitting AI-assisted reports—which are often exceptionally wordy—having researchers on hand to clarify technical details, test proposed solutions, and verify fixes is deeply appreciated.
Reviewing these automated reports consumes substantial developer time, particularly when determining whether a submission duplicates an existing bug. Project leaders noted that any assistance from the community in testing, verifying, and easing the administrative burden on the geoserver-security team directly contributes to the overall stability and safety of the ecosystem.
Community Participation and Support
Securing a complex open-source mapping platform like GeoServer requires sustained collaboration between developers, maintainers, and the organizations that rely upon the technology for critical geospatial infrastructure. The project continually encourages organizations dependent on GeoServer to consider financial sponsorship or to allow their internal technical staff to participate directly in the geoserver-security working group.
Furthermore, to accommodate public institutions and government agencies that frequently face administrative or legal restrictions regarding direct corporate sponsorship and participation, the project is actively working to establish structured project membership options through initiatives such as GSIP-243.
For security researchers and system administrators seeking to report newly discovered vulnerabilities responsibly, the project maintains strict guidelines. All potential security issues should be reported privately using the designated GitHub security advisories framework outlined in the official GeoServer security policy, ensuring that patches can be properly developed and tested before public disclosure occurs.