
The GeoServer open-source project has released a comprehensive security recap detailing a turbulent summer of 2026 marked by critical vulnerability disclosures, a high-profile zero-day exploit, a supply chain advisory, and an influx of AI-generated security reports. Project maintainers are strongly urging all administrators and organizations managing GeoServer instances to apply the latest security patches immediately to protect their geospatial data infrastructure.
According to the official advisory, users are required to update their deployments to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6 depending on their active branch. These critical releases bundle vital security patches designed to protect servers from actively exploited flaws and previously cataloged vulnerabilities.
The GeoServer development team strictly adheres to a coordinated vulnerability disclosure policy. Under this framework, security issues are thoroughly investigated, and fixes are developed and tested for both stable and maintenance releases prior to the public publication of Common Vulnerabilities and Exposures (CVE) details. The primary objective of this coordinated approach is to give system administrators, enterprises, and public institutions adequate time to apply updates before malicious actors can weaponize the underlying security flaws.
However, the summer of 2026 tested the limits of this coordinated model, most notably during an August zero-day incident. GeoServer encountered an aggressive zero-day vulnerability, representing an actively exploited security flaw in the wild for which no official project fix had yet been publicly deployed. The underlying technical problem had already been privately reported to the core development team by several independent security researchers, and a formal patch had been scheduled for inclusion in the upcoming GeoServer 3.0.1 release.
The zero-day crisis escalated rapidly when an unrelated third party publicly disclosed the vulnerability details on social media. The fallout was immediate and severe. Automated security scanners and threat actors began probing public-facing networks for the vulnerability within hours of the social media post going live. The extraordinary speed with which the exploit attempts materialized prompted immediate media coverage and an urgent broadcast warning disseminated across the official OSGeo user forum. Project leadership formally acknowledged the swift reporting efforts of security researcher Ravie Lakshmanan, who first notified project leadership via the Open Source Geospatial Foundation, helping trigger the emergency response.
This dramatic incident forcefully reaffirmed the critical necessity of adhering strictly to coordinated vulnerability disclosure policies. Project maintainers reiterated that when new patched versions are made available, administrators must prioritize rapid deployment rather than waiting for scheduled maintenance windows, especially when vulnerabilities become public knowledge.
The summer security recap also reviewed a series of previously published CVEs that had rolled out earlier in the season. On June 11, 2026, alongside the major release of GeoServer 3.0.0, developers published multiple CVE entries addressing various underlying software weaknesses across older maintenance and development branches, including GeoServer 2.27.3, 2.26.4, and the initial 2.27.0 release. These historical patches laid the groundwork for the modern architectural improvements found in the 3.0 series, but they also underscored the ongoing challenge of maintaining large, complex Java-based geospatial software stacks.
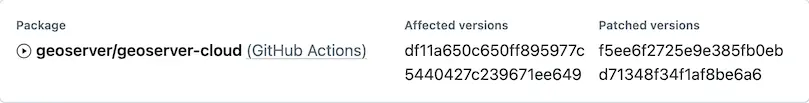
Adding to the complexity of the summer update cycle, the GeoServer project faced its first-ever infrastructure supply chain advisory. Supply chain security advisories inherently carry the potential to undermine the cryptographic and operational integrity of software packages downloaded by end users. In this specific instance, the advisory was officially categorized under the label for the GeoServer Cloud GitHub Actions environment because the incident did not correspond directly to a standard source release of GeoServer. Consequently, the supply chain event did not qualify for a traditional CVE number.
Crucially, project leadership emphasized that no official GeoServer software releases were compromised or affected by this infrastructure event. Standard GeoServer releases continue to be compiled securely using an isolated Jenkins build server that publishes verified software artifacts directly to SourceForge and trusted OSGeo infrastructure repositories, maintaining a strict barrier between development automation pipelines and official distribution channels.
Beyond traditional software bugs and infrastructure warnings, the GeoServer project has reported a noticeable surge in vulnerability reports generated with the assistance of artificial intelligence. Like many other major open-source software communities, the GeoServer security team has experienced a steady wave of verbose, AI-assisted security submissions. These automated or semi-automated reports often present significant review challenges, requiring substantial manual effort to analyze, verify, filter out false positives, and identify duplicate submissions.
To address this modern shift in vulnerability reporting, project maintainers have established a general AI policy alongside a comprehensive update to the official GeoServer security policy. These updated guidelines explicitly acknowledge the integration of AI tools in security research and provide clear instructions for researchers utilizing them. The project has stressed that when submitting AI-generated reports, having researchers on hand to clarify technical details, test proposed fixes, and assist with verification is invaluable. Community collaboration helps alleviate the heavy workload shouldered by the dedicated geoserver-security team, ensuring that genuine threats are addressed efficiently without burning out maintainers.
As the project navigates these multifaceted security challenges, maintainers have outlined several ways for organizations and individual developers to contribute to the long-term health and safety of the ecosystem. Organizations whose core operational capabilities depend heavily on GeoServer are encouraged to consider formal project sponsorship or to authorize their internal engineering staff to participate directly in the geoserver-security working group. Furthermore, the project is actively working to establish formal project membership pathways for public institutions and government agencies that frequently face administrative or legal restrictions regarding financial sponsorship and direct community participation.
Addressing common maintenance questions, project leaders emphasized the importance of adhering to the structured release cycle. GeoServer operates on a time-boxed release schedule throughout the year, actively maintaining both stable and maintenance release lines. Administrators are strongly advised to upgrade their operational GeoServer deployments to a supported, patched release at least once a year to ensure continuous receipt of vital security fixes and performance improvements. Detailed upgrading instructions and migration paths are documented thoroughly within the official GeoServer User Guide to assist system administrators through the transition processes.
Organizations or security researchers who discover new, undisclosed security vulnerabilities within GeoServer are reminded to follow the established private reporting protocol outlined in the project’s security policy, utilizing GitHub security advisories to ensure responsible disclosure before any public discussion or patching takes place.




