Federal Bureau of Investigation (FBI) agents have arrested a high-profile executive at a Canadian cybersecurity firm in Pennsylvania, marking a dramatic escalation in the ongoing, high-stakes international investigation into the notorious "ShinyHunters" hacking syndicate. The arrest comes on the heels of a massive and deeply embarrassing cyberattack by the group that compromised sensitive internal records belonging to thousands of federal law enforcement agents.
Multiple sources familiar with the matter confirmed the arrest to KrebsOnSecurity, noting that the suspect was taken into federal custody earlier this week. The operation ties directly into a sprawling multi-jurisdictional crackdown on cybercrime actors and ransomware negotiators, a probe that has recently seen federal authorities centralize command and control operations at an FBI field office in Texas.
The New York Times first reported the arrest of the Canadian man in Pennsylvania on suspicion of providing assistance to ShinyHunters. However, the initial Times report and a brief statement posted to the social media platform X by FBI Director Kash Patel did not publicly identify the individual in custody.
A Cyber Risk Summit and Corporate Connections
According to sources close to the unfolding investigation, the Canadian executive had traveled to Pennsylvania to attend a prominent industry event: the Cyber Risk Summit, which was held at the Loews Philadelphia Hotel. Publicly available records, including speaker and sponsor lists for the event, indicate that the conference took place between October 5 and October 7.
While the annual event drew numerous sponsors from across the risk management and cybersecurity sectors, the summit’s website listed a Canadian security firm known as Cypfer as its primary and largest sponsor.
Background searches and corporate footprints on professional networking platforms like LinkedIn reveal further ties to the event. One of Cypfer’s prominent former leaders, Edward Dubrovsky, had recently transitioned to another Canadian security firm and conference sponsor called CyberSteward. Approximately one month prior to the summit, Dubrovsky published a post on LinkedIn announcing his plans to attend the Cyber Risk Summit alongside members of the CyberSteward team.
In the wake of the news, a spokesperson for Cypfer clarified that Dubrovsky’s LinkedIn profile mischaracterized his historical role with the company, noting that he was never a founder or co-founder, but rather served as a managing director prior to resigning from the firm in November 2025.

Prior to his arrest, Dubrovsky had publicly championed his ongoing work in the sector, writing on social media that he looked forward to continuing industry discussions regarding "strategy & compliant driven coercive (ransomware, extortion) advisory, negotiations and settlement services that are global and truly agnostic."
Court Documents and Federal Charges
Federal court records reveal that an individual named Edward Dobrovsky—with a slight spelling variation in the surname—was taken into custody in Pennsylvania on October 8. He faces serious federal charges, including cyber extortion and conspiracy.
While several key documents in the docket, including the core criminal complaint, remain under seal, a handful of filings have been indexed on public legal databases such as CourtListener. A summary of the complaint shows that the defendant is formally charged with "conspiracy to threaten to impair the confidentiality of information with the intent to extort money," alongside a charge of "interference with commerce by threats."
Inmate locator records maintained by the U.S. Bureau of Prisons indicate that a 54-year-old Edward Dubrovsky is currently being housed at a federal detention facility in Philadelphia. However, court docket entries show that a legal notice was filed on October 9 to transfer the case to the U.S. District Court for the Eastern District of Texas. Legal sources indicate that this district has become the primary nerve center and epicenter for the federal government’s comprehensive investigation into ShinyHunters.
The FBI has consistently declined to comment on the specifics of the ongoing investigation or the pending charges.
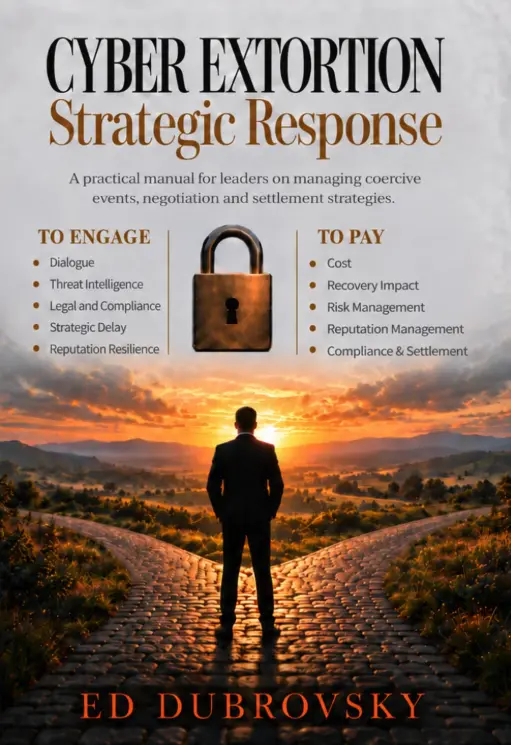
Beyond his executive and corporate advisory roles in the Canadian cybersecurity market, Dubrovsky is also known within professional circles as an author. His 252-page book, Cyber Extortion Strategic Response, focuses heavily on the complex mechanics of corporate ransomware negotiations.
An excerpt from the book’s publisher summary highlights a foundational philosophy in modern incident response: "At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."

At the time of reporting, Dubrovsky could not be reached directly for comment, and representatives from CyberSteward had not yet issued public statements regarding the arrest. Available court records indicate that the defendant has not yet retained private legal counsel, nor has a public defender been formally appointed by the court.
The Broader ShinyHunters Threat Landscape
The arrest highlights the relentless pressure federal law enforcement agencies are applying to dismantle the infrastructure behind ShinyHunters. The cybercriminal syndicate has established a reputation for infiltrating software-as-a-service companies through sophisticated phishing campaigns and the use of stolen credentials. Once inside corporate environments, the group siphons vast troves of proprietary data, leveraging the threat of public exposure to exact multi-million-dollar extortion payments.
According to internal estimates and federal tracking, ShinyHunters has successfully extorted more than $70 million from corporate and institutional victims over the course of the year.
The current wave of law enforcement actions traces back through a series of recent international busts. Last month, Dutch police apprehended Pepijn van der Stap, a reformed hacker suspected of playing a major role in the enterprise, prompting federal investigators to scour electronic devices and digital evidence seized during the arrest. Sources indicate that additional criminal charges against principals at other specialized ransomware negotiation and advisory firms could be forthcoming as the probe widens.
The pressure on the hacking collective intensified dramatically immediately following Van der Stap’s arrest. An operative within the group using the online handle "Rey" stepped into a leadership vacuum, aggressively assuming control of ShinyHunters and launching a public taunt campaign against federal authorities. The taunts stemmed from a brazen breach that compromised sensitive data from the FBI’s own online recruitment portal, exposing internal details including individual agent unit assignments, specialized skills, and confidential medical and psychiatric records.
Investigative reporting from Reuters revealed that the individual operating as Rey was a teenager named Saif Al-din Khader. Law enforcement authorities subsequently detained Khader, who has reportedly begun cooperating with federal investigators. Early October reporting detailed how Rey was tracked down and apprehended as the collective allegedly attempted an extortion scheme against a digital aviation and navigation unit that had been divested by Boeing in late 2025.
As the investigation continues to develop at a rapid pace, federal authorities are maintaining a tight grip on emerging details regarding the full scope of the conspiracy.