
The GeoServer open-source project has issued a comprehensive security recap detailing a tumultuous summer of 2026. The update covers critical patches for recently discovered Common Vulnerabilities and Exposures (CVEs), a supply chain advisory, and the growing operational impact of AI-assisted vulnerability reporting. Most urgently, the project is urging all administrators overseeing GeoServer instances to apply the newly released updates immediately by upgrading to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6.
For years, the GeoServer project has maintained a strict coordinated vulnerability disclosure policy. Under this framework, security flaws are patched simultaneously across both stable and maintenance release lines before any technical CVE details are made public. The fundamental objective of this policy is to grant system administrators, enterprise users, and public institutions a fair window of opportunity to secure their infrastructure prior to malicious actors learning about the specifics of a vulnerability. However, maintaining this balance became exceptionally challenging over the course of the summer months, highlighted by a dramatic zero-day incident in August that tested the project’s incident response capabilities.
The August Zero-Day Incident
In August 2026, the GeoServer ecosystem encountered a high-pressure zero-day vulnerability—a security flaw that was actively being exploited in the wild before an official fix could be widely deployed. Prior to the public disclosure, the underlying problem had already been responsibly identified and reported privately by several independent security researchers. Project maintainers had scheduled a fix for this specific issue to coincide with the planned GeoServer 3.0.1 release.
Unfortunately, the coordinated timeline was disrupted when a third party, entirely unconnected to either the core project development team or the original researchers who discovered the flaw, published the vulnerability details openly on social media. The fallout from this uncoordinated disclosure was immediate and severe. Automated threat intelligence and project telemetry indicated that malicious scans targeting this exact vulnerability began sweeping across the internet within mere hours of the social media post going live.
The speed and aggression of this opportunistic exploitation triggered swift media coverage and forced project leaders to issue an urgent, high-priority call to action across official user forums and communication channels. Project leadership publicly expressed gratitude to journalist Ravie Lakshmanan for first notifying project leadership regarding the active exploitation via the Open Source Geospatial Foundation. This intense episode reaffirmed the critical importance of strictly adhering to coordinated vulnerability disclosure policies and underscored why administrators must prioritize applying new patches the moment they are made available by the maintainers.
Previously Published CVEs and Release History
The summer security turbulence followed earlier advisories published on June 11, 2026, which coincided with the major release of GeoServer 3.0.0. Those earlier disclosures addressed multiple CVEs affecting various active branches, necessitating follow-up patches for versions such as GeoServer 2.27.3, 2.26.4, and the foundational GeoServer 2.27.0 release. Maintaining compatibility and security across multiple concurrent release lines demands significant coordination from the core development team, who balance introducing new features in major versions with backporting critical security fixes to older maintenance branches that many enterprise environments rely on for production stability.
Supply Chain Advisory Involving Infrastructure
Adding to the complexity of the summer security cycle, the project faced its first-ever infrastructure supply chain advisory. Because supply chain advisories have the potential to compromise the integrity of software downloaded by end users, the project team treated the situation with the utmost seriousness.
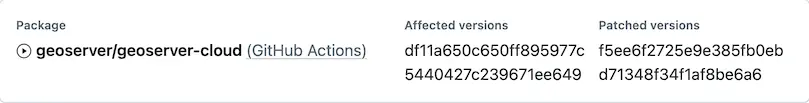
However, project maintainers clarified that no official GeoServer releases were impacted by this supply chain event. Official GeoServer releases are strictly compiled and published using a dedicated Jenkins build server that distributes authorized software artifacts to both SourceForge and the core OSGeo infrastructure. Instead, the advisory specifically affected the "geoserver/geoserver-cloud (GitHub Actions)" environment, which operates outside of the traditional release pipeline. Because the advisory did not correspond to an official release artifact of GeoServer itself, it did not qualify for a traditional CVE tracking number, but it nevertheless prompted transparent communication to ensure user trust and awareness.
The Wave of AI-Assisted Vulnerability Reports
Like many prominent open-source software projects across the global technology landscape, the GeoServer maintainers have noted a substantial increase in vulnerability reports generated with the assistance of artificial intelligence tools. While these tools can sometimes help identify potential code anomalies, they frequently produce large volumes of verbose, low-signal, or duplicate submissions that require significant manual effort from maintainers to triage, review, and verify.
In response to this administrative burden, the project has established a dedicated general AI Policy and updated its comprehensive GitHub Security Policy. These policy updates formally acknowledge the influx of AI-generated content and provide explicit guidance for researchers utilizing automated tools. Project maintainers emphasize that when researchers submit AI-assisted reports—which are often characterized by excessive length and complexity—being readily available to clarify technical details, test potential patches, and verify fixes is deeply appreciated. Navigating these reports consumes valuable developer time that could otherwise be spent on core feature development or proactive security hardening, making community collaboration essential.
Community Support and Engagement
As the project continues to navigate these evolving security challenges, maintainers have renewed their calls for broader community involvement. Organizations and commercial enterprises that depend heavily on GeoServer for critical geospatial infrastructure are encouraged to financially sponsor the project or allow their internal engineering staff to directly participate in the geoserver-security working group. Furthermore, the project is actively working to establish formal project membership pathways for public sector institutions and government agencies that often face regulatory or bureaucratic restrictions preventing traditional corporate sponsorship or direct community participation.
Addressing the Question of Upgrade Cadence
With modern software vulnerabilities evolving rapidly, system administrators frequently ask how often they should upgrade their deployments. GeoServer operates on a structured, time-boxed release cycle, rolling out designated stable and maintenance releases consistently over the course of each year.
To maintain a secure posture and ensure uninterrupted protection against newly discovered threats, maintainers strongly advise organizations to upgrade their GeoServer instances to a supported release at least once a year. Detailed technical instructions and step-by-step guidance for migrating between versions are fully documented in the official GeoServer User Guide under the section dedicated to upgrading existing installations.
For security researchers and administrators who suspect they have discovered a legitimate security flaw, the project continues to enforce strict private disclosure guidelines. Anyone wishing to report a vulnerability is instructed to review the official security policy and submit details privately using GitHub security advisories to ensure that fixes can be developed and tested before any public exposure occurs.




