
The GeoServer project has issued a comprehensive security recap covering a turbulent summer in 2026, highlighting a series of newly published Common Vulnerabilities and Exposures (CVEs), a notable supply chain advisory, and an unexpected zero-day exploit that forced the project’s maintainers into rapid action. In response to these developments, project leadership is strongly urging administrators managing GeoServer instances to update immediately to the newly released versions: GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6.
The summer events have underscored the critical importance of adhering to coordinated vulnerability disclosure policies. The GeoServer project traditionally follows a strict coordinated disclosure model, ensuring that security flaws are thoroughly addressed and fixed across both stable and maintenance release lines before any official CVE details or technical descriptions are made public. This established protocol is designed to provide organizations and system administrators with a crucial window of opportunity to apply patches and secure their infrastructure before malicious actors can weaponize the vulnerabilities. However, recent events during the summer months tested the limits of this coordinated approach, putting the project’s incident response capabilities to the test.
The August Zero-Day Incident
The most pressing security challenge of the season occurred in August, when GeoServer faced a high-profile zero-day vulnerability—an active exploit occurring in the wild for which no official patch had yet been publicly deployed. Prior to the public breach, the underlying security problem had already been responsibly identified and reported to the project privately by several independent security researchers. A formal software fix had already been scheduled and queued for inclusion in the upcoming GeoServer 3.0.1 release.
However, the containment strategy was disrupted when an unrelated third party—completely unconnected to either the GeoServer project or the original researchers who discovered the issue—decided to publicly disclose the vulnerability details on social media. The consequences of this premature disclosure were immediate and severe. Within hours of the social media post, automated security scans and malicious probes detecting and targeting the vulnerability were observed across the internet.
The sudden influx of hostile scanning prompted an emergency response from the GeoServer development and security teams. News coverage quickly picked up on the unfolding situation, amplifying an urgent call for administrators to update their software, which was broadcasted prominently across the official user forums. Project leadership formally acknowledged the rapid escalation and expressed gratitude to security researcher Ravie Lakshmanan for first notifying project leadership through the Open Source Geospatial Foundation.
The rapid deployment of GeoServer 3.0.1, alongside updated maintenance versions 2.28.5 and 2.27.6, mitigated the immediate threat. Nevertheless, project organizers noted that the incident serves as a stark reminder of why coordinated vulnerability disclosure is vital to the broader open-source ecosystem, and why community members must act quickly to adopt new releases as soon as they become available.
Previously Published CVEs and Release Management
The summer security recap also accounted for vulnerabilities identified earlier in the season. A series of CVEs were officially published on June 11, 2026, coinciding with the major rollout of the GeoServer 3.0.0 release. These historical advisories affected various earlier configurations, including dedicated updates directed at GeoServer 2.27.3, 2.26.4, and the initial 2.27.0 branch.
Managing these multifaceted security updates is an ongoing challenge for the project, which operates under a strict time-boxed release cycle. Over the course of any given year, the project maintains parallel "stable" and "maintenance" release tracks. To maintain adequate protection against known security flaws, administrators are advised to upgrade their operational GeoServer instances to a supported release at least once a year. Comprehensive guidance for managing these upgrades can be found within the official user installation documentation provided by the project.
Supply Chain Advisory and Infrastructure Security
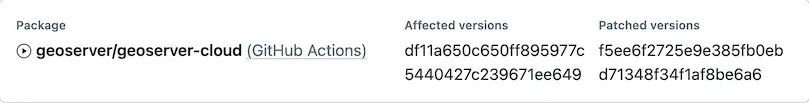
In addition to direct software vulnerabilities, the GeoServer project navigated its first-ever infrastructure-level supply chain advisory over the summer. Because this particular advisory affected the geoserver/geoserver-cloud repository on GitHub Actions rather than a direct downloadable source code release of GeoServer itself, it did not qualify for a standard CVE tracking number.
Project maintainers moved quickly to reassure the user base that no official GeoServer software releases were compromised or affected by the supply chain incident. Standard GeoServer software releases are compiled and distributed using an independent Jenkins build server, which publishes verified software artifacts directly to SourceForge and official Open Source Geospatial Foundation (OSGeo) infrastructure. The distinction highlights the complex nature of modern software supply chains, where ancillary development and continuous integration environments can face scrutiny independent of the core application code.
The Rise of AI-Assisted Vulnerability Reports
Another notable trend highlighted in the summer review is the surging volume of security vulnerability reports generated with the assistance of artificial intelligence. Like many other prominent open-source software projects, the GeoServer team has experienced a noticeable wave of AI-crafted submissions.
While automated tools can sometimes assist in security research, AI-generated reports often present distinct challenges for maintainers. These reports tend to be exceptionally verbose, requiring significant manual effort from core developers to review, parse, and determine whether individual submissions represent genuine vulnerabilities or redundant duplicate filings. Furthermore, verifying these theoretical claims and testing proposed fixes takes valuable time away from core feature development.
To address this shift in the security landscape, the GeoServer project has established a dedicated general AI policy and updated its overarching security policy. These framework updates acknowledge the proliferation of AI-generated content and provide clear guidance for researchers utilizing automated tools. The project has emphasized that when security researchers submit AI-assisted reports, being readily available on hand to clarify technical details, test proposed patches, and assist the security team greatly reduces the administrative burden on maintainers.
Community Support and Engagement
Securing a widely used open-source geospatial platform requires sustained collaboration between core developers, institutional users, and enterprise organizations. The GeoServer project continues to rely heavily on the active participation of its community to manage the heavy workload associated with maintenance, vulnerability triage, and patch verification.
Organizations whose operational workflows depend heavily on GeoServer are encouraged to consider financial sponsorship or to allow their internal technical staff to participate directly in the geoserver-security working groups and mailing lists. Additionally, the project is actively working to establish formal project membership pathways tailored for public institutions and government agencies that often face regulatory or administrative restrictions regarding direct financial sponsorship and corporate participation.
For individuals or organizations seeking to report newly discovered security issues responsibly, the project maintains clear, private reporting channels. Security vulnerabilities can be submitted confidentially through GitHub security advisories by consulting the official security policy documented in the main repository, ensuring that issues are addressed through proper channels before any public disclosure can impact production environments.




