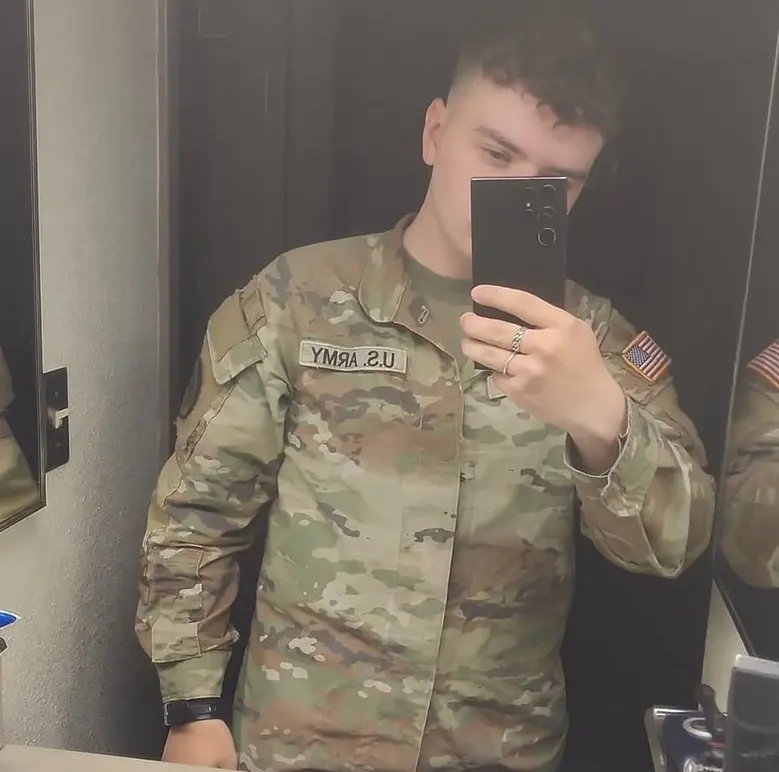
A U.S. Army soldier who pleaded guilty to hacking into multiple telecommunications companies and stealing mobile call and text metadata belonging to more than 100 million AT&T customers was sentenced to 70 months in federal prison today. In addition to the prison term handed down in a Seattle federal courtroom, the defendant was ordered to pay nearly $300,000 in restitution to his victims.
Cameron John Wagenius, 22, was stationed at a U.S. Army base in South Korea when he operated under the cybercriminal moniker “Kiberphant0m.” Working alongside a network of alleged co-conspirators, Wagenius exploited exposed credentials and systems that failed to enforce multi-factor authentication within cloud data storage service Snowflake. Snowflake has since mandated multi-factor authentication across all accounts following the sweeping wave of compromises.
By October 2024, Wagenius took to cybercrime forums to boast about his acquisition of call and text metadata—including source and destination numbers, timestamps, and call durations—for tens of millions of AT&T customers. His digital incursions extended far beyond a single telecommunications giant, ultimately touching more than a dozen telecom companies worldwide, including Verizon’s Push-to-Talk business. In these campaigns, Wagenius and his associates publicly extorted the affected corporations, leveraging the threat of publishing sensitive proprietary data in exchange for ransoms.
The digital trail leading to his unmasking began to take shape in late November 2025, when cybersecurity research publication KrebsOnSecurity warned that the persona Kiberphant0m likely belonged to a U.S. soldier stationed in South Korea. Less than a month after that reporting, Wagenius was arrested and faced two separate federal indictments. He swiftly pleaded guilty to all counts across both cases, culminating in today’s sentencing hearing where federal judges imposed a nearly six-year federal prison sentence alongside an order for $294,978 in restitution.
Federal prosecutors outlined that Wagenius did not operate in a vacuum, receiving assistance in his extortion plots from Kenneth Schuchman, a 28-year-old resident of Vancouver, Washington, with a substantial criminal history in the digital underground. Schuchman previously pleaded guilty in 2019 to operating the Satori botnet, a vast and dangerous collection of compromised Internet-of-Things devices leveraged to launch large-scale distributed denial-of-service attacks.
Meanwhile, other alleged co-conspirators tied to the Snowflake data thefts continue to navigate the legal system. Conor Riley Moucka, operating under the alias “Judische” in Kitchener, Ontario, was arrested in 2024 and entered a guilty plea in August 2026. Another co-conspirator, John Erin Binns, an American citizen currently residing in Turkey, remains wanted in connection with both the Snowflake incidents and a massive 2021 data breach at T-Mobile that compromised the personal information of at least 76 million customers.
The operations orchestrated by Wagenius also crossed dangerous lines into national security threats. Prosecutors revealed that Kiberphant0m resorted to re-extorting victims by threatening to release classified secrets. Immediately following the arrest of Moucka—and despite the fact that AT&T had already paid the extortion syndicate a $370,000 Bitcoin ransom—Wagenius published what he alleged were the AT&T call logs of then-President-elect Donald Trump and then-Vice President Kamala Harris on hacker forums. He also distributed documents and schematics allegedly stolen from the U.S. National Security Agency.
Paul Russell, resident agent in charge at the Defense Criminal Investigative Service, the criminal investigative arm of the U.S. Department of Defense Office of Inspector General, detailed the collaborative law enforcement response. Once the DCIS received intelligence suggesting an active-duty soldier holding a secret security clearance was embroiled in cybercrime and extortion, the agency launched a joint investigation alongside the FBI, the Army Criminal Investigative Division, and the U.S. Secret Service.
According to Russell, discovering an insider threat of this magnitude was extraordinarily rare. Law enforcement agencies quickly mobilized because the situation presented a unique security challenge where initial investigators could not immediately measure the full scope of the compromise.
Even while incarcerated and awaiting his day in court, Wagenius continued to test the boundaries of institutional security. A sentencing memo filed by federal prosecutors in Seattle revealed that Wagenius was caught attempting to probe the computer network of the Bureau of Prisons for vulnerabilities. While residing in a correctional facility, Wagenius utilized another inmate’s email system to prompt commercial artificial intelligence tools to reveal Windows 10 Enterprise privilege escalation CVEs and working exploit scripts.
Records from the Bureau of Prisons indicated that Wagenius subsequently leveraged another inmate’s account to search for step-by-step instructions and code for CVE-2023-45208, a legacy command injection vulnerability affecting D-Link networking devices. During the same timeframe, Wagenius sought instructions on how to construct a makeshift prison-yard antenna using commissary items to extend radio reception, alongside queries regarding prison escape methods.
Prosecutors noted that Wagenius framed many of these AI queries within the context of researching a book he claimed to be writing. Investigators identified this tactic as a classic example of prompt injection, a method where attackers supply deceptive inputs to bypass commercial AI safety guardrails designed to prevent the generation of actionable exploit code. Although the government found no evidence that Wagenius successfully deployed these vulnerabilities against the prison system’s internal networks, his ongoing inquiries underscored a persistent digital risk. When confronted by authorities, Wagenius claimed he was merely exploring vulnerabilities to hand information over to the Bureau of Prisons.
Despite the sweeping nature of the data he and his co-conspirators accumulated from AT&T and other telecom providers, financial audits of the operation revealed that the enterprise was remarkably unsuccessful in monetizing its efforts. The government’s sentencing memo estimated that Wagenius accumulated a total of roughly $1,500 from direct sales of stolen corporate data.
Concluding their assessment in the sentencing memorandum, prosecutors emphasized the stark contrast between his monetary gain and the widespread impact of his actions, noting that while Wagenius was not particularly financially successful as a cybercriminal, he both intended to and caused significant harm to numerous individual victims, major U.S. corporations, and the United States government.