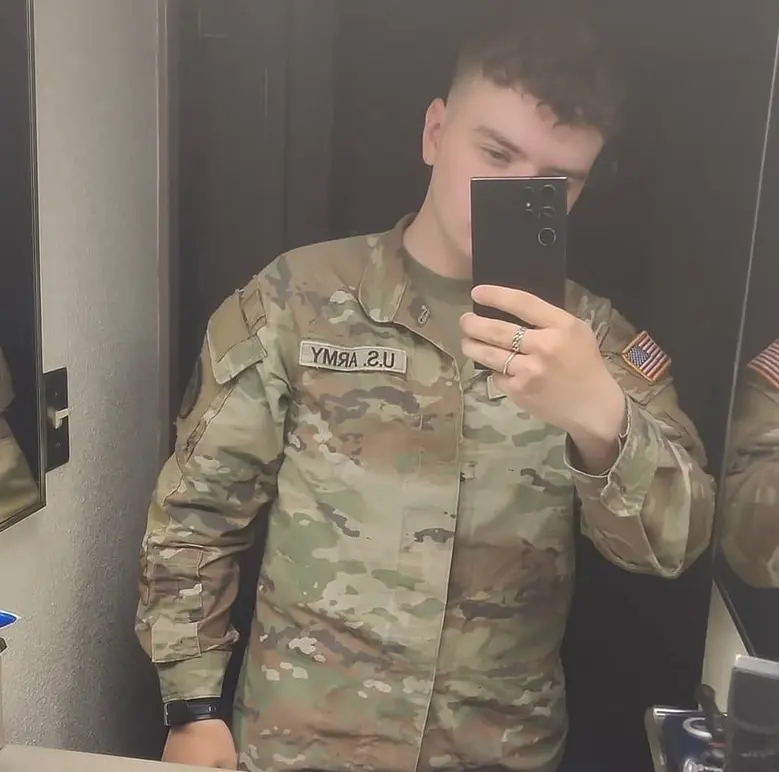
A United States Army soldier who pleaded guilty to hacking into multiple telecommunications companies and stealing mobile call and text metadata belonging to more than 100 million AT&T customers was sentenced in a federal courtroom to 70 months in prison. In addition to the nearly six-year federal prison sentence, the defendant was ordered to pay nearly $300,000 in restitution to his victims, bringing a significant chapter of a high-profile international cyber extortion investigation to a close.
Cameron John Wagenius, a 22-year-old soldier who was stationed at a U.S. Army base in South Korea at the time of his offenses, operated under the online cybercriminal persona "Kiberphant0m." Operating within shadowy digital underground forums, Wagenius collaborated with a network of alleged co-conspirators to exploit vulnerabilities tied to cloud data storage provider Snowflake. According to federal investigators, the group targeted large enterprise customers of the platform that had left credentials exposed and failed to enforce multi-factor authentication, a security lapse that Snowflake has since addressed by mandating multi-factor authentication across all accounts.
The breadth of the operation began to surface publicly in October 2024, when Kiberphant0m took to cybercrime forums to boast about a massive data theft. The hacker claimed to have exfiltrated call and text metadata—including source and destination telephone numbers, timestamps, and call durations—for tens of millions of AT&T customers. Furthermore, Kiberphant0m asserted that he had successfully breached more than a dozen telecommunications companies worldwide, including Verizon’s Push-to-Talk business, and proceeded to publicly extort these corporate entities under the threat of publishing the sensitive proprietary data online.
The investigation accelerated significantly in late November 2025, when independent security journalism by KrebsOnSecurity warned that the individual operating behind the Kiberphant0m handle was likely a U.S. service member stationed in South Korea. Less than a month after those reports surfaced, Wagenius was apprehended and subsequently faced two separate federal indictments. Demonstrating early cooperation with authorities, he quickly pleaded guilty to all counts across both legal cases.
During his sentencing hearing in Seattle, federal judges handed down the nearly six-year prison term alongside an order to remit $294,978 in restitution. Federal prosecutors outlined that Wagenius did not operate in a vacuum, detailing his collaboration with Kenneth Schuchman, a 28-year-old resident of Vancouver, Washington, who possesses a substantial history in the cybercrime underworld. Schuchman previously pleaded guilty in 2019 to operating the Satori botnet, a massive collection of compromised Internet-of-Things devices weaponized to launch large-scale distributed denial-of-service attacks against global targets.
Wagenius also shared associations with other prominent digital figures facing legal scrutiny in connection with the Snowflake data thefts. Among them is Conor Riley Moucka, also known online as "Judische," a resident of Kitchener, Ontario, who was arrested in 2024 and entered a guilty plea in August 2026. Another co-conspirator named in the broader investigations is John Erin Binns, an American citizen currently residing in Turkey, who has also been wanted by law enforcement for his alleged role in a massive 2021 data breach at T-Mobile that exposed the personal identifying information of at least 76 million customers.
As the extortion campaign progressed, Kiberphant0m’s tactics grew increasingly aggressive, expanding into re-extorting victims and threatening to leak sensitive national security secrets. Immediately following the arrest of Moucka—and despite the fact that AT&T had already paid the extortion syndicate a Bitcoin ransom valued at $370,000—Kiberphant0m published files on hacker forums. He claimed these files contained AT&T call logs belonging to then-President-elect Donald Trump and then-Vice President Kamala Harris, alongside digital schematics alleged to have been stolen from the U.S. National Security Agency.
The unique and alarming nature of the case mobilized a multi-agency federal response. Paul Russell, a resident agent in charge at the Defense Criminal Investigative Service, the criminal investigative arm of the U.S. Department of Defense Office of Inspector General, detailed how the investigation unfolded. Russell explained that once the DCIS received actionable intelligence indicating that an active-duty soldier holding a secret security clearance was actively engaged in cybercrime and extortion, a joint operation was swiftly established alongside the Federal Bureau of Investigation, the Army Criminal Investigative Division, and the U.S. Secret Service.
"We don’t often get leads where there’s an active duty soldier with a secret clearance who’s creating hacking tools and trafficking in data," Russell noted, reflecting on the severity of the threat. "That doesn’t happen every day, and so when that hits it really spins all of our partner organizations up. It was very serious from jump street, just because it was unique, it was an insider threat, and we weren’t sure what we were dealing with."
Despite his quick guilty plea and subsequent cooperation with federal prosecutors, details emerged in a sentencing memorandum filed by the government in Seattle indicating that Wagenius continued his illicit technical pursuits even while incarcerated and awaiting sentencing. The government’s filing revealed that Wagenius had violated the computer use policies of the Federal Bureau of Prisons in an apparent attempt to probe vulnerabilities within the prison system’s internal computer network.
According to records compiled by the Bureau of Prisons, Wagenius utilized another inmate’s email system around September 2025 to instruct an email recipient to prompt a commercial artificial intelligence tool. The queries specifically asked for vulnerabilities related to Windows 10 Enterprise privilege escalation, requesting specific identifiers and functional working scripts without omitted code. Less than a week later, utilizing a different inmate’s email account, Wagenius allegedly directed another AI prompt query toward a three-year-old command injection vulnerability affecting D-Link networking devices, requesting detailed exploitation steps and associated functional code.
During the same period, Wagenius also sought instructions on how to construct a makeshift radio antenna using prison commissary items or readily available tools to extend reception, alongside inquiries concerning how to execute a prison escape. Prosecutors noted that Wagenius frequently framed these AI queries as background research for a book he claimed to be writing. Federal authorities described this tactic as a classic example of prompt injection, a method where attackers supply deceptive inputs to bypass commercial AI safety guardrails designed to prevent the generation of actionable exploitation code.
While the government acknowledged that it found no evidence Wagenius successfully deployed or utilized these researched vulnerabilities within Bureau of Prisons systems—with the defendant claiming during questioning that he was merely researching potential weaknesses to report them to prison authorities—the behavior underscored a persistent technical fixation.
Ironically, despite the immense scale of the data exfiltrated from major corporate entities like AT&T, the financial return for Wagenius’s extensive cybercriminal enterprise was remarkably low. According to the government’s sentencing memorandum, Wagenius managed to net a total of only around $1,500 from selling portions of the stolen data.
"While Wagenius was not particularly financially successful as a cybercriminal, he both intended to and caused significant harm to numerous individual victims, U.S. companies, and the U.S. government," the federal sentencing memo concluded.