
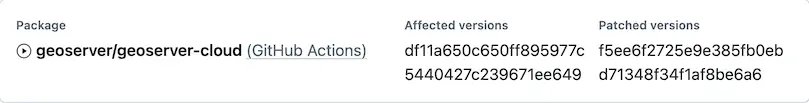
The GeoServer open-source project has released a comprehensive security recap detailing a turbulent summer of 2026, which included managing a critical zero-day exploit, addressing previously published Common Vulnerabilities and Exposures (CVEs), handling a software supply chain advisory, and adapting to a sharp rise in AI-generated security reports. Project maintainers are urging all administrators of GeoServer instances to upgrade immediately to the latest patched versions to safeguard their systems against active threats.
Administrators overseeing GeoServer deployments are instructed to transition without delay to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6. These maintenance and stable releases contain critical fixes designed to close security gaps that have emerged over recent months.
Traditionally, the GeoServer project operates under a strict coordinated vulnerability disclosure policy. This policy is designed to ensure that security flaws are patched across both stable and maintenance releases before any technical details or CVE identifiers are made public. The underlying philosophy of this approach is to give system administrators, organizations, and infrastructure operators a fair and adequate opportunity to apply updates and secure their environments prior to malicious actors weaponizing the vulnerabilities. However, recent events during the summer months tested the limits of this coordinated approach, highlighting the volatility of modern software maintenance and the speed at which unpatched systems can become targets.
August Zero-Day Incident
The most significant security challenge of the period occurred in August, when GeoServer was struck by a zero-day vulnerability—an actively exploited flaw in the wild for which no official patch had yet been publicly released. Prior to the incident, the underlying problem had already been reported privately to project maintainers by several independent researchers. A fix had been scheduled for inclusion in the upcoming GeoServer 3.0.1 release, adhering to the standard responsible disclosure timeline.
The zero-day crisis materialized when a third party, entirely unconnected to the GeoServer project and independent of the original researchers who discovered the issue, publicly disclosed the vulnerability on social media. The fallout was instantaneous. Within hours of the public social media post, automated scanners and threat actors began actively probing networks for vulnerable GeoServer instances.
The velocity of this malicious response caught the attention of the broader cybersecurity community, triggering widespread news coverage and prompting an urgent call to action on the official GeoServer user forums. Project leadership formally acknowledged the rapid escalation and expressed gratitude to researcher Ravie Lakshmanan for initially notifying project leadership via the Open Source Geospatial Foundation. The swift deployment of GeoServer 3.0.1, alongside the corresponding updates in versions 2.28.5 and 2.27.6, helped mitigate the immediate fallout. Nevertheless, the incident served as a stark reminder of the risks posed by premature public disclosures and reinforced the critical importance of adhering to coordinated vulnerability disclosure timelines while urging the community to patch systems immediately upon release.
Previously Published CVEs
The summer security updates also encompassed a series of vulnerabilities published earlier in the season. On June 11, 2026, coinciding with the major rollout of the GeoServer 3.0.0 release, project maintainers published several CVEs affecting earlier iterations of the software. These included specific security adjustments integrated into GeoServer 2.27.3 and 2.26.4, as well as baseline updates associated with GeoServer 2.27.0. These mid-year releases formed part of the project’s routine maintenance schedule, aimed at addressing technical debt, resolving lingering bugs, and hardening the platform against evolving threat vectors.
Supply Chain Advisory and Infrastructure Integrity
In addition to direct software vulnerabilities, the GeoServer project navigated its first-ever infrastructure supply chain advisory during the summer period. Supply chain advisories carry inherent risks because they have the potential to compromise the integrity of software artifacts downloaded by end users.
Because this particular advisory did not correspond to a direct code release of GeoServer itself, it was categorized distinctly as a "geoserver/geoserver-cloud (GitHub Actions)" advisory. Consequently, it did not qualify for a traditional CVE number. Project leaders emphasized a vital distinction for users: no official GeoServer releases were impacted by the supply chain incident. Standard GeoServer releases are compiled and distributed using a dedicated Jenkins build server, which publishes verified artifacts securely to both SourceForge and official OSGeo infrastructure, maintaining a strict barrier between development pipelines and production software distribution.
AI-Assisted Vulnerability Reports and Policy Updates
Like many other prominent open-source software projects, the GeoServer maintainers have reported experiencing a massive influx of vulnerability reports generated with the assistance of artificial intelligence tools. While AI technologies can sometimes assist in identifying code anomalies, they frequently produce large volumes of verbose, repetitive, or inaccurate submissions that require significant manual triage by core developers.
To manage this growing administrative and technical burden, the project has established a formal general AI policy and updated its core security policy. These framework updates are designed to acknowledge the modern reality of AI-assisted security research and provide clear guidance to researchers utilizing these tools. Maintainers have noted that because AI-generated reports tend to be overly verbose, researchers who submit such findings are strongly encouraged to remain available to clarify technical details, help determine if reports represent duplicate findings, and assist in testing and verifying fixes as they are developed. Streamlining this review process is vital to reducing the workload on the volunteer-driven geoserver-security team.
Community Support and Upgrade Cadence
As the GeoServer project continues to navigate these security challenges, project leadership has emphasized the importance of community involvement. Organizations that rely heavily on GeoServer for critical geospatial infrastructure are encouraged to consider financial sponsorship or to allow their technical staff to participate directly in the work of the geoserver-security team. Additionally, the project is working to establish formal project membership pathways for public institutions that may face bureaucratic or legal restrictions regarding corporate sponsorship and direct participation.
To maintain robust security postures, GeoServer operates on a time-boxed release cycle that spans a full calendar year, maintaining distinct stable and maintenance releases. Maintainers strongly advise all users to upgrade their installations to a supported release at least once every twelve months to ensure continuous access to security patches and bug fixes. Comprehensive documentation and step-by-step instructions for transitioning between versions are maintained within the official GeoServer User Guide.
Anyone discovering a new potential security vulnerability within the platform is advised to review the project’s security policy and submit their findings privately through GitHub security advisories, ensuring that the principles of coordinated disclosure continue to protect the global user base.




