
The open-source geospatial community has faced a demanding summer of security maintenance, culminating in an urgent call for administrators to patch their systems following a turbulent zero-day disclosure in August. Project maintainers have released a comprehensive security recap detailing the recent vulnerabilities, an infrastructure supply chain advisory, and a newly formalized policy addressing the growing influx of AI-assisted vulnerability reports.
For organizations running enterprise mapping and geospatial data servers, the immediate imperative is clear. Administrators are strongly urged to update their deployments to the latest patched versions: GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6. These releases contain critical fixes designed to protect instances from active exploitation and ensure long-term stability across both stable and maintenance branches of the software.
The GeoServer project traditionally adheres to a strict coordinated vulnerability disclosure policy. Under this framework, security flaws are identified, analyzed, and patched for both stable and maintenance releases in a private environment before any Common Vulnerabilities and Exploits details are made public. The underlying philosophy of this approach is to provide system administrators with a crucial window of opportunity to apply updates and safeguard their infrastructure before malicious actors become aware of the specific mechanics of a vulnerability.
However, this deliberate rhythm was disrupted in August when GeoServer confronted its first major zero-day situation of the year—an active exploit in the wild operating without a known public fix at the time of discovery. The core issue had already been reported privately through proper channels by several independent researchers, and developers had naturally scheduled a fix to be bundled into the upcoming GeoServer 3.0.1 release.
The security landscape shifted rapidly when an unrelated third party, entirely disconnected from both the project development team and the original reporting researchers, publicly disclosed the vulnerability on social media. The consequences were immediate and severe. Automated scans searching for vulnerable instances were detected across the internet within hours of the public social media post going live.
The sheer speed of the hostile response generated widespread industry attention, prompting prominent news coverage and immediate emergency warnings broadcast across the official GeoServer user forums. Project leadership expressed gratitude to security researcher Ravie Lakshmanan for first notifying project leadership regarding the unfolding situation via the Open Source Geospatial Foundation. This high-pressure episode forcefully reaffirmed the critical necessity of adhering to coordinated disclosure practices and highlighted why system administrators must act swiftly to apply security patches the moment new versions are made publicly available.
Beyond the August zero-day event, the summer recap also accounted for previously published CVE disclosures that emerged earlier in the season. On June 11, concurrent with the major rollout of the GeoServer 3.0.0 release, developers published several CVEs affecting earlier iterations of the software, prompting corresponding updates for versions 2.27.3, 2.26.4, and 2.27.0. These routine maintenance updates are part of the project’s ongoing commitment to closing security gaps as they are identified by the developer community and external auditors.
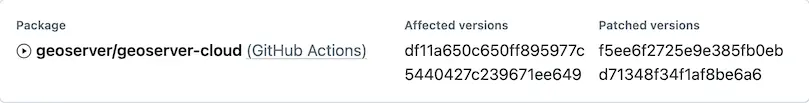
In addition to direct software vulnerabilities, the summer review addressed a distinct supply chain advisory that tested the project’s operational resilience. Supply chain advisories inherently carry the potential to undermine the integrity of downloaded software, making them a top priority for open-source maintainers. This particular incident marked the first time the GeoServer project has had to navigate an infrastructure advisory of this nature. Because the advisory did not correspond to a standard software release of GeoServer itself—stemming instead from a GitHub Actions workflow within the geoserver/geoserver-cloud repository—it did not qualify for a traditional CVE number.
Project maintainers emphasized a crucial point of reassurance for the user base: no official GeoServer releases were compromised or affected by the incident. Standard GeoServer releases are compiled and published through an independent Jenkins build server that distributes trusted artifacts directly to SourceForge and the Open Source Geospatial Foundation infrastructure, keeping the core distribution channels secure.
Another significant development over the summer has been the management of an escalating volume of vulnerability reports generated with the assistance of artificial intelligence. Like many prominent open-source software projects, GeoServer has experienced a noticeable wave of security submissions drafted by AI tools. These automated or semi-automated reports often present unique challenges for maintainers because they tend to be exceptionally verbose, frequently obscure the core technical mechanics behind walls of generated text, and complicate the process of filtering out duplicate submissions.
To adapt to this technological shift, the project has established a general AI Policy and updated its formal Security Policy hosted on GitHub. These updated guidelines explicitly acknowledge the integration of AI tools into the vulnerability reporting ecosystem and provide clear instructions for researchers utilizing them. Maintainers have noted that because AI-generated reports often require extensive human review to validate, having reporters on hand to clarify technical ambiguities is immensely helpful. Furthermore, security team members appreciate when reporters are positioned to test and verify proposed fixes, as any assistance in streamlining the review workflow helps alleviate the burden on the dedicated geoserver-security team.
As the project looks toward maintaining long-term security and sustainability, leadership has outlined several ways for the broader community to contribute. Organizations that rely heavily on GeoServer for mission-critical geospatial operations are encouraged to consider financial sponsorship or to authorize their internal technical staff to participate directly in the geoserver-security work groups. Additionally, the project is actively working to establish formal project membership structures for public institutions and government agencies that often face regulatory restrictions preventing traditional corporate sponsorship or direct participation.
Addressing common maintenance questions, project maintainers stress the importance of maintaining a regular upgrade cadence. GeoServer operates on a time-boxed release cycle, actively supporting stable and maintenance releases over the course of a year. System administrators are strongly advised to upgrade their deployments to a supported release at least once every year to ensure they continue receiving vital security patches and bug fixes. Comprehensive instructions and upgrade paths are documented extensively within the official GeoServer User Guide to assist administrators through the transition process.
For security researchers and system operators who discover potential vulnerabilities in the future, the project maintains a strict private disclosure protocol. Rather than resorting to public forums or social media prematurely, individuals are instructed to consult the official security policy repository on GitHub for step-by-step guidance on submitting vulnerability reports privately through GitHub security advisories, ensuring that the coordinated disclosure model can protect the global geospatial community effectively.




