
The GeoServer project has released a comprehensive security recap detailing a tumultuous summer of vulnerability disclosures, a high-profile zero-day exploit, a supply chain warning, and a formal policy update addressing the rising tide of artificial intelligence-generated security reports. Administrators managing GeoServer instances are being urged to apply the latest patches immediately to safeguard their mapping infrastructure against active exploitation.
The core message for system administrators and IT professionals responsible for geospatial deployments is straightforward: upgrade immediately. The project team has rolled out targeted patches across multiple release lines, resulting in the availability of GeoServer version 3.0.1, GeoServer version 2.28.5, and GeoServer version 2.27.6. These updates close critical security gaps that have emerged over the past several months and incorporate fixes that were originally scheduled for staggered deployment before external events forced an acceleration of the timeline.
GeoServer has long maintained a strict coordinated vulnerability disclosure policy. Under this framework, security vulnerabilities are privately reported, analyzed, and fixed across both stable and maintenance releases before any Common Vulnerabilities and Exposures (CVE) details are made publicly available. The primary objective of this protocol is to give organizations adequate breathing room to apply necessary updates before malicious actors can weaponize the underlying source code flaws. However, maintaining this controlled release schedule faced a significant hurdle during the summer months due to unexpected external disclosures.
The August Zero-Day Incident
The security landscape shifted dramatically in August when GeoServer confronted an active zero-day vulnerability—an exploit operating in the wild with no official software patch publicly available at the exact moment of disclosure. Prior to the public leak, the underlying problem had already been responsibly reported through private channels by several independent security researchers, and project maintainers had neatly scheduled a fix to coincide with the planned deployment of GeoServer 3.0.1.
The emergency situation materialized because an unconnected third party—completely separate from the core development project and entirely removed from the original reporting researchers—publicly disclosed technical details of the vulnerability on social media. The fallout was swift and measurable. Automated scanning tools and malicious actors began probing public-facing infrastructure for this specific vulnerability within mere hours of the social media post going live.
The rapid escalation triggered immediate media coverage and prompted the project leadership to issue an urgent call to action across official user forums and communication channels. Project representatives expressed public gratitude to security researcher Ravie Lakshmanan, who first notified project leadership through the Open Source Geospatial Foundation, helping coordinate the rapid response that followed. The intense pressure of the August zero-day event powerfully reaffirmed why maintaining a coordinated vulnerability disclosure policy is vital, and why users must act decisively when new maintenance and security releases are published.
Previously Published CVEs and Release Cycles
The summer security recap also reflected upon vulnerabilities disclosed earlier in the season. On June 11, 2026, a series of CVEs were published to coincide directly with the major feature release of GeoServer 3.0.0. These earlier disclosures prompted immediate updates across the ecosystem, notably impacting maintenance branches such as GeoServer 2.27.3, 2.26.4, and the initial 2.27.0 branch.
To help administrators navigate this continuous stream of updates, the GeoServer project operates on a time-boxed release cycle. Over the course of any given year, the project maintains parallel "stable" and "maintenance" release branches. Project maintainers strongly recommend that organizations upgrade their deployments to a supported, active release at least once a year to ensure continuous receipt of critical security fixes and patches. Upgrading existing versions requires following established guidelines detailed in the project’s official user documentation, ensuring that map servers remain resilient against newly discovered attack vectors.
Supply Chain Security and Infrastructure Adherence
Beyond application-level source code vulnerabilities, the GeoServer project encountered its first major supply chain advisory during the summer review period. Supply chain advisories inherently carry the potential to disrupt trust in software integrity, raising concerns about whether downloaded binaries or artifacts have been tampered with during the build and distribution pipeline.
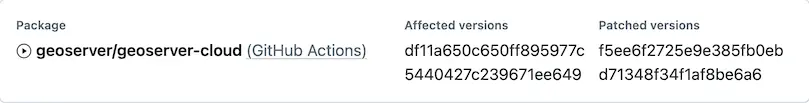
In this specific instance, the advisory was officially categorized under GitHub Actions affecting the geoserver/geoserver-cloud repository structure. Because the advisory did not correspond to a standard, official release of the core GeoServer software package, it did not qualify for a formal CVE designation. Most importantly, project leadership confirmed that no official GeoServer releases were compromised or affected by this supply chain event. Authentic GeoServer releases are strictly compiled and published using an isolated Jenkins build server, which pushes verified distribution artifacts simultaneously to SourceForge and official OSGeo infrastructure.
Managing AI-Assisted Vulnerability Reports
Like numerous other open-source software foundations and enterprise development teams worldwide, the GeoServer security team has experienced a noticeable surge in vulnerability reports generated with the assistance of artificial intelligence tools. These automated and AI-generated reports often exhibit extreme verbosity, creating significant review overhead for maintainers who must carefully analyze the text, determine authenticity, and filter out false positives or duplicate submissions.
To adapt to this modern phenomenon, the GeoServer project has established a dedicated general AI policy and updated its core security policy guidelines. These formal documentation updates acknowledge the widespread utilization of automated security tools and provide clear expectations for external contributors who lean on AI to scan and report codebases. Project leadership notes that when dealing with verbose AI-generated submissions, having reporters on hand to clarify technical ambiguities, test proposed patches, and verify remediation efforts is immensely helpful. Managing these reports demands considerable human capital; consequently, any assistance from the community in triaging, testing, and confirming fixes directly alleviates the burden on the core security team.
Community Involvement and Reporting Protocols
Securing an enterprise-grade open-source project used globally across government agencies, scientific institutions, and private enterprises requires sustained community backing. Project organizers emphasize that organizations heavily dependent on GeoServer for critical spatial data infrastructure should actively consider financial sponsorship or direct staff participation in security work via the official geoserver-security list. Furthermore, the project is working to establish specialized project membership frameworks tailored for public institutions and government agencies that frequently face administrative or legal restrictions regarding corporate sponsorship and direct open-source contributions.
For security researchers and administrators who discover potential vulnerabilities in future cycles, the GeoServer project maintains a transparent reporting protocol. Detailed instructions are hosted within the project’s security policy on GitHub, directing individuals to submit findings privately utilizing GitHub security advisories rather than disclosing details prematurely on public forums or social media platforms.




