Federal law enforcement agents have arrested the co-founder of a prominent Canadian cybersecurity firm in connection with an expanding international investigation into the notorious "ShinyHunters" hacking syndicate. The syndicate recently made headlines by breaching federal networks and obtaining sensitive personal and professional data concerning thousands of law enforcement personnel.
The arrest of 54-year-old Edward Dubrovsky took place in Pennsylvania, according to multiple sources familiar with the matter and federal court documentation. The operation coincides with a centralized push by the Federal Bureau of Investigation, which has consolidated command of the multifaceted ShinyHunters probe into a specialized field office located in Texas. Although FBI Director Kash Patel acknowledged the apprehension of a Canadian suspect in an official statement on social media, federal authorities have largely kept specific details under wraps, declining to offer additional comments as the investigation continues to unfold at a rapid pace.
According to background gathered from multiple sources close to the unfolding case, Dubrovsky had traveled to Pennsylvania to participate in a high-profile industry gathering known as the Cyber Risk Summit, which took place at the Loews Philadelphia Hotel. Dubrovsky’s professional background includes a prominent career in cybersecurity, notably as the co-founder of Cypfer, a Canadian security organization that frequently acts as a primary sponsor for risk management summits and specializes in navigating complex ransomware negotiations alongside digital extortion advisory services. More recently, Dubrovsky transitioned his professional focus to another security firm and event sponsor known as CyberSteward.

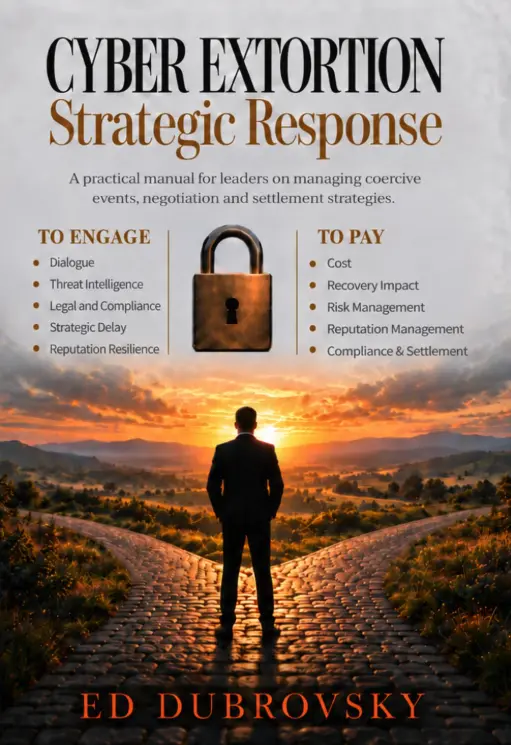
Digital footprints left across professional networking platforms indicate that Dubrovsky had publicly anticipated his attendance at the Pennsylvania conference alongside his colleagues. In a social media post published roughly one month prior to his arrest, he expressed enthusiasm for continuing industry dialogues surrounding global strategies for dealing with compliance-driven coercive tactics, ransomware threats, and settlement advisory services. Furthermore, Dubrovsky is recognized within the cybersecurity community as an author who has published literature detailing the strategic responses required when confronting cyber extortion, focusing heavily on the intricate decision-making processes organizations must navigate during digital crises.
Federal court dockets reveal that an individual under the name Edward Dobrovsky—featuring a slight spelling variation from his standard professional name—was taken into custody on October 8. The initial charges filed against him include conspiracy to threaten to impair the confidentiality of information with the intent to extort money, alongside charges related to interference with commerce by threats. While the core complaint and several associated documents have been placed under seal by the court, basic tracking details indexed through legal databases confirm his detention.
Initial records from the U.S. Bureau of Prisons confirmed that Dubrovsky was held at a federal facility in Philadelphia following his apprehension. However, judicial notices filed shortly thereafter initiated a transfer of the case to the U.S. District Court for the Eastern District of Texas, which sources indicate has become the primary operational hub for the government’s comprehensive crackdown on the ShinyHunters network. Available court documentation indicates that Dubrovsky has yet to secure legal representation or have a public defender formally appointed by the court. Attempts to reach Dubrovsky for comment immediately following his detention were unsuccessful, and representatives for CyberSteward have not yet issued formal statements regarding the situation.
The investigation into Dubrovsky forms part of a much broader, highly aggressive federal campaign directed at dismantling the ShinyHunters hacking group. Operating primarily through sophisticated phishing campaigns and the acquisition of compromised credentials, the syndicate routinely targets software-as-a-service companies to siphon confidential data from corporate repositories. The group then leverages the threat of public data exposure to extract massive financial settlements from corporate victims. According to estimates provided by federal law enforcement, the hacking collective has successfully extorted upwards of $70 million from various organizations over the course of the year.

Pressure on the cybercrime collective has mounted significantly in recent weeks following a series of international law enforcement actions. Last month, Dutch police apprehended Pepijn van der Stap, a reformed hacker suspected of maintaining deep ties to the syndicate, seizing a vast array of electronic devices that federal investigators have been meticulously analyzing. Sources familiar with the ongoing trajectory of the investigation suggest that these seized devices have provided a wealth of intelligence, hinting that additional criminal charges against principals at other firms specializing in ransomware negotiations could be imminent.
The fallout from these law enforcement actions has triggered aggressive retaliatory behavior from remaining members of the hacking collective. Immediately following the arrest executed by Dutch authorities, an operative utilizing the alias "Rey" assumed operational control of the ShinyHunters infrastructure. In an unprecedented escalation, the group began taunting federal investigators online, publicly boasting about a security breach that compromised the FBI’s online recruitment portal. This specific intrusion yielded highly sensitive records containing personal identifiers, unit assignments, professional specializations, and confidential medical and psychiatric histories of numerous agents.
Journalistic reports from outlets such as Reuters subsequently identified the operative known as Rey as a teenager named Saif Al-din Khader. Investigators quickly tracked the young hacker, leading to his detention and subsequent cooperation with federal authorities. The apprehension occurred as the cybercrime group attempted to execute an extortion campaign against a digital aviation and navigation unit that had recently been spun off from Boeing.
As federal authorities continue to parse through seized digital evidence and evaluate the cooperation of key informants, legal proceedings related to the broader conspiracy are expected to accelerate. Law enforcement agencies maintain that the multi-jurisdictional dragnet remains active, with further developments anticipated as the Justice Department builds its case against the network of individuals allegedly facilitating and negotiating digital extortion schemes.